authenticity

AppWizard
October 10, 2026
The game Nivalis Nights is designed to be intentionally overwhelming at the start, reflecting the stress of a cyberpunk world without traditional elements like player death or boss fights. Players navigate a chaotic environment where every app demands attention, mirroring modern life's pace. The game allows for various paths to success, including unconventional achievements, and emphasizes the complexity of relationships through its dating mechanics, aiming for authenticity and unpredictability. The game's narrative explores themes of technological advancement and societal pressures, inviting players to actively engage rather than passively receive rewards.
Tech Optimizer
October 10, 2026
In gaming, tools such as utilities, beta applications, and modding tools are often distributed as APK, IPA, or desktop files, and it is essential to investigate their origin, version, and any security warnings before installation. Antivirus software flags potential threats based on known malicious signatures, behavior patterns, and reputation data. Tools that modify game clients may receive heightened scrutiny, and classifications like “HackTool” or “Riskware” do not definitively indicate a file's functionality. Identical game utilities can exist on various platforms, and a familiar website does not guarantee authenticity. It is crucial to verify the publisher, update date, version, and installation method of a file. The SHA-256 hash verifies file integrity but does not ensure safety from malware. Calculating a file hash can be done using specific commands in Windows, macOS, or Linux. Multi-engine scanning platforms like VirusTotal provide insights, but a lack of detections does not guarantee safety. Even if a file matches its reference hash and raises no alerts, it may still violate online game terms. A pre-installation checklist includes confirming the publisher, checking file types, comparing SHA-256 hashes, reviewing security findings, keeping antivirus protection enabled, and consulting platform rules. A cautious approach integrates source verification, file integrity checks, security assessments, and compliance with platform regulations.
Tech Optimizer
October 7, 2026
Many VPN providers are now offering additional security features such as malware detection, malicious link checkers, and ad blockers, alongside their primary function of encrypting internet traffic. Notable VPNs like NordVPN and Surfshark have integrated real-time malware protection, with NordVPN becoming the first VPN to receive certification as a reliable anti-phishing tool in 2024. Surfshark's Surfshark One package offers comprehensive real-time protection from viruses and malware. Other VPNs, such as Avira and CyberGhost, utilize shared infrastructures for antivirus capabilities, which can lead to delays in updates and inconsistent platform support. Microsoft Defender has improved significantly, blocking 95.5% of live threats according to AV-Comparatives, while Apple employs multiple defenses in macOS, including Gatekeeper and XProtect, to manage malware threats. Avast Free Antivirus has achieved a perfect 100% block rate in recent testing but comes with limitations compared to paid antivirus suites like Norton 360 Deluxe and Bitdefender Total Security, which offer additional features such as password managers and identity monitoring. A layered approach to digital security, combining a VPN, free antivirus, and built-in OS-level security, is recommended for effective protection. Relying solely on one layer leaves potential gaps, as a VPN cannot detect existing malware, and free antivirus solutions may lack advanced features. Users managing sensitive data or frequent financial transactions should consider investing in premium antivirus suites for enhanced security.
AppWizard
October 6, 2026
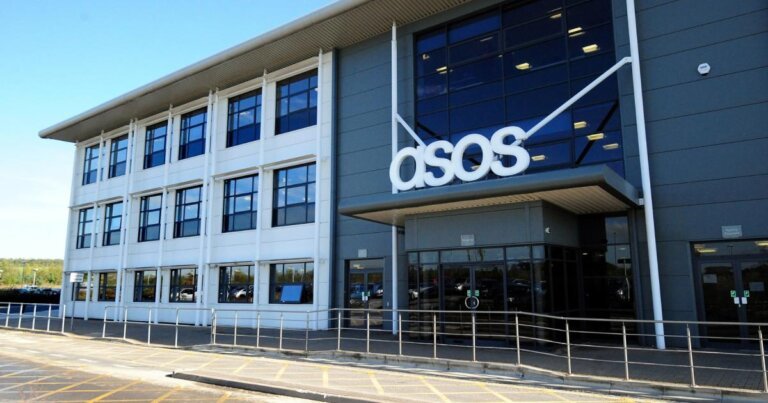
ASOS customers received a notification titled 'ASOS HACKED,' stating that the company's Snowflake instance had been compromised and threatening to leak data unless the company engaged with the sender. Many users expressed confusion on social media, questioning the legitimacy of the notification and speculating it could be a marketing strategy. ASOS has not yet commented on the situation.
BetaBeacon
October 3, 2026
Nintendo released Pictonico!, a game where players can turn their own pictures into mini WarioWare-style games, resulting in chaotic and fun challenges based on the photos.
AppWizard
September 29, 2026
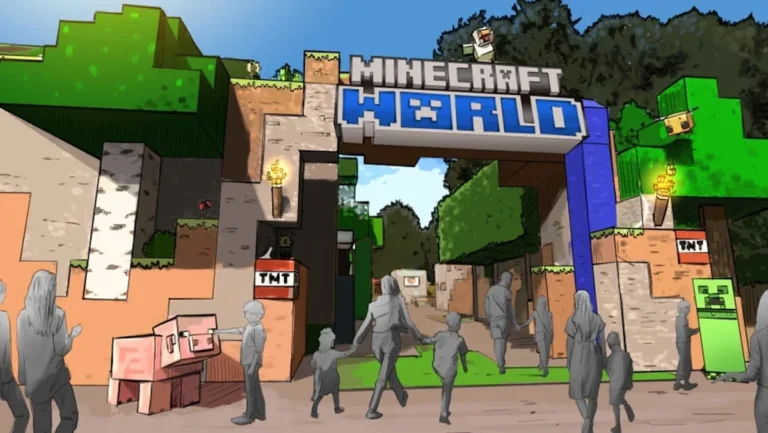
Merlin Entertainments and Mojang Studios are collaborating to create the first-ever Minecraft theme park, named Minecraft World, which will open in 2027 at Chessington World of Adventures. The project has a budget of £50 million and will feature a roller coaster that takes guests on a minecart journey through the Nether. The park will include interactive adventures, themed dining experiences, and block-built playscapes, as well as merchandise stores. The developers are working closely with Minecraft creators to ensure authenticity. Minecraft World is located 35 minutes by train from London Waterloo.
Tech Optimizer
September 28, 2026
Two newly identified Critical CVEs have expanded Microsoft's September identity infrastructure vulnerabilities to over ten verified weaknesses across more than ten distinct services. The Azure Database for PostgreSQL is vulnerable to CVE-2026-85878, an Improper Authorization flaw (CWE-285) with a CVSS score of 9.9. Azure Billing is impacted by CVE-2026-62874, which presents an Insufficient Data Authenticity Verification issue (CWE-345) with a CVSS score of 10.0. Both vulnerabilities were disclosed on September 18 and validated by Tenable and MITRE. CVE-2026-85878 allows an authorized attacker to elevate privileges over the network with minimal complexity, while CVE-2026-62874 requires no authentication, enabling unauthenticated attackers to jeopardize financial integrity. The vulnerability cluster first emerged during the Patch Tuesday cycles on September 3 and September 8, with initial reports highlighting critical flaws in core services. Other September disclosures include CVE-2026-83711 (Azure AD B2C, CVSS 10.0), CVE-2026-70352 (Azure AI Language, CVSS 10.0), CVE-2026-83941 (Entra ID, CVSS 9.9), CVE-2026-62916 (Entra ID, CVSS 9.1), CVE-2026-69857 (Azure Cosmos DB, CVSS 8.5), and CVE-2026-69854 (Spring Cloud Azure, CVSS 9.0). Activity heightened between September 17 and 18 with the introduction of CVE-2026-77903 (Microsoft Dataverse, CVSS 9.0) and CVE-2026-69843 (Microsoft Fabric, CVSS 10.0). The attack surface has broadened from authentication concerns to encompass trust in AI endpoints, data storage locations, and billing verification processes. Seven out of the ten vulnerabilities are unauthenticated, and all issues were addressed through server-side fixes by Microsoft. The extensive range of affected services suggests these vulnerabilities indicate a shared architectural dependency on authentication logic.
Winsage
September 27, 2026
Windows 11 requires drivers to be digitally signed, a policy aimed at enhancing security by preventing unauthorized code from executing at the kernel level. This requirement, which began with Windows Vista and became mandatory with Windows 10, version 1607, has tightened over the years, especially with the introduction of UEFI Secure Boot and TPM in Windows 11. While this enforcement protects against malware and supports anti-cheat systems in gaming, it limits user autonomy and imposes significant challenges for developers, particularly those working on smaller projects. In contrast, Linux allows users more freedom to modify their systems, though this flexibility can compromise security.
Search