autonomous

AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If an organization holds Microsoft 365 E5, it already has access to Microsoft Defender for Endpoint. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly management. CrowdStrike is preferred for those with a mature Security Operations Center (SOC) and sufficient budget. The choice of endpoint protection depends on specific organizational needs. Business endpoint protection integrates various technologies to defend against malware and attacks on devices. Organizations should assess their current situation before selecting a solution. Key recommendations include: - Microsoft Defender for Endpoint for organizations already using Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a funded SOC. - SentinelOne for mid-sized organizations needing automation. - ESET for those with older hardware or virtual desktops. - Avast Business for very small businesses lacking IT staff. - VIPRE for budget-conscious organizations needing straightforward coverage. - Expel for organizations wanting managed detection across diverse environments. Organizations should avoid running multiple real-time agents simultaneously and ensure prevention features are activated. Testing should prioritize line-of-business applications, and rollout procedures should be defined before going live. It’s essential to verify update staging and rollback procedures with vendors and confirm existing licenses to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If you hold Microsoft 365 E5, you have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly platform. CrowdStrike is suggested for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses, VIPRE for budget-conscious mixed estates, and Expel for tool-agnostic managed detection and response. Antivirus and EDR are now unified under a single agent, and organizations should inquire about update staging processes to avoid issues like those experienced in July 2024 with a major vendor's faulty content update. Independent tests from organizations like AV-Comparatives and AV-TEST are crucial for evaluating protection rates and false positives. Linux servers require attention as they are often targeted by ransomware. When deploying endpoint protection, avoid running two real-time agents simultaneously, activate prevention features promptly, and test deployments on critical applications first. Organizations should confirm their Microsoft licensing covers necessary features and ensure there is a plan for responding to alerts. Common pitfalls include neglecting identity management and failing to test response workflows before incidents occur.
Tech Optimizer
September 7, 2026
Endpoint detection and response (EDR) continuously records process, file, registry, and network activity on endpoints, applying behavioral analytics to identify attacker techniques while providing tools for investigation and containment. Several EDR platforms have emerged, each catering to different organizational needs: 1. CrowdStrike: Best overall for its rich telemetry and elite threat intelligence. 2. SentinelOne: Best for autonomous response, featuring strong containment and rollback capabilities. 3. Microsoft Defender for Endpoint: Best value for organizations already using Microsoft 365 E5. 4. Palo Alto Cortex XDR: Best for native data fusion across endpoint, network, and cloud telemetry. 5. Sophos: Best for generalist IT teams due to its user-friendly interface. 6. Trend Micro: Best for server and workload coverage, focusing on cloud and hybrid environments. 7. Bitdefender: Best mid-market value with strong detection capabilities at an accessible price. 8. Trellix: Best for organizations already using Trellix products, offering integrated solutions. 9. Huntress Managed EDR: Best for managed endpoint security, ideal for teams lacking full staffing. 10. Cisco Secure Endpoint: Best for Cisco environments, integrating well with Cisco security solutions. Key differentiators among these platforms include the analyst burden, alert management efficiency, and the impact of retention policies on investigation quality. The evaluation of EDR solutions should consider detection depth, response capabilities, operational costs, and the specific needs of the organization.
AppWizard
September 2, 2026
A developer, Mert Cobanov, optimized his smart TV using Claude Code, resulting in improved performance that surpasses its original state. He connected to his Android TV via ADB, deactivated unnecessary applications, and installed FLauncher without root access. Cobanov has created a website, "Clean up your Android TV," which provides a four-step process for others to achieve similar results. The process allows for reversibility, ensuring nothing is permanently uninstalled, and includes instructions for restoring specific apps if needed.
Tech Optimizer
August 29, 2026
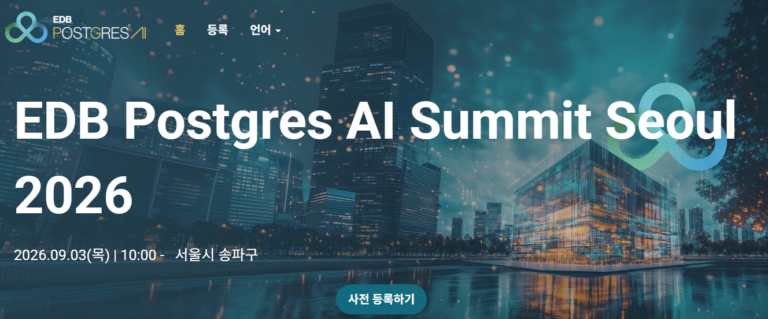
A company's approach to artificial intelligence (AI) begins with determining the optimal structure for data storage and management, often facing challenges such as high costs of commercial databases and reliance on specific enterprise technologies. To effectively utilize AI, companies need to establish new infrastructures, including vector search capabilities, Search Augmentation Generative (RAG) systems, and data lakehouses. EDB is notable for connecting companies and technology partners that have transitioned to open-source databases. On September 3, EDB will host the 'EDB Postgres AI Summit Seoul 2026' at the Sofitel Ambassador Seoul, starting at 10:00 AM. This event is the largest PostgreSQL conference in Korea, themed 'Change the Game,' focusing on the shift from commercial databases to open-source and AI-driven frameworks, featuring real-world case studies. Approximately 300 C-level executives and IT decision-makers from various sectors are expected to attend, with participation by invitation only. The summit will include 15 sessions with customer case studies and technical presentations. Notable discussions will include IBK Industrial Bank of Korea's migration of 15 core systems to PostgreSQL, a semiconductor company's diversification of MPP databases on a DBaaS platform, and Kyobo Book Centre's database modernization strategy. Shopcast will present its development of an 'Agentic Lakehouse' integrating AI technology with a data lakehouse framework. The keynote address will be given by Kim Deok-joong, discussing organizational management strategies for integrating AI agents. The technical sessions will cover the architecture of the 'EDB Postgres AI' platform, which supports AI vector search and RAG, with live demonstrations of the analytics engine ClickHouse and LakeHouse technology for analyzing petabyte-scale data. EDB's domestic distributors and international partners will participate as sponsors. The summit aims to showcase technologies and case studies from the domestic ecosystem, addressing PostgreSQL adoption, system migration, operations, data analysis, and AI implementation. EDB manages transaction, analytics, and AI workloads using Postgres in cloud environments, serving over 1,500 global customers. Herve Timsit, EDB's Chief Revenue Officer, emphasized the event's focus on sharing tangible results and addressing the challenges of commercial databases while investing in AI infrastructure.
Winsage
August 24, 2026
This week, insights into datacenter technology reveal a shift in GPU dominance, with companies exploring alternatives. Cerebras, founded by Andrew Feldman, has developed chips the size of dinner plates that contain 44 gigabytes of ultra-fast SRAM, circumventing high-bandwidth memory supply constraints. In 2024, Cerebras launched an inference server that processes tokens faster than any GPU configuration, utilizing structured sparsity and partnering with AWS and AMD. The latest Cerebras chips, CS-4 systems, feature a modular architecture that doubles performance and bandwidth. Google is also moving towards custom silicon with its Tensor Processing Units (TPUs), while Marvell competes with Broadcom in providing IP for custom chips. Waymo announced a custom machine learning accelerator for its autonomous vehicles to enhance compute density and address limitations of previous FPGA use. On the software side, Microsoft is reintroducing the ability to move the taskbar in Windows 11, responding to user feedback after nearly five years. This change reflects Microsoft's focus on user experience amid competition from alternatives like macOS and Linux.
Search