Microsoft is working to reduce the memory footprint of Windows, aiming for acceptable performance with 8 GB of RAM. However, users face challenges with lengthy update processes, as demonstrated by a recent experience where a laptop took approximately seven hours to boot due to numerous updates. This includes patches for Windows components, firmware, and drivers, leading to multiple restarts and frustrating progress bar behavior. The tech industry is recognizing the need for greater efficiencies, but Microsoft must also address the overwhelming frequency of updates that hinder user experience.
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
Mark Russinovich, the Chief Technology Officer of Microsoft Azure, transitioned ZoomIt, a Windows tool for screen zooming, recording, and annotation, to macOS using artificial intelligence. Originally developed to aid in teaching Windows Internals, ZoomIt has been enhanced over the years with features like screen recording and webcam overlays. Despite initial reluctance due to time constraints, Russinovich utilized AI to create a functional macOS version in just two days, significantly faster than anticipated. The AI model leveraged the original Windows code, allowing for a high-fidelity clone of ZoomIt that includes essential features. ZoomIt for macOS is now available as a free and open-source tool, requiring macOS 14 Sonoma or newer, and can be installed via Homebrew or from Microsoft’s GitHub repository. Users can access its functionalities through keyboard shortcuts and a menu bar icon.
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures.
RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands.
The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
David Plummer, a former Microsoft engineer, was the primary author of Windows XP's Product Activation system, which included the infamous product key FCKGW. This key became widely used on pirated copies of the operating system. Plummer created the activation system by compressing and encrypting disc data, ensuring its security. The FCKGW key was specifically tied to certain data configurations, making it ineffective on standard XP CDs. A piracy group, Devils0wn, leaked a complete Windows XP Pro Corporate ISO and the valid FCKGW key just five weeks before the official launch, allowing unauthorized installations. Microsoft responded by blacklisting product IDs associated with the compromised keys in Service Pack 1 and blocking updates for installations using the FCKGW key in Service Pack 2. Valid, un-leaked Volume License Keys (VLKs) remained functional for years after the incident. Plummer noted that the media and the key were leaked before the product reached stores, preventing the intended hardware-binding from functioning.
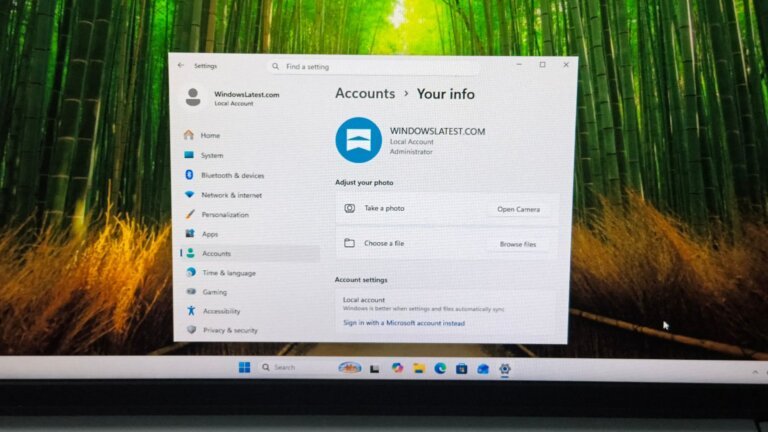
A workaround has been discovered for Windows 11 Home Edition users that allows them to bypass the requirement for a Microsoft account during setup. Users can click the "Learn more" hyperlink during the account prompt in the Out-of-Box Experience (OOBE) to proceed without signing in. This method has been demonstrated by a user named "Bob Pony" and is currently functional, although it may not last long as Microsoft typically addresses such loopholes. The workaround is exclusive to the Home Edition, and users of Windows 11 Pro have different options available.
Artificial intelligence is transforming malware detection by moving away from traditional file signature reliance to analyzing program actions. Antivirus software previously used signatures to identify known threats, but the rapid emergence of over 450,000 new malware samples daily complicates this method. Attackers now employ techniques like repacking and encryption to evade detection, prompting the need for machine-learning and behavioral techniques for better protection. Modern detection systems assess multiple characteristics of executable files, including their behavior, to identify potential threats, even if they lack recognized signatures.
Microsoft's Project Ire exemplifies advanced detection capabilities, functioning as an automated malware analyst that evaluates unknown binaries based on their behavior. Additionally, modern endpoint-security products leverage cloud systems to analyze data from multiple devices, enhancing threat detection through shared intelligence. However, AI detection can still produce false positives and is susceptible to manipulation by attackers. Therefore, effective security systems require a combination of traditional measures, behavioral monitoring, machine learning, and human analysis to navigate complex threats.
Android Auto allows users to enhance their driving experience with applications from the Google Play Store and through sideloading. To enable sideloading, users must access developer settings in Android Auto by navigating to the Apps section, tapping on version and permission info multiple times, and activating the Unknown sources toggle. Users can then install the Android Auto Apps Downloader (AAAD) from its GitHub repository, which helps discover and install third-party applications.
Notable applications include CarStream, which allows access to YouTube content while parked, although it is not compatible with Android 15 or later. Screen2Auto enables users to mirror their entire Android phone screen onto the infotainment display, allowing access to any application, including YouTube. AABrowser provides a full web browsing experience on Android Auto, supporting touchscreen controls and a keyboard for input, but should only be used when safely parked.
Microsoft has addressed 24 Common Vulnerabilities and Exposures (CVEs) in its developer tooling, with 23 classified as important and one as critical. The critical entry, CVE-2026-34182, has a CVSS score of 9.1 and affects CMS AuthEnvelopedData processing in Visual Studio versions 2017 to 2022. The highest-scoring entry is CVE-2026-81376, a security feature bypass in Visual Studio Code, with a CVSS score of 9.6. Visual Studio Code and its Copilot extensions account for ten of the CVEs, primarily related to security feature bypasses. The .NET framework has updates for SDK versions 8.0.131, 8.0.425, 9.0.121, 9.0.318, 10.0.112, and 10.0.401. Monthly rollups for the .NET Framework have been released for various operating systems, including Windows Server 2012 and Windows 10 versions. Adobe has released 963 CVEs, with 55 flagged by Microsoft as high risk, primarily in printing and fonts.
Microsoft has streamlined the Windows 11 setup process by encouraging the creation of a Microsoft account (MSA) during installation. A new workaround allows users to create a local account without needing complex tools or disconnecting from the internet. To use this method, users should start a fresh installation of Windows 11 Home, connect to the internet, and look for the small “Learn more” link under “Sign-in options” when prompted for MSA details. If successful, users can enter a local username and continue the setup process, including creating a password and answering security questions. This method is not officially sanctioned by Microsoft and may be an unintended bug. Microsoft has previously eliminated other methods for bypassing the MSA requirement, citing the need for fully configured devices. Internally, opinions at Microsoft about the MSA requirement vary, with some executives expressing frustration. The overall Out-Of-Box Experience (OOBE) still requires improvement, with reports indicating lengthy setup times due to advertisements and web-based components.