capture

AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
Tech Optimizer
September 16, 2026
Iranian state-affiliated cyber actors are targeting dissidents, activists, and journalists using fake AI applications, counterfeit antivirus tools, and fabricated MRI scan results, primarily through a spyware family known as CHOSEN BRICK, which is designed for Windows systems. This campaign has been active since at least 2025 and affects individuals globally, including in the UK, US, and Netherlands. The malware establishes persistence via the Windows Registry Run key and communicates through Telegram, utilizing unique Bot IDs for each victim. CHOSEN BRICK is capable of extensive data collection, including capturing screenshots, recording audio, and stealing email content. Personal information from victims has been found on pro-Iranian leak sites, increasing harassment risks. Security measures should include monitoring for suspicious Registry entries and unusual communications, while users are advised to avoid unsolicited software installations and keep their systems updated. The FBI refers to this malware family as HEAVYGRAM.
AppWizard
September 16, 2026
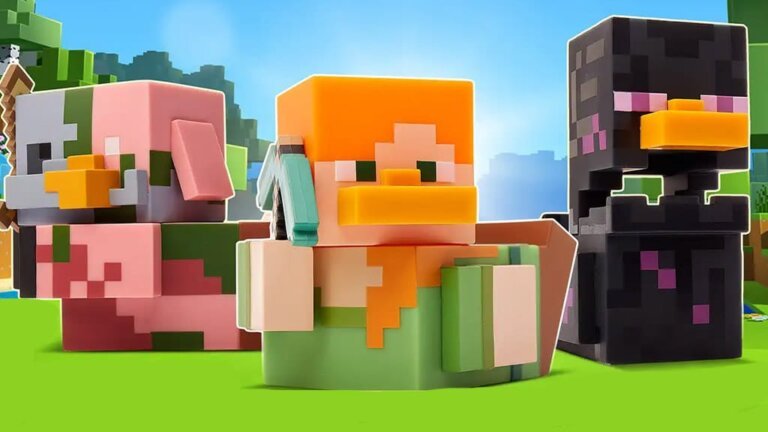
Tubbz is expanding its Minecraft lineup with three new collectible rubber ducks: Alex, an Enderman, and a Zombified Piglin. The Enderman features a slack-jawed expression and purple eyes, the Zombified Piglin has a half-decayed look and a golden sword, and Alex is equipped with a diamond pickaxe. Each comes in a themed bathtub display with a sticker and an exclusive print. They are available for purchase at select retailers and on tubbzus.com, with a suggested retail price of .99 - .99.
AppWizard
September 16, 2026
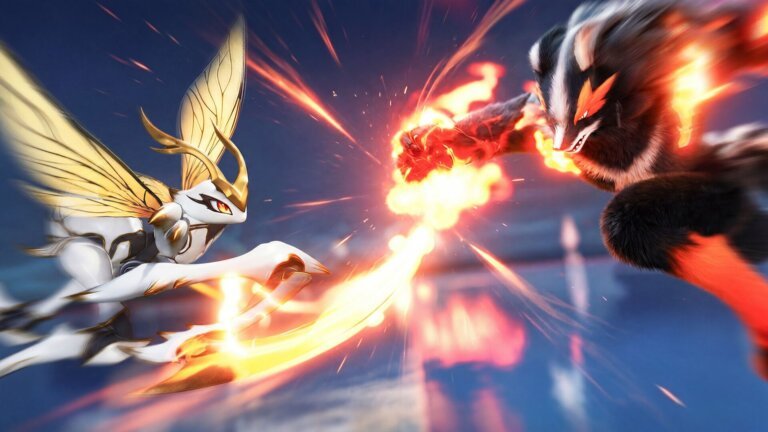
Aniimo is not a gacha game, as it lacks traditional banner systems. It monetizes through a cosmetics shop where players can buy Lumin Crystals with real money for outfits and accessories. Some cosmetics are available for free, but premium items are often behind a paywall. The game also features shop bundles and a battle pass called the "Companion Handbook," which includes free and premium tiers. Players can acquire Aniimo by using Aniipods to capture creatures, hatching eggs, completing events, or progressing through the battle pass. Legendary Aniimo can be captured by collecting unique tokens and using a special Aniipod.
Winsage
September 15, 2026
Iranian state cyber actors are targeting individuals through popular messaging applications, using surveillance and data-stealing malware known as "Chosen Brick," which has been in use since at least 2025. This malware is designed for Windows systems and enables the theft of personal data, allowing Iranian spies to monitor perceived threats such as dissidents, activists, and journalists. The attacks typically begin with messages sent via WhatsApp or Telegram, impersonating trusted contacts. Attackers conduct extensive research on their targets to craft convincing messages that encourage victims to download malicious files disguised as legitimate applications. Once executed, Chosen Brick operates stealthily, evading detection and establishing a connection for command-and-control communications. It can enumerate processes, capture screen and audio content, extract sensitive information, and even wipe infected systems. Organizations suspecting compromise are advised to engage IT providers for investigations and to inform staff about potential risks. Recent alerts follow cyberattacks on water and energy sectors linked to Iran, with ongoing concerns about the implications for cybersecurity amid escalating military tensions. Additionally, five US agencies have reported that attackers are using AI-generated scripts to exploit vulnerabilities in critical infrastructure systems.
AppWizard
September 15, 2026
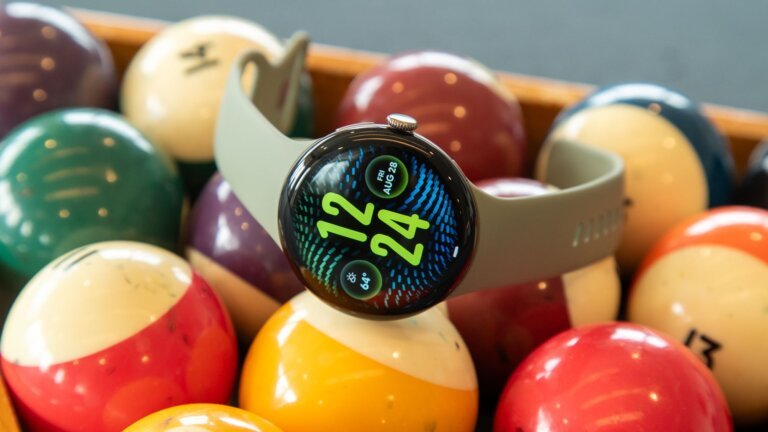
A Google-made wearable device has been listed at the FCC, suggesting it may run on Wear OS and is primarily designed as a fitness tracker due to its lack of Wi-Fi connectivity and use of Bluetooth LE. It features GPS support and a durable metal frame. ADB testing indicates it may include Wear OS software. This device could fill the gap between the Fitbit Air and the Pixel Watch, as there have been no updates to the Fitbit Charge series since 2023. It is also connected to an unannounced fitness tracker shown during the Pixel 11 launch event, indicating Google's intent to expand its fitness tracking offerings.
AppWizard
September 15, 2026
Aniimo is set to release on September 15 in the United States and September 16 in Europe and the UK. Preloading is available starting September 14 at 10 am (UTC+8), and the game requires approximately 40GB of storage, with initial downloads around 28GB. Players can download the Aniimo launcher from the official website. The game adopts a free-to-play model without gacha mechanics.
Winsage
September 15, 2026
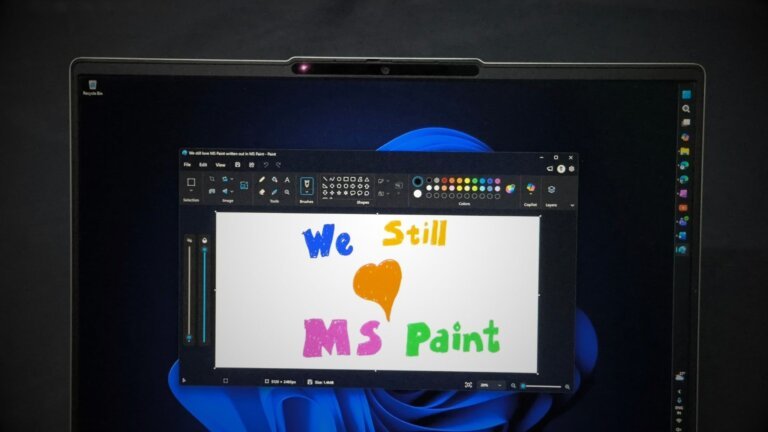
Microsoft's Paint has been a popular tool since its launch in Windows 1.0 in 1985, with over 100 million monthly users reported in 2017. Paint 3D was introduced as part of Microsoft's vision for "3D for everyone," featuring tools like 3D Doodle, Brushes for 3D surfaces, Magic Select, and Mixed Reality Viewer. However, it struggled to resonate with users due to a cumbersome interface and a lack of necessity for 3D capabilities, leading to its deprecation in 2024. By 2021, Paint 3D was no longer preinstalled on new Windows 10 devices, and Microsoft shifted focus back to the original Paint, enhancing it with features like background removal and AI-driven tools. Despite its potential, Paint 3D failed to bridge the gap between casual users and professional 3D software, and an open-source approach could be a way to revitalize it.
AppWizard
September 14, 2026
LG asserts that its smart TVs do not secretly record or transmit user conversations, clarifying that listening for a wake word does not mean recording conversations. Audio without the wake word is discarded locally and not sent to LG servers. The company uses technology that listens for a specific wake word and processes audio only after recognition. LG's Automatic Content Recognition (ACR) technology, which enhances user experience, relies on audio fingerprinting and requires user consent to activate. Users can disable ACR in TV settings. This privacy debate follows a previous incident involving unsolicited promotional pop-ups from LG monitors, which led to intervention from Microsoft.
Search