A study by Proton found tracker code associated with companies in China and Russia in many of the most downloaded free Android games in the US and Europe.
Qualcomm is exploring the possibility of adding DirectX 12 support to future Snapdragon mobile chips, potentially improving PC game compatibility and performance on mobile devices.
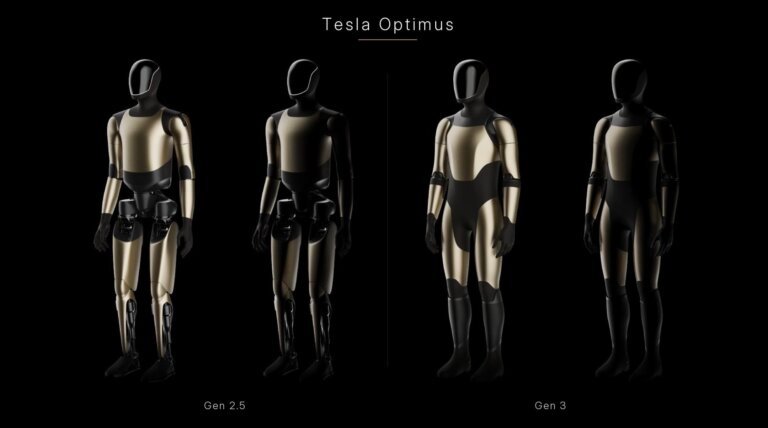
Tesla's next-generation Optimus humanoid robot, referred to as Optimus Gen 3, has been previewed through new 3D design assets found in the Android version of Tesla’s mobile app. These assets, which include renders labeled “gen3” and images comparing Optimus Gen 2.5 and Gen 3, indicate significant design changes. The robot features a cleaner aesthetic with enclosed joints, a unified torso shell, thicker forearms, slimmer wrists, and redesigned legs that resemble integrated boots. The assets began appearing in app builds around August 27, 2026, with higher-resolution versions on September 5. Tesla initially planned to unveil Optimus Gen 3 by the end of Q1 2026, but this timeline was missed. Elon Musk later indicated that the reveal was postponed to mid-year for strategic reasons. Tesla has also started auditing suppliers in China for Gen 3 production, suggesting a potential reveal is approaching.
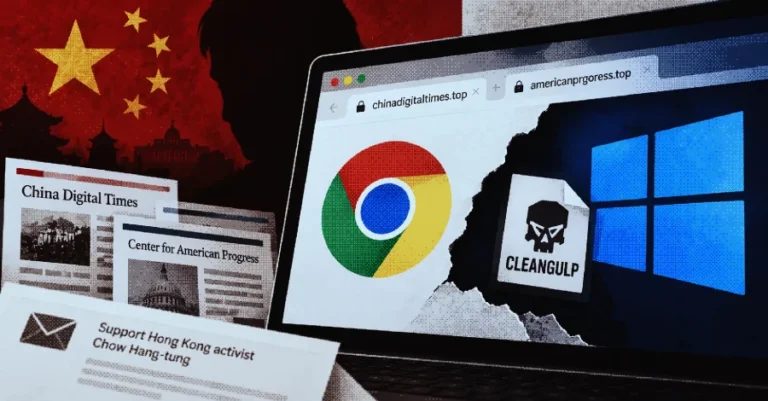
A Chinese threat actor, codenamed UTA0565, has exploited newly disclosed vulnerabilities in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) through deceptive websites, achieving remote code execution. The attacks were detected on September 3 and 4, 2026, and involved impersonating organizations to mislead victims, particularly targeting Asian government entities with phishing emails related to Hong Kong activist Chow Hang-tung. The phishing messages directed users to fraudulent sites that loaded an HTML element using the BlueMoon exploit kit, which delivered a payload named "chrome_cleanup.exe," associated with the CLEANGULP malware family. This malware allows for command execution, process listing, file uploads and downloads, and uses a hard-coded domain for command-and-control communications. The exploit's widespread use suggests a coordinated effort within the Chinese cyber espionage community, with indications that multiple groups are sharing and weaponizing the exploit.
A newly identified strain of Android malware, RatHat, utilizes generative AI to manipulate infected devices in real time. It is linked to threat actors believed to be operating out of China. RatHat serializes the device’s live Accessibility tree into XML format and communicates with a generative AI assistant to return screen coordinates, identify text, and issue navigation commands. The malware employs WebView-based HTML overlays to capture login credentials from banking and cryptocurrency applications and can infiltrate payment apps like WeChat and Alipay to extract PINs. It also features an SMS receiver and notification listener to intercept OTPs and 2FA codes.
RatHat is disseminated through smishing, malvertising campaigns, and misleading third-party forums. It employs anti-analysis techniques such as container tampering, manifest bombing, DEX bytecode poisoning, string encryption, and anti-debugging. Once installed, it gains Accessibility access, activates Developer Options, and enables Wireless Debugging, allowing it to connect to the device's local ADB service and launch control agents with shell-level privileges.
The malware captures raw touch coordinates to reconstruct PINs and unlock patterns, bypassing screenshot protections. It also includes persistence mechanisms that prevent uninstallation by presenting a fake Google Play failure overlay and automatically reinstalling itself if removed.
Cybersecurity researchers at Zimperium have identified a new strain of malware called RatHat, targeting Android devices and linked to threat actors from China. RatHat uses generative AI to maintain persistence and control over infected devices. The malware is typically spread through social engineering, tricking users into downloading counterfeit applications that appear legitimate. Once installed, RatHat requests accessibility permissions, activates Wireless Debugging, and can capture text messages, create overlays, and steal passwords and multi-factor authentication codes. Its AI capabilities allow it to navigate the device interface in real-time, making detection by security software more difficult. To protect against RatHat, users should avoid downloading apps from untrustworthy sources, and removal requires a factory reset of the device.
A new messaging and payment app called Max has emerged in Russia, developed by VKontakte, and has become the country's most utilized messaging platform. Max integrates various services, including banking and government services, and has been adopted by tens of millions of Russians. It features extensive surveillance capabilities, allowing it to take screenshots, access information without consent, impersonate users, and potentially conduct cyberattacks. The app's adoption has been largely mandatory, particularly among state employees and students. Despite its rise, Max has not replaced Telegram as a primary news source, and users have raised concerns about privacy and surveillance. Experts warn that Russia's swift implementation of digital control strategies reflects a growing trend of digital authoritarianism.
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox.
The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception.
Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client.
The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures.
RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands.
The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
Chinese state security officials have emphasized the necessity for organizations to keep antivirus software and virus databases updated to prevent data breaches and unauthorized access. The Ministry of State Security (MSS) highlighted that neglecting these updates has led to significant security incidents, including the theft of sensitive data and cyberattacks on work email accounts. Specific cases include a research institute that suffered a breach due to unpatched vulnerabilities, an institution exposed to cyberattacks for not enforcing regular virus scans, and a company that operated a poorly protected server with outdated antivirus software. Contributing factors to delayed updates include a lack of awareness about cybersecurity risks, insufficient network maintenance, and unclear responsibilities within organizations. Under China's Cybersecurity Law, network operators must implement measures to protect against cybersecurity threats. The MSS advises organizations to enhance their cybersecurity measures by adopting technologies like automated risk alerts and intelligent behavioral analysis.