China

AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
AppWizard
September 14, 2026
The iQOO 16 will be the first smartphone to feature a 2K resolution OLED display with a 165Hz refresh rate, co-developed with Samsung Display. It utilizes Samsung's M16 luminescent material and LEAD 2.0 architecture, achieving a global peak brightness of 2,800 nits and a local peak brightness of 10,000 nits, with a pixel density of 508 PPI. The device includes a 500Hz multi-touch sampling rate and a 5,000Hz instantaneous sampling rate for gaming, along with Q-Flex technology to reduce input lag. It also features 3,300Hz PWM dimming and is designed to be energy-efficient, consuming 31% less power at 150 nits compared to a 1.5K panel. The iQOO 16 is expected to launch in China at the end of September.
Winsage
September 9, 2026
Recent investigations have identified the BlueMoon exploit kit, used by espionage-driven threat activity clusters, particularly linked to APT31, a China-aligned state-sponsored group, since August 28, 2026. BlueMoon exploits three vulnerabilities: CVE-2026-85046 (a type confusion vulnerability in Google Chrome's V8 engine), an unassigned V8 sandbox escape, and CVE-2026-85880 (a heap-based buffer overflow in Windows ALPC). Google and Microsoft have released patches for these vulnerabilities, which were exploited as "patch-gap" zero-days. The attack vectors typically begin with phishing emails that lead victims to malicious URLs, triggering the vulnerabilities for code execution and privilege escalation. Variants of BlueMoon have been detected, featuring modifications for specific campaigns. Notable attack chains include: - APT31 targeting NGOs and mining firms in the U.S. with a malicious browser add-on called GemStone. - UNK_LateNight targeting U.S. aerospace companies, deploying BlueMoon alongside the ShadowPad backdoor. - UNK_DoubleCheck targeting a Vietnamese manufacturer, using DLL sideloading to execute a Rust binary. - UNK_QuietRacket targeting government and financial organizations in Indonesia and Singapore, modifying BlueMoon to execute a .NET assembly. CISA added the Chrome flaw to its Known Exploited Vulnerabilities catalog on September 4, 2026, requiring federal agencies to apply patches by September 18, 2026. Indicators of compromise include specific process trees, files, folders, scheduled tasks, mutexes, and registry keys. Proofpoint has released detection rules to help organizations identify and mitigate these threats.
BetaBeacon
September 8, 2026
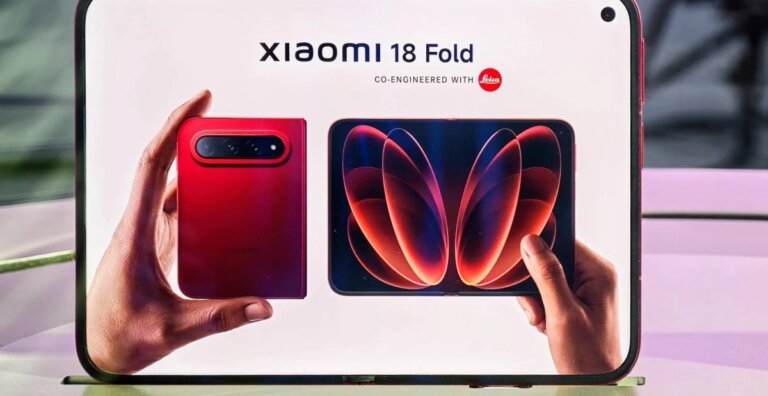
Arm's DLSS for Android is set to be released soon, starting with the Xiaomi 18 Fold in China. The new Arm Mali G2-Ultra NX graphics processor inside the custom Xring O3 chip promises to enhance mobile gaming by providing PC-like technologies to improve game performance without using more power. This technology includes AI gaming graphics accelerators that can eliminate jagged edges in games and offer features similar to Nvidia's DLSS, such as AI upscaling, frame generation, and ray reconstruction. The new graphics tech is expected to be available in various devices beyond Chinese phones, including tablets and Chromebooks. The technology is aimed at improving gaming experiences while maintaining battery life and will be integrated into games like Where Winds Meet, Infinity Nikki, and Arena Breakout: Infinite.
AppWizard
September 5, 2026
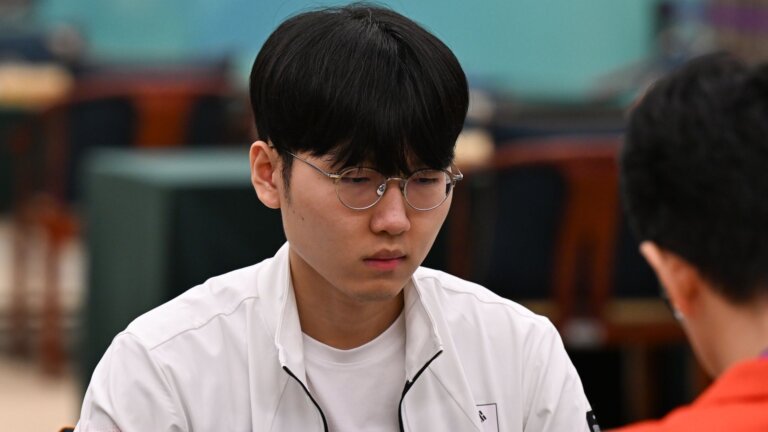
Go grandmaster Shin Jin-seo became the first human to win against the AI platform KataGo on July 21, achieving victory in an official three-game series with a final score of 2-1. Shin, who is 26 years old, played with a two-stone handicap and initially lost the first match before winning the next two. His victory is significant as it contrasts with the previous defeat of grandmaster Lee Sedol by Google's AlphaGo a decade ago. Shin expressed the desire to challenge AI under more difficult conditions in the future and emphasized the importance of personal strategy over imitating AI moves.
Tech Optimizer
September 5, 2026
The cyber threat group Silver Fox is distributing the ValleyRAT backdoor disguised as a legitimate signed Chinese adware application, specifically bundled with the QN Wallpaper tool. This malware allows attackers to gain comprehensive control over infected machines, enabling them to collect sensitive information, capture screenshots, and deploy additional malicious modules. The attack utilizes DLL sideloading, where a modified version of QN Wallpaper loads a malicious DLL from the same directory, circumventing signature-based security measures. The installer disables Windows Defender, adds itself to autorun entries, and uses the "runas" command to elevate privileges if the user lacks administrator rights. ValleyRAT also marks its process as critical, potentially causing a blue screen of death if terminated. Kaspersky has identified Silver Fox as the likely perpetrator of this campaign, known for similar techniques.
AppWizard
September 4, 2026
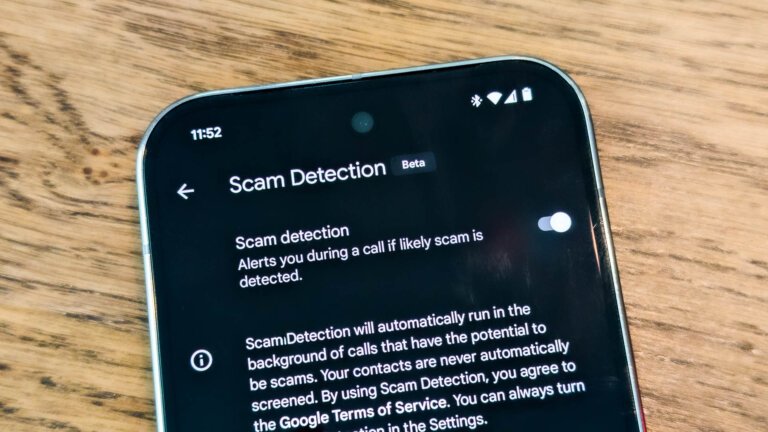
Google's Scam Detection feature, initially available only on Pixel devices, is expanding to more Android smartphones, currently accessible on the Galaxy S26 series and potentially coming to vivo phones. Recent findings from the Google Phone app's public beta indicate that Xiaomi may also support this feature, with the Xiaomi 18 Fold being a possible candidate for the initial rollout, although it is currently confirmed only for release in China. Google's Scam Detection uses on-device AI to analyze incoming calls for potential scams, aiming to enhance user security. The feature is still in beta and may have flaws, but improvements are expected as Google refines the technology.
Search