code execution

Tech Optimizer
October 11, 2026
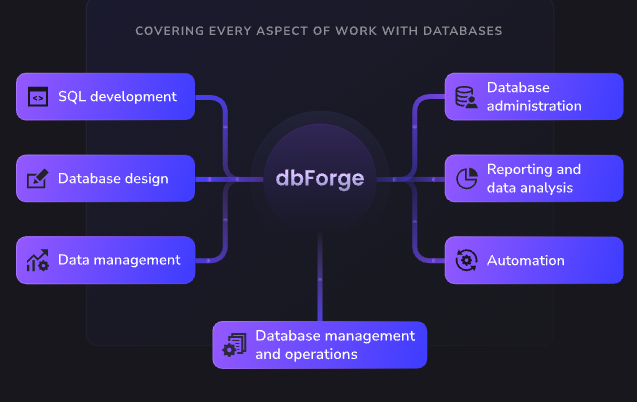
Devart has released dbForge 2026.2, a unified database management ecosystem for PostgreSQL developers, featuring an embedded PostgreSQL Debugger that allows for efficient error tracking in server-side code. The Debugger enables breakpoints, step-through code execution, and real-time monitoring of variables and query results. Visual editors for PostgreSQL event triggers, functions, and procedures have been introduced, allowing for easier management without manual SQL writing. The dbForge AI Assistant now offers expanded context awareness, enabling users to attach various documents and select from multiple AI models for generating relevant SQL code. A free Express edition of the AI Assistant is available, with limited features compared to paid plans. Additionally, new SQL refactoring commands and schema comparison improvements have been implemented, along with updates for compatibility with MySQL 26.7 and MariaDB 13.x.
Tech Optimizer
October 6, 2026
Devart has released dbForge 2026.2, a database management suite update featuring a PostgreSQL Debugger for error tracking, visual editors for managing PostgreSQL objects, and an enhanced dbForge AI Assistant with broader context awareness. The AI Assistant now supports models from Anthropic and OpenAI and includes a free Express edition with limited features. The update also improves SQL development and schema comparison functionalities, with new refactoring commands and support for MySQL 26.7 and MariaDB 13.x. dbForge 2026.2 is available for download, with current users able to update through the Help menu.
Winsage
September 24, 2026
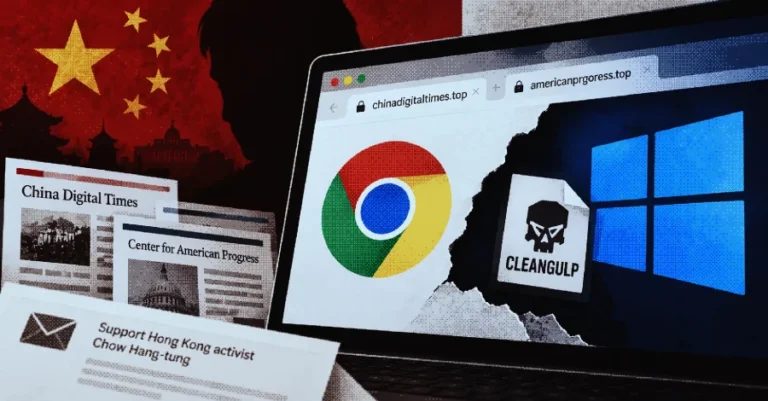
A Chinese threat actor, codenamed UTA0565, has exploited newly disclosed vulnerabilities in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) through deceptive websites, achieving remote code execution. The attacks were detected on September 3 and 4, 2026, and involved impersonating organizations to mislead victims, particularly targeting Asian government entities with phishing emails related to Hong Kong activist Chow Hang-tung. The phishing messages directed users to fraudulent sites that loaded an HTML element using the BlueMoon exploit kit, which delivered a payload named "chrome_cleanup.exe," associated with the CLEANGULP malware family. This malware allows for command execution, process listing, file uploads and downloads, and uses a hard-coded domain for command-and-control communications. The exploit's widespread use suggests a coordinated effort within the Chinese cyber espionage community, with indications that multiple groups are sharing and weaponizing the exploit.
Tech Optimizer
September 23, 2026
A new tool named BigDiskBuster has been released on GitHub, which disrupts Microsoft Defender Antivirus by preventing it from installing updates. It does this by consuming available disk space during the update process, causing Defender to remain on its current version and unable to receive new platform or signature updates. BigDiskBuster operates as a local denial-of-service technique and requires prior access to the target machine to execute. The tool was created by researcher Abdelhamid Naceri, known as Nightmare Eclipse, who has previously worked on similar projects. As of now, there is no CVE identifier, patch, or advisory from Microsoft regarding this issue.
Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
Winsage
September 14, 2026
Microsoft's recent security updates have caused disruptions in several areas: 1. Remote Desktop Services (RDS): Users on Windows 11 26H1 and Windows Server 2012 are experiencing connectivity issues, including failed connections, freezing servers, and unresponsive tools like Microsoft Management Console (MMC). A temporary solution involves restarting the virtual machine, and Microsoft is working on a fix. 2. USB Audio Devices: Problems have been reported with USB Audio Class 1.0 devices on Windows 11 26H1, 25H2, and 24H2, leading to audio issues. A workaround includes switching to two-channel mode, and Microsoft is addressing the situation. 3. Excel Functionality: A fix for vulnerabilities in Excel has disrupted the paste operation across versions 2016, 2019, 2021, and 2024, leaving users unable to paste content correctly. Some users have resolved the issue by uninstalling and reinstalling Office or using commands to remove the security update, though this also removes the associated security fixes.
AppWizard
September 12, 2026
Enthusiasts in the emulation community have acquired a toolkit for the static recompilation of Nintendo Switch games on PCs, following the final update of the suyu emulator, which introduced Recompiler mode. This tool pre-compiles static code from the ARM AArch64 architecture into instructions for modern 64-bit x86 chips, allowing game logic to operate natively and reducing CPU overhead. The implementation is about 50% complete, focusing on code execution, while the graphics and audio components still rely on high-level emulation. Fully functional native ports will require third-party developers to create their own renderers for the Tegra GPU's graphics calls. The codebase allows the community to explore game structures, develop modifications, and create semi-native executables for PCs.
Winsage
September 10, 2026
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has expanded its Known Exploited Vulnerabilities (KEV) catalog, adding critical vulnerabilities that need immediate attention. 1. CVE-2026-75650: A vulnerability in Adobe Commerce and Magento with a CVSS score of 10.0, allowing unauthenticated remote code execution. Affected versions include Magento Open Source releases 2.4.7, 2.4.8, and 2.4.9. It has been actively exploited since September 4. 2. CVE-2026-81963: A Microsoft Windows vulnerability with a CVSS score of 7.8, related to a link-following issue within the Update Stack, allowing local attackers to escalate privileges. It is currently being exploited. 3. CVE-2026-85880: Another Microsoft Windows vulnerability rated at 7.8, involving a heap-based buffer overflow in the ALPC component, permitting local privilege escalation. This flaw is also actively exploited. 4. CVE-2026-86218: A N-able N-central vulnerability with a CVSS score of 10.0, allowing pre-authenticated remote code execution. N-able has released an emergency hotfix for this issue. Federal agencies must address these vulnerabilities by specified deadlines: Windows flaws by September 22 and other vulnerabilities by September 11, 2026, in accordance with Binding Operational Directive (BOD) 22-01. Private organizations are advised to review the KEV catalog and take necessary actions to strengthen their infrastructure against these vulnerabilities.
Search