contacts

Tech Optimizer
September 15, 2026
Iranian state-sponsored hackers are targeting dissidents, activists, and journalists using deceptive tactics, including malicious applications that impersonate reputable cybersecurity products like Norton Antivirus and KeePass. The FBI and UK authorities issued a warning about these hackers, who establish rapport with targets via social messaging platforms, posing as IT support or known contacts. They convince victims to download files that appear authentic, including AI video creation applications and other software. The spyware, named “Chosen Brick,” infects Windows PCs and has capabilities such as capturing screen content, recording audio, collecting message data, and downloading additional malware. The hackers have exploited this spyware to publish personal details of victims, increasing their harassment. The FBI advises potential victims on detecting the spyware and recommends enabling antivirus software, running regular scans, and avoiding unofficial downloads.
AppWizard
September 15, 2026
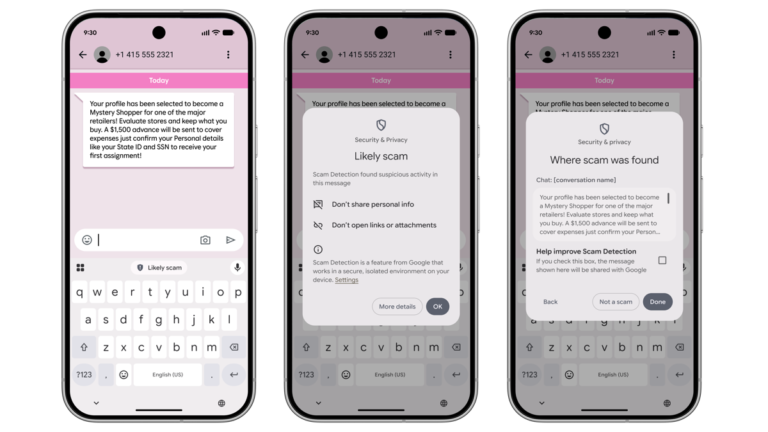
Google has released a feature update for Pixel phones that enhances existing functionalities and introduces new elements. The update expands scam-text detection capabilities to chat applications using Gboard, compatible with devices as old as the Pixel 6, and is available in multiple countries including the US, UK, Australia, Canada, France, Germany, India, Mexico, Japan, and Singapore. It also improves VIP notifications by allowing users to add home-screen widgets for designated contacts and includes a new navigation menu for easier contact switching, available for Pixel 6 and newer models. Additionally, a Harry Potter-themed pack with wallpapers, icons, and audio effects is offered, along with a two-month free subscription to Audible. For Pixel Watch users, the update introduces a one-handed pinch gesture for easier access to notifications and improved functionality for the raise-to-talk gesture on newer models.
Winsage
September 15, 2026
Iranian state cyber actors are targeting individuals through popular messaging applications, using surveillance and data-stealing malware known as "Chosen Brick," which has been in use since at least 2025. This malware is designed for Windows systems and enables the theft of personal data, allowing Iranian spies to monitor perceived threats such as dissidents, activists, and journalists. The attacks typically begin with messages sent via WhatsApp or Telegram, impersonating trusted contacts. Attackers conduct extensive research on their targets to craft convincing messages that encourage victims to download malicious files disguised as legitimate applications. Once executed, Chosen Brick operates stealthily, evading detection and establishing a connection for command-and-control communications. It can enumerate processes, capture screen and audio content, extract sensitive information, and even wipe infected systems. Organizations suspecting compromise are advised to engage IT providers for investigations and to inform staff about potential risks. Recent alerts follow cyberattacks on water and energy sectors linked to Iran, with ongoing concerns about the implications for cybersecurity amid escalating military tensions. Additionally, five US agencies have reported that attackers are using AI-generated scripts to exploit vulnerabilities in critical infrastructure systems.
Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
AppWizard
September 14, 2026
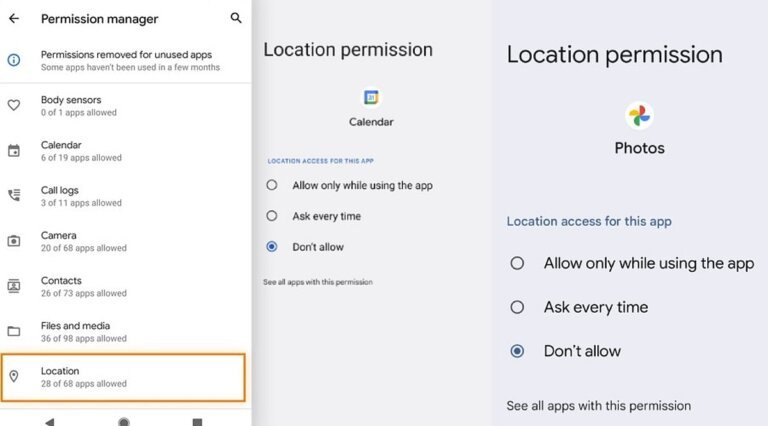
Permissions in Android apps should be granted based on their relevance to the app's primary function. Users should be cautious with permissions such as location, contacts, SMS, microphone, camera, and accessibility access, as they can expose sensitive information or control device capabilities. To review app permissions, users can navigate to Settings, select Apps, choose the application, and tap on Permissions. The Permission Manager under Security & Privacy allows users to see which apps have access to specific permissions. Android can automatically pause activity for seldom-used apps, removing previously granted permissions. If an app repeatedly requests denied permissions, users should evaluate the necessity of the request and consider maintaining their denial if it seems unwarranted.
AppWizard
September 10, 2026
Comma Compliance released the source code for its Android capture component on September 10, 2026, allowing corporate IT and security teams to inspect the software that captures employee text messages for compliance archiving. The source code is available on GitHub under the MIT license. The capture mechanism reads messages stored in the phone's default messaging app, encrypts them, and sends them to the customer's Comma backend without intercepting messages in transit. A persistent notification appears on the phone when archiving is active, indicating the organization responsible for the archiving. Comma previously open-sourced its WhatsApp and Signal capture connectors in 2025.
Search