counterfeit

AppWizard
October 9, 2026
Bitdefender researchers have identified a malware campaign called Midnight Mimosa that can be embedded in the software of low-cost Android devices before sale. This malware operates stealthily, allowing it to install and remove applications without user knowledge, generate fraudulent advertising activity, and convert devices into residential-proxy relay nodes for a botnet. It has been found on MediaTek-based, white-label devices marketed under misleading names. Users should be cautious of suspiciously cheap devices and look for signs of infection, such as unexplained ads, unfamiliar apps, sudden battery drain, and discrepancies in model names. Standard uninstallation or factory resets may not remove this malware, and users are advised to update their devices, review app lists, and contact sellers for refunds or replacements if they suspect infection. Mobile protection solutions can help monitor app behavior and alert users to potential threats.
AppWizard
October 9, 2026
Researchers from Bitdefender have discovered that thousands of inexpensive Android devices are preloaded with malware called "Midnight Mimosa," which generates fraudulent advertising revenue. This malware is embedded in the device firmware before the first power-up, making it impossible for users to uninstall. It operates with system-level privileges, allowing it to install or remove applications without user consent and to download additional code. The malware primarily aims for financial gain through advertising and click fraud, while also gathering information about devices. Bitdefender has detected this malware on thousands of devices across over 150 countries, with the highest concentrations in Mexico, France, and Italy, followed by the United States, Germany, Brazil, and Spain. Many affected devices are low-cost, white-label, or counterfeit models, often sold online. The malware stealthily installs legitimate-looking applications that display ads in invisible windows, generating ad impressions without user awareness. Bitdefender identified at least 32 disguised applications and found 13 apps in the Google Play Store with similar ad-fraud code. The source of the malware remains unidentified, but some affected firmware was signed with certificates from Shenzhen Zediel, a Chinese company. The researchers suggest that the malware could have been introduced at various stages of the supply chain, potentially by manufacturers or intermediaries.
Winsage
October 5, 2026
Microsoft has warned Windows users about a cyber threat that disguises itself as a CAPTCHA test, where cybercriminals use fraudulent verification pages to trick users into executing commands that can install malware. This tactic involves users being directed to a compromised website that presents a fake verification window, prompting them to copy text and execute it in the Windows Run dialog. This method allows attackers to bypass antivirus software by pre-loading malicious scripts disguised as harmless images in the browser's cache. Once activated, the malware collects system information, steals data, and maintains long-term control over the system. Microsoft recommends using robust security software and being aware that no legitimate service will ask users to copy and paste commands into system dialogs.
Tech Optimizer
September 25, 2026
Cybercriminals have developed an infostealer called MacSync, targeting Mac devices by using iCloud calendar events and cloud storage. This malware disguises itself as fake cryptocurrency wallets and pirated software. It begins with a loader that retrieves instructions from calendar entries and deploys malware to exfiltrate sensitive information, including credentials and cryptocurrency wallets. Recent versions have introduced an Objective-C backdoor that mimics Finder. Victims are often tricked into downloading these malicious applications, and effective antivirus solutions can prevent damage. Cybercriminals use tactics like SEO poisoning and phishing to direct victims to fraudulent websites or social media promoting pirated software. In one case, the loader was marketed as a cryptocurrency wallet, and victims encountered a misleading ClickFix error message that prompted them to execute a command in the Terminal.
Tech Optimizer
September 22, 2026
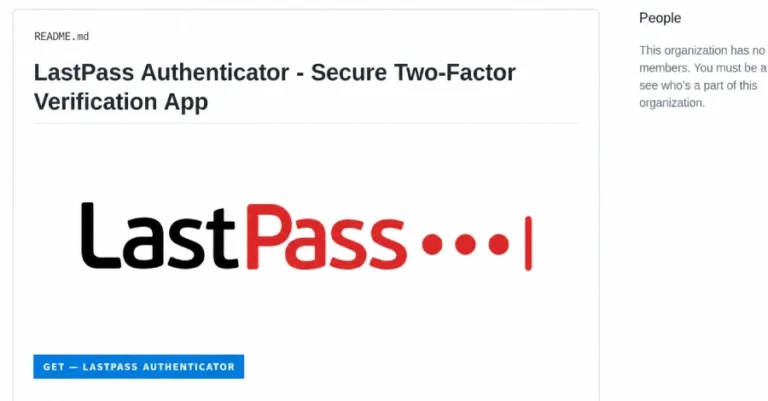
LastPass has identified a sophisticated scheme targeting users of its Authenticator app, involving SEO poisoning and deceptive GitHub pages that distribute malicious ZIP files disguised as legitimate software. Users searching for "LastPass Authenticator download" may encounter these counterfeit pages, which redirect them to a malicious server delivering a ZIP file containing vsdbg.exe and vsdbg.dll. The executable is a legitimate Microsoft debugging tool exploited to execute the malicious DLL through DLL sideloading, allowing the malware to run undetected. Named Rapuncel by security researchers from Delphos, this malware is undetectable by antivirus engines and targets a hardcoded list of 145 antivirus and endpoint security products, disabling them upon detection. Rapuncel harvests sensitive information, including saved passwords from over 25 web browsers, cryptocurrency wallet files from more than 30 applications, and session tokens from platforms like Discord and Steam. It also captures screenshots and compiles a profile of the infected system, uploading the stolen data to an attacker-controlled server. The malware includes a kernel driver that intercepts web traffic, allowing for advertisement injection and search result manipulation. This campaign has been active for several months, with LastPass vaults remaining unaffected. Users are advised to download applications only from trusted sources. Rapuncel establishes persistence on infected machines by installing itself as a Windows service that starts with the system and terminates activated security products. Removing the kernel driver requires booting into Safe Mode or using external recovery tools, as standard Windows utilities cannot eliminate software operating at that level.
AppWizard
September 22, 2026
Cybersecurity researchers at Zimperium have identified a new strain of malware called RatHat, targeting Android devices and linked to threat actors from China. RatHat uses generative AI to maintain persistence and control over infected devices. The malware is typically spread through social engineering, tricking users into downloading counterfeit applications that appear legitimate. Once installed, RatHat requests accessibility permissions, activates Wireless Debugging, and can capture text messages, create overlays, and steal passwords and multi-factor authentication codes. Its AI capabilities allow it to navigate the device interface in real-time, making detection by security software more difficult. To protect against RatHat, users should avoid downloading apps from untrustworthy sources, and removal requires a factory reset of the device.
Tech Optimizer
September 21, 2026
The landscape of computer security has changed significantly over the past two decades. In 2026, antivirus protection remains important, but the need for separate third-party programs has decreased for many users due to the built-in Microsoft Defender in Windows 11, which is activated by default and effectively blocks 100% of common malware samples according to independent testing by AV-TEST. Windows 11 also includes additional protective features like SmartScreen and a robust Firewall. While dedicated security suites from companies like Norton and Bitdefender offer advanced functionalities, many users may find adequate protection with the built-in tools. Research from AV-Comparatives indicates that performance varies among security programs, particularly against real-world attacks. Phishing attacks accounted for approximately 60% of initial access points in incidents examined by the ENISA Threat Landscape report from 2025, highlighting that user behavior is a significant vulnerability. Modern web browsers and operating systems have enhanced their security measures, with Google Chrome, Microsoft Edge, macOS, and Android incorporating features to protect users from harmful websites and downloads. For the average Windows 11 user who keeps their system updated and practices safe browsing, built-in protection is generally sufficient, though paid antivirus options can provide additional tools.
Search