Tech Optimizer
September 21, 2026
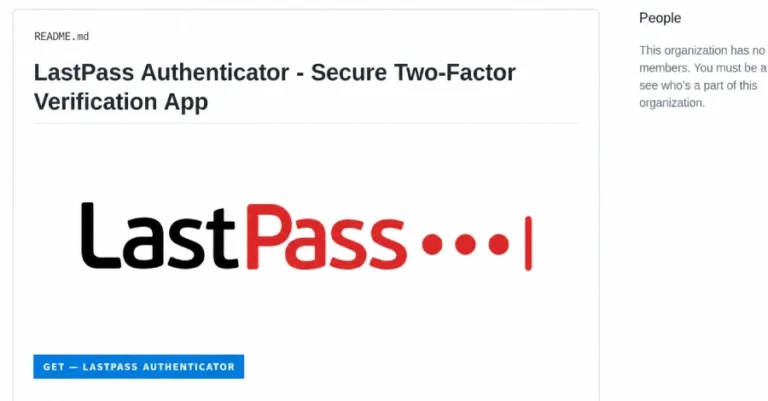
On September 17, researchers from LastPass and Delphos Labs discovered a counterfeit LastPass Authenticator installer on GitHub that installs a malicious Windows kernel driver designed to disable antivirus and steal passwords. The driver, named Alinubx.sys, was signed through Microsoft's hardware compatibility program and initially scored zero detections on VirusTotal. The fake installer is hosted on a fraudulent GitHub page that mimics a legitimate LastPass product page. When executed, the installer uses DLL side-loading to gain SYSTEM-level access and terminates security processes, allowing it to harvest saved passwords from various browsers and applications. The driver is a renamed variant of a known malicious driver, evading detection due to its new file hash. Delphos reported the driver to Microsoft, but it was not considered a security vulnerability. Users who executed the fake installer should treat their passwords and sensitive data as compromised and change them from a secure device. The malicious server has been linked to impersonation pages for multiple brands, and the loader was likely created using a specific crypter tool.