device security

AppWizard
September 18, 2026
Google has launched the AndroidX Security State and Security State Provider libraries, enhancing Android's security framework. These tools allow applications to assess the security status of individual components on a device, rather than relying solely on the overall security patch level. Applications can now verify specific security fixes, identify available updates, and check for pending installations. This is particularly useful for security-sensitive applications, such as banking software, which can confirm the presence of necessary security fixes before allowing transactions. The libraries also enable apps to check for the resolution of specific vulnerabilities (CVEs), ensuring critical fixes are in place before enabling features like tap-to-pay. Phone manufacturers can communicate specific security fixes without changing the overall security patch date, meaning a device may show an outdated patch date while still having resolved certain vulnerabilities.
AppWizard
September 18, 2026
The new AndroidX Security State libraries, with stable releases of Security State v1.1.0 and Security State Provider v1.0.0, allow developers to evaluate the security status of individual device components. They provide three levels of security patch information: Device Security Patch Level (DSPL), Published Security Patch Level (PSPL), and Available Security Patch Level (ASPL). These libraries enable checks on critical components of the Android operating system, including system modules and the Linux kernel, which are represented by version numbers rather than monthly patch dates. Applications that prioritize security can utilize this detailed patch information to assess vulnerabilities, particularly those tracked as Common Vulnerabilities and Exposures (CVEs). The libraries also integrate with the Open Source Vulnerabilities (OSV) database for access to Android Security Bulletin data and device-specific vulnerability reports. Additionally, Android 17 allows manufacturers to declare individual security fixes beyond the stated security patch level, and Google is working with manufacturers to transition their OTA update clients to this new standardized system.
AppWizard
September 16, 2026
A new feature called "expert mode" is being introduced to enhance the "Advanced Protection" framework for Android users, allowing them to toggle specific security features individually. Users will be able to manage six distinct items within the Advanced Protection suite: Intrusion logging, USB protection, Block auto-connection to unsecured Wi-Fi, Unknown apps, Spam filter, and Suspicious links in Google Messages. The "expert features" will not replace "Advanced Protection" but will provide users with the option to enable all protections at once or selectively activate specific features. While "Block auto-connection to unsecured Wi-Fi" will debut with "expert features," the inclusion of "Unknown apps," "Spam filter," and "Suspicious links in Google Messages" in the final version remains uncertain. The relevant resource for updates is the "Google Play services" app, version v26.36, released on September 15, 2026.
AppWizard
September 14, 2026
Android users can now transfer passwords and passkeys between supported password-manager applications without using export files. The transfer process starts in the receiving app, where Android identifies other installed password managers, allowing users to select and authorize specific data for transfer. This new functionality supports both passkeys and conventional passwords, taking only a few seconds to complete. Prominent password managers like Google Password Manager, 1Password, Bitwarden, and Dashlane support this feature, which is available on devices running Android 8 or later. The transfer mechanism maintains the security model of passkeys during authentication while facilitating the exchange between trusted managers. Recent research has identified potential vulnerabilities in synced Google passkeys, emphasizing the need for strong device security measures.
Winsage
September 10, 2026
Microsoft is continuing the rollout of Secure Boot certificate updates, with the next significant deadline on October 19, 2026, when the Microsoft Windows Production PCA 2011 certificate expires. The September 2026 Patch Tuesday update has expanded eligibility for Secure Boot certificates to more PCs classified as “high confidence.” Users may need to reboot their PCs to install these updates, and some may require firmware updates beforehand. Microsoft has confirmed that the update process will persist beyond established deadlines, and older certificates are expiring in stages, with the first two deadlines having already passed. Users should ensure they have the latest updates installed and check their Secure Boot status in Windows Security. Microsoft has assured that PCs without the newer certificates will continue to boot normally and receive standard updates while the rollout continues.
Tech Optimizer
September 7, 2026
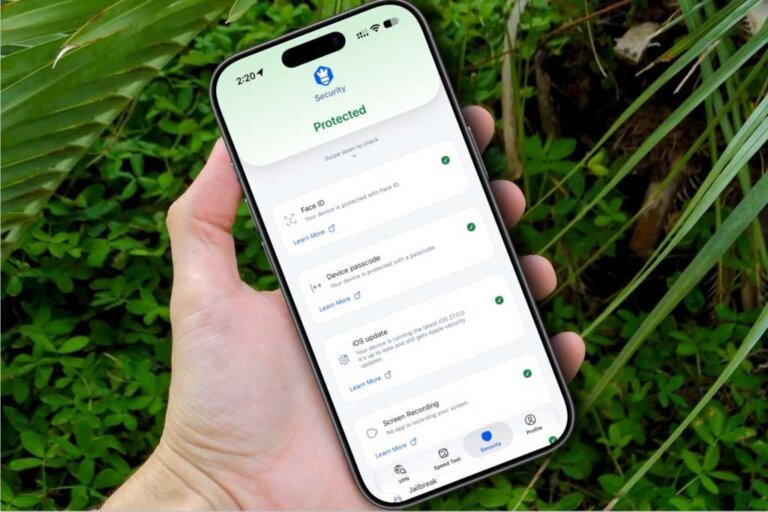
Intego ONE Complete has launched the Intego ONE: VPN & Wi-Fi Security app for iPhone, available at no extra charge to Complete subscribers. The app provides VPN protection, Wi-Fi security assessments, and checks on built-in iPhone security settings but does not function as antivirus software. It enhances existing Apple security measures by addressing vulnerabilities related to insecure Wi-Fi connections and unprotected internet access. The app is accessible to both new and existing subscribers, and Intego is currently offering a 50% discount on subscriptions until September 30, 2026. Intego ONE is available in three tiers: Essential, Advanced, and Complete, with the Complete tier including the new iPhone app. The app features a VPN that encrypts internet connections on public Wi-Fi, Wi-Fi security checks, and assessments of iPhone security settings. While traditional viruses are rare on iPhones, threats like spyware and exploits still exist. The app does not replace Apple's malware protection but complements it. Intego ONE Complete is recommended for Mac and iPhone owners, particularly those who travel frequently or connect to public Wi-Fi. The pricing includes various deals, with a 50% discount currently available and a subsequent 35% discount after the promotional period.
AppWizard
September 4, 2026
The Indian Cyber Crime Coordination Centre (I4C) has issued an advisory about malicious Android applications disguised as adult-content apps, which are promoted through social media and distributed outside official app stores. The National Cybercrime Threat Analytics Unit (NCTAU) warned that these apps can compromise mobile device security by requesting sensitive permissions and may install additional software without user consent, leading to unauthorized financial transactions. Users are advised to download apps only from trusted sources like the Google Play Store, avoid installing APK files from unverified sources, and refrain from granting accessibility permissions to untrusted applications. Recommendations include regularly reviewing installed apps, keeping Google Play Protect enabled, and monitoring bank accounts for unauthorized activities. Victims of cyber fraud are encouraged to report incidents via the national cybercrime helpline or the government’s reporting portal.
Search