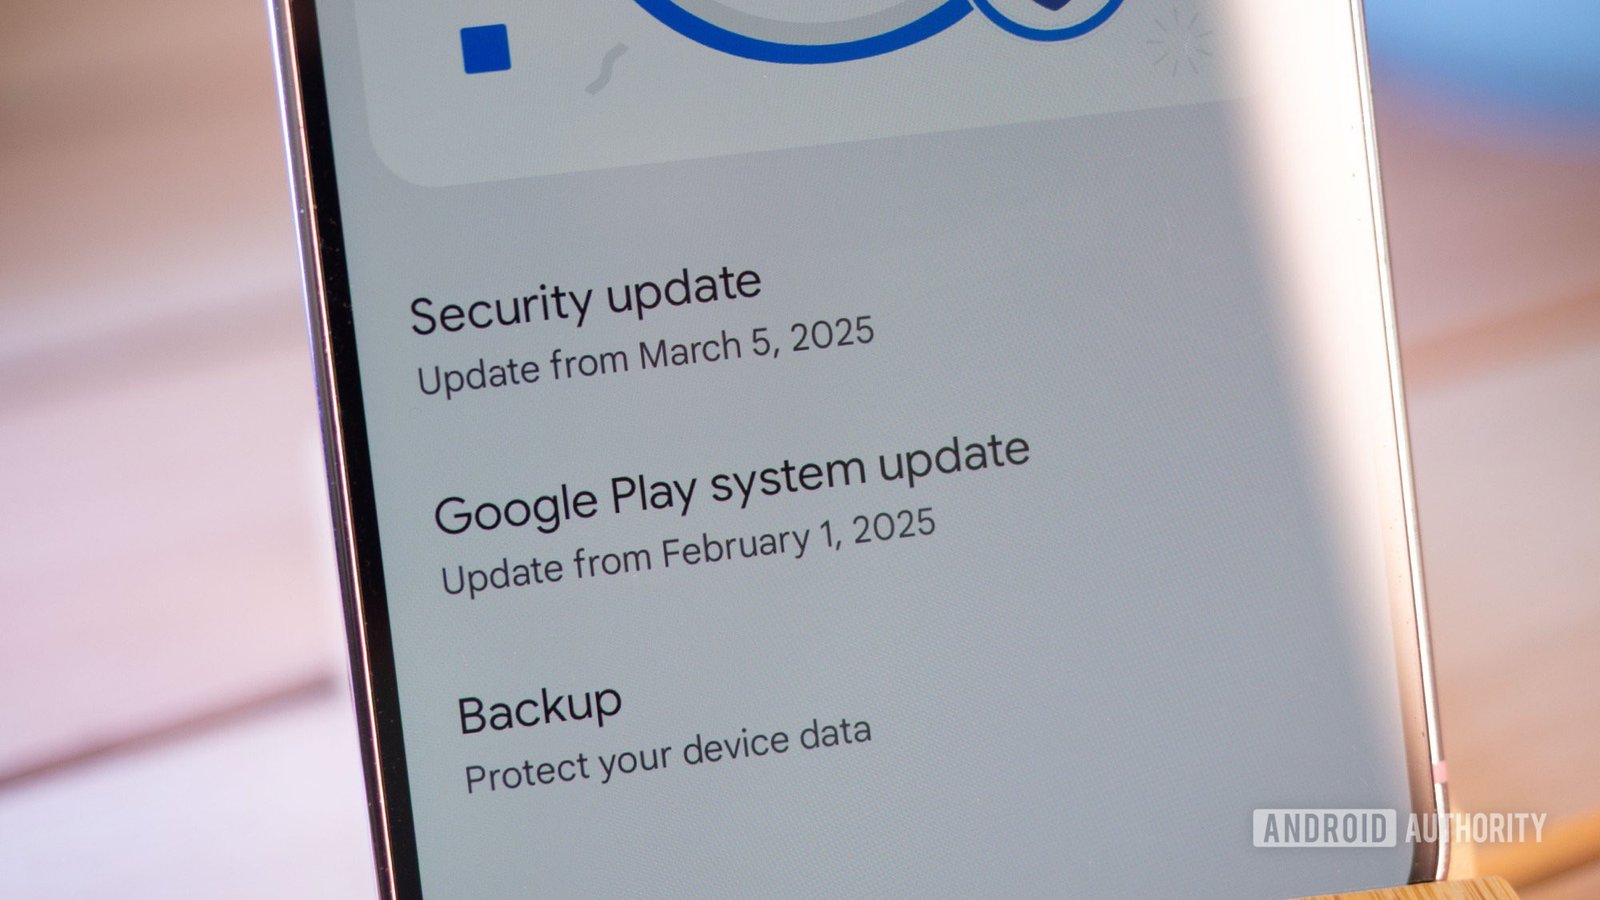
Google has introduced a significant enhancement to Android’s security framework with the launch of its AndroidX Security State and Security State Provider libraries. These tools empower applications to assess the security status of individual components within an Android device, moving beyond the traditional reliance on the overall security patch level.
Enhanced Security Insights for Apps
Previously, the security patch level and its corresponding date were the primary indicators for apps and businesses to determine whether a device was up to date. However, this method often failed to provide a complete picture. Android’s architecture allows for the independent updating of various operating system components, with some updates being delivered directly from manufacturers and others through Google Play, without necessitating a full system overhaul.
With the new libraries, applications can now delve deeper into the security state of a device. They can verify which specific security fixes are installed, identify the latest available updates, and check if any updates are pending installation. This capability is particularly beneficial for applications where security is paramount, such as banking software.
- For instance, a banking app could verify the presence of a specific security fix before permitting sensitive transactions.
- If an update is available but not yet installed, the app could prompt the user to install it, rather than simply refusing to proceed.
Moreover, the libraries enable apps to check for the resolution of specific security vulnerabilities, identified as Common Vulnerabilities and Exposures (CVEs). This means that critical fixes related to NFC or Bluetooth can be confirmed before allowing functionalities like tap-to-pay or data sharing.
Phone manufacturers will also benefit from this new framework. They can now communicate specific security fixes to Android without altering the overall security patch date. This means that a device might display an outdated patch date while still having resolved certain vulnerabilities.
While these advancements may not be immediately noticeable to the average user, they represent a significant step towards a more nuanced understanding of device security. Over time, applications will gain a clearer insight into the actual protection status of a phone, independent of the traditional patch date metric.