device settings

AppWizard
September 19, 2026
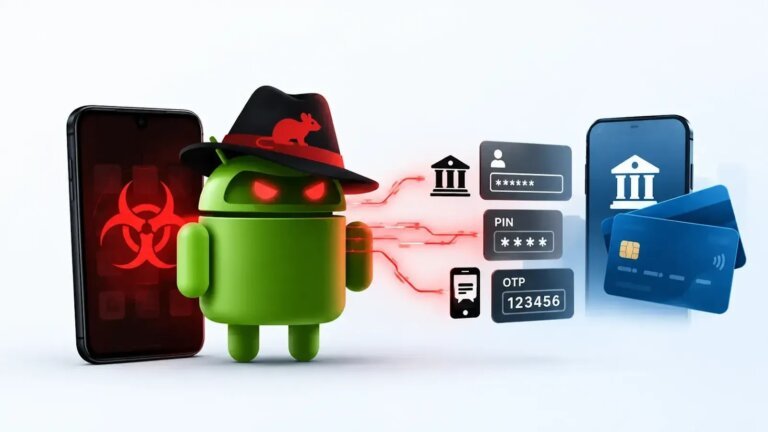
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
Tech Optimizer
September 16, 2026
Intego has reduced the price of its top-tier Mac security plan, the Intego ONE “Complete” plan, to half its usual cost during the back-to-school season. The plan, which covers one Mac and one iPhone, is now priced at .99 for a year, down from .99. A two-year subscription is available for .98, reduced from 9.99, equating to .74 per month. The promotion does not require a discount code, as the price is automatically applied at checkout, and it includes a 30-day money-back guarantee, valid until September 30. The “Complete” plan features Intego VPN and an iPhone app, providing comprehensive protection even when the laptop is not in use. The VPN encrypts internet traffic and conceals the user's IP address, while the iPhone app audits device settings and includes a Wi-Fi security check. Intego acknowledges that macOS has built-in security features and positions its antivirus as a complementary layer. The plan is particularly beneficial for users who travel frequently or connect to public Wi-Fi.
AppWizard
September 14, 2026
Malicious Android applications are being promoted through social media advertisements, particularly on platforms like Instagram and Facebook, posing significant risks to users. The Indian Cyber Crime Coordination Centre (I4C) has warned about deceptive apps advertised under names such as Night Play, Reloop, Kyss, Vimo, Rivo, Nezo, and Vixa, which often redirect users to pornographic websites to download APK files. These applications can exploit sensitive device permissions, leading to malware infections, unauthorized financial transactions, and various forms of cyber fraud. Users may be tricked into granting accessibility permissions that allow the malware to operate in the background and potentially install a VPN, rerouting internet traffic through servers controlled by attackers. Cybersecurity experts advise users to verify the legitimacy of applications before installation and to be cautious of permissions requested by unknown apps.
AppWizard
September 10, 2026
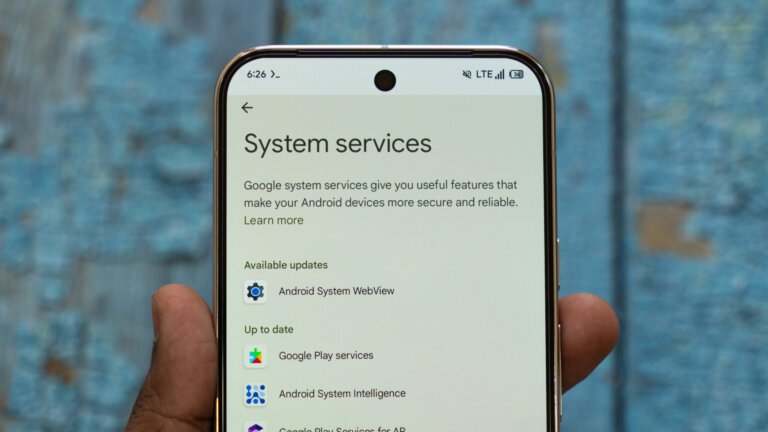
On September 9, 2026, Google rolled out the “Google Play System Update” for Android devices, which is part of the monthly “Google System Updates” aimed at enhancing security and reliability. The update reflects an “Update date: September 1, 2026,” and includes improvements to the app version of “Mainline services,” updated to version v2026-09-01S+. Users can check for the update in device settings under [Security & privacy] → [System & updates] → [Google Play system update], or through the “Mainline services” app, available since November 19, 2025.
AppWizard
September 6, 2026
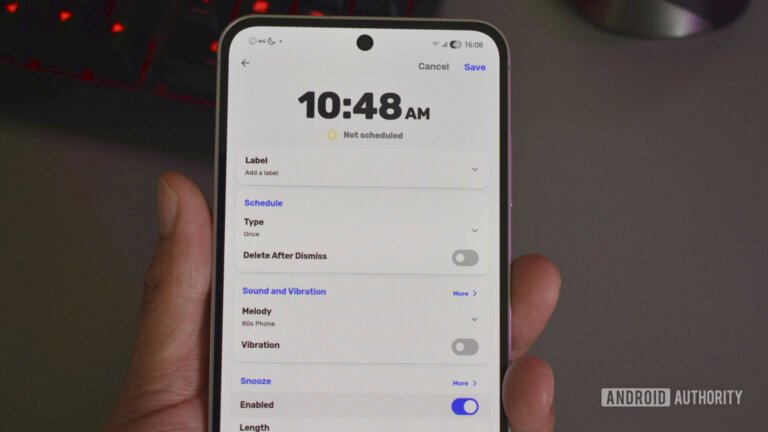
Many users prefer default applications for calendars, messaging, and clocks, but third-party options like Chrono offer enhanced experiences. Chrono is an open-source clock application that provides a user-friendly interface, extensive alarm features, and an ad-free experience, but it is not available on the Google Play Store. The app features four tabs: Alarm, World Clock, Timer, and Stopwatch, with customization options including dark mode and Material design. Users can personalize the app's appearance and tag alarms for organization. Chrono's alarm functionality includes assertive alarms that require tasks to be completed before turning off, adjustable snooze intervals, and the ability to lock alarms. To download Chrono, users must visit the F-Droid website, download the app, and follow installation instructions. Updating Chrono through F-Droid is straightforward, while sideloaded users must check for updates manually or use a tool like Obtainium.
AppWizard
September 4, 2026
The Indian Cyber Crime Coordination Centre (I4C) has issued an advisory about malicious Android applications disguised as adult-content apps, which are promoted through social media and distributed outside official app stores. The National Cybercrime Threat Analytics Unit (NCTAU) warned that these apps can compromise mobile device security by requesting sensitive permissions and may install additional software without user consent, leading to unauthorized financial transactions. Users are advised to download apps only from trusted sources like the Google Play Store, avoid installing APK files from unverified sources, and refrain from granting accessibility permissions to untrusted applications. Recommendations include regularly reviewing installed apps, keeping Google Play Protect enabled, and monitoring bank accounts for unauthorized activities. Victims of cyber fraud are encouraged to report incidents via the national cybercrime helpline or the government’s reporting portal.
AppWizard
August 9, 2026
Third-party advertising tools embedded in Android applications are automatically collecting location data, often without the app developers' awareness. Software development kits (SDKs) used for advertising come with location data collection enabled by default, unless developers actively disable this feature. Historical location data has been sold to military and intelligence agencies, including the FBI, and used in immigration enforcement actions in the US. The Electronic Frontier Foundation (EFF) reported that app-level location permissions do not provide meaningful consent for location collection by third-party advertising SDKs. The EFF identified four advertising SDKs—InMobi, BidMachine, Verve's HyBid, and Huawei's Petal Ads—that collect and share location data by default. Two analyzed apps had been downloaded 60 million times without providing a privacy notice or seeking user consent for third-party location sharing. Users can manage location permissions through their device settings, but the EFF emphasizes that developers should ensure user data is not shared by default.
Search