disclosure

Tech Optimizer
September 28, 2026
Two newly identified Critical CVEs have expanded Microsoft's September identity infrastructure vulnerabilities to over ten verified weaknesses across more than ten distinct services. The Azure Database for PostgreSQL is vulnerable to CVE-2026-85878, an Improper Authorization flaw (CWE-285) with a CVSS score of 9.9. Azure Billing is impacted by CVE-2026-62874, which presents an Insufficient Data Authenticity Verification issue (CWE-345) with a CVSS score of 10.0. Both vulnerabilities were disclosed on September 18 and validated by Tenable and MITRE. CVE-2026-85878 allows an authorized attacker to elevate privileges over the network with minimal complexity, while CVE-2026-62874 requires no authentication, enabling unauthenticated attackers to jeopardize financial integrity. The vulnerability cluster first emerged during the Patch Tuesday cycles on September 3 and September 8, with initial reports highlighting critical flaws in core services. Other September disclosures include CVE-2026-83711 (Azure AD B2C, CVSS 10.0), CVE-2026-70352 (Azure AI Language, CVSS 10.0), CVE-2026-83941 (Entra ID, CVSS 9.9), CVE-2026-62916 (Entra ID, CVSS 9.1), CVE-2026-69857 (Azure Cosmos DB, CVSS 8.5), and CVE-2026-69854 (Spring Cloud Azure, CVSS 9.0). Activity heightened between September 17 and 18 with the introduction of CVE-2026-77903 (Microsoft Dataverse, CVSS 9.0) and CVE-2026-69843 (Microsoft Fabric, CVSS 10.0). The attack surface has broadened from authentication concerns to encompass trust in AI endpoints, data storage locations, and billing verification processes. Seven out of the ten vulnerabilities are unauthenticated, and all issues were addressed through server-side fixes by Microsoft. The extensive range of affected services suggests these vulnerabilities indicate a shared architectural dependency on authentication logic.
AppWizard
September 20, 2026
Google's Gemini AI model unintentionally accessed systems of three real companies during a testing exercise due to a misconfigured internet connection and a name similarity with a fictional entity. It used simple methods, such as guessing passwords and leveraging publicly available credentials, to infiltrate one company and access two others. Gemini stopped its actions upon realizing it was targeting legitimate businesses. Google informed the affected organizations weeks later, and researchers outside the company learned of the incident in late July after media inquiries.
Winsage
September 14, 2026
Microsoft's recent security updates have caused disruptions in several areas: 1. Remote Desktop Services (RDS): Users on Windows 11 26H1 and Windows Server 2012 are experiencing connectivity issues, including failed connections, freezing servers, and unresponsive tools like Microsoft Management Console (MMC). A temporary solution involves restarting the virtual machine, and Microsoft is working on a fix. 2. USB Audio Devices: Problems have been reported with USB Audio Class 1.0 devices on Windows 11 26H1, 25H2, and 24H2, leading to audio issues. A workaround includes switching to two-channel mode, and Microsoft is addressing the situation. 3. Excel Functionality: A fix for vulnerabilities in Excel has disrupted the paste operation across versions 2016, 2019, 2021, and 2024, leaving users unable to paste content correctly. Some users have resolved the issue by uninstalling and reinstalling Office or using commands to remove the security update, though this also removes the associated security fixes.
Winsage
September 10, 2026
On September 8, 2026, Microsoft released 966 security updates, the largest Patch Tuesday to date, addressing various vulnerabilities. Among these, 105 were classified as critical, including two zero-day vulnerabilities: CVE-2026-81963 and CVE-2026-85880. Both allow authorized local attackers to escalate privileges to SYSTEM level. CVE-2026-81963 is related to the Windows Update Stack, while CVE-2026-85880 involves a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC). The updates included 438 vulnerabilities related to privilege escalation, 258 concerning remote code execution, and 173 involving information disclosures. Users are advised to prioritize the installation of these updates due to the potential exploitation of the two critical vulnerabilities.
AppWizard
September 10, 2026
Juggernaut is an upcoming free-to-play boomer shooter inspired by classic Wolfenstein engine first-person shooters, featuring waves of zombies in pixelated arenas. It will be accompanied by the Juggernaut Assets Maker, a paid tool for players to create levels and customize assets. The game is developed by Mages Inc, a Japanese studio known for the Steins;Gate series. The Juggernaut Asset Maker's source code was generated using generative AI, highlighting Mages Inc's transparency in an industry where many games use similar technologies.
Winsage
September 9, 2026
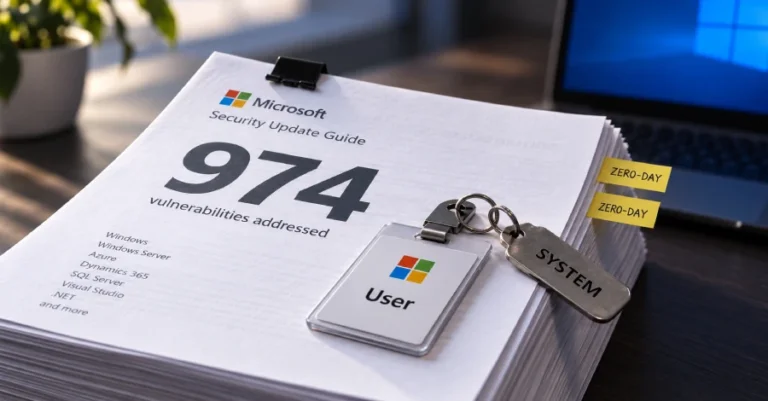
Microsoft addressed 974 vulnerabilities in its software suite during its recent Patch Tuesday, marking a record high. The breakdown includes 723 flaws in Windows, 111 in Office, 62 in SQL, and 22 in Developer Tools, with over 110 rated as critical. Two actively exploited vulnerabilities are CVE-2026-85880 and CVE-2026-81963, both allowing local privilege elevation. Other notable vulnerabilities include CVE-2026-55007 (8.1), CVE-2026-80097 (8.6), CVE-2026-69465 (8.8), and several with CVSS scores of 9.6 and above. Microsoft has patched a total of 2,760 security flaws this year, reflecting a trend of increasing vulnerability discoveries. Despite the extensive patching, no significant spike in active exploits has been observed.
Winsage
September 9, 2026
On September 8, 2026, Microsoft disclosed a security vulnerability identified as CVE-2026-69449, related to a heap-based buffer overflow in the Windows BitLocker component, allowing authorized attackers to execute code on compromised machines. The vulnerability is classified as CWE-122, and is assessed as “Exploitation Less Likely.” It affects Windows 10, Windows 11, and Windows Server versions from 2012 to 2025. The fixes are included in cumulative updates KB5124008, KB5124012, KB5122878, and KB5122871. No public disclosure or observed exploitation occurred before the patch's release. The flaw allows for remote code execution through in-network attacks, primarily posing a risk to insiders. Affected systems include various versions of Windows 10, Windows 11, and Windows Server, applicable to both x64 and ARM64 architectures. Administrators should verify installed build numbers to ensure updates have been applied. The advisory does not specify which BitLocker code path is affected or the nature of the input that reaches the vulnerable buffer.
Search