DLL

Winsage
September 17, 2026
The search index on Windows 11 can contribute to storage bloat, with reported sizes varying significantly among users. The search index database, named Windows.db, is crucial for delivering quick search results and can grow dramatically, with some users experiencing sizes exceeding 200GB. A PowerShell script can be used to check the size of the Windows.db file. If the file size is unusually large, users can rebuild the search index through the Indexing Options in the Control Panel. Windows 11 has two indexing modes: Classic and Enhanced, which affect the size and number of indexed items. Classic mode indexes specific folders, while Enhanced mode indexes the entire PC. Excluding certain directories can help manage index size. Performance issues may arise on PCs with over 400,000 indexed items.
Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
Winsage
September 9, 2026
Recent investigations have identified the BlueMoon exploit kit, used by espionage-driven threat activity clusters, particularly linked to APT31, a China-aligned state-sponsored group, since August 28, 2026. BlueMoon exploits three vulnerabilities: CVE-2026-85046 (a type confusion vulnerability in Google Chrome's V8 engine), an unassigned V8 sandbox escape, and CVE-2026-85880 (a heap-based buffer overflow in Windows ALPC). Google and Microsoft have released patches for these vulnerabilities, which were exploited as "patch-gap" zero-days. The attack vectors typically begin with phishing emails that lead victims to malicious URLs, triggering the vulnerabilities for code execution and privilege escalation. Variants of BlueMoon have been detected, featuring modifications for specific campaigns. Notable attack chains include: - APT31 targeting NGOs and mining firms in the U.S. with a malicious browser add-on called GemStone. - UNK_LateNight targeting U.S. aerospace companies, deploying BlueMoon alongside the ShadowPad backdoor. - UNK_DoubleCheck targeting a Vietnamese manufacturer, using DLL sideloading to execute a Rust binary. - UNK_QuietRacket targeting government and financial organizations in Indonesia and Singapore, modifying BlueMoon to execute a .NET assembly. CISA added the Chrome flaw to its Known Exploited Vulnerabilities catalog on September 4, 2026, requiring federal agencies to apply patches by September 18, 2026. Indicators of compromise include specific process trees, files, folders, scheduled tasks, mutexes, and registry keys. Proofpoint has released detection rules to help organizations identify and mitigate these threats.
Winsage
September 6, 2026
Users can customize icons in Windows 11 by following different methods depending on the type of icon. For folders and shortcuts, right-clicking the item and selecting Properties allows users to change icons easily. Taskbar items require pressing Shift while right-clicking the closed app. Desktop icons like "This PC" and the Recycle Bin can be modified through Settings > Personalization > Themes > Desktop icon settings. More complex changes, such as altering icons for file types or drives, involve editing the Windows registry. Windows retains a selection of classic icons within DLL files, including moricons.dll, pifmgr.dll, and netshell.dll. Users can also access the Windows Icon Archive project for a repository of icons from various Windows versions, though .png files need conversion to .ico format for use. Limitations include the inability to change icons for new folders automatically, modifications not reflecting in Quick Access for special folders, and restrictions on altering application icons. Programs like OpenShell can help modify taskbar and Start menu icons, but achieving a perfect replica of older versions is not possible.
Tech Optimizer
September 5, 2026
The cyber threat group Silver Fox is distributing the ValleyRAT backdoor disguised as a legitimate signed Chinese adware application, specifically bundled with the QN Wallpaper tool. This malware allows attackers to gain comprehensive control over infected machines, enabling them to collect sensitive information, capture screenshots, and deploy additional malicious modules. The attack utilizes DLL sideloading, where a modified version of QN Wallpaper loads a malicious DLL from the same directory, circumventing signature-based security measures. The installer disables Windows Defender, adds itself to autorun entries, and uses the "runas" command to elevate privileges if the user lacks administrator rights. ValleyRAT also marks its process as critical, potentially causing a blue screen of death if terminated. Kaspersky has identified Silver Fox as the likely perpetrator of this campaign, known for similar techniques.
AppWizard
September 4, 2026
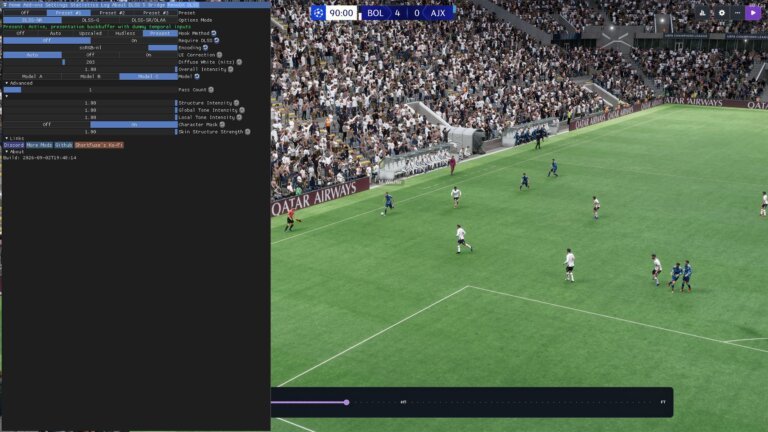
Future and its syndication partners may earn a commission when purchases are made through links in their articles. The Control mod has led to experimentation with DLSS 5 .dll files among gamers, resulting in varied visual outcomes. For example, integrating DLSS 5 into The Blood of Dawnwalker caused visual distortions in characters. The early access version of NBA 2K27 has prompted modders to create game-agnostic versions of DLSS 5, allowing integration into various titles. DLSS 5 can produce impressive visual effects when used correctly, but it significantly impacts performance, potentially reducing frame rates by 50-60%. For instance, using DLSS 5 on an RTX 5090 dropped frame rates from 110 fps to below 50 fps. In Football Manager 26, DLSS 5 improves environmental lighting, pitch details, and player profile pictures. The installation of DLSS 5 can be done through the ReShade HDR Installer from GitHub, simplifying the process. Players can customize DLSS 5 settings in-game using the RenoDX tab. However, there are concerns about how such modifications may affect the original artistic vision of the games.
AppWizard
September 4, 2026
The integration of DLSS 5 .dll files into various games has produced mixed results, with some enhancements working well while others cause visual glitches. A review of The Blood of Dawnwalker revealed issues with the DLSS pipeline, resulting in an unexpected undead appearance for a character. A demonstration at Gamescom showed that DLSS 5 can significantly enhance visuals when used correctly, particularly with Model C at 60-70% intensity. However, Nvidia has noted that DLSS 5 can lead to a 50-60% reduction in frame rates, especially at 4K resolution. For example, on an RTX 5090, frame rates dropped from approximately 110 fps to below 50 fps with DLSS 5 activated. DLSS 5 can also run on lower-spec GPUs, although it was initially demonstrated with dual RTX 5090s. In Football Manager 26, DLSS 5 improved visuals without achieving photorealism, maintaining a steady 60 fps. The ReShade HDR Installer allows users to integrate DLSS tools into unsupported games, but results may vary and troubleshooting may be necessary. The official release of DLSS 5 will not include the fine-tuning sliders available through ReShade, which could complicate the preservation of developers' artistic intent. For best results, users should use the Upscaled or DLSS version of DLSS-NR rather than the 'Present' method, and may need to try different RenoDX DLSS 5 tools if issues arise.
Winsage
September 4, 2026
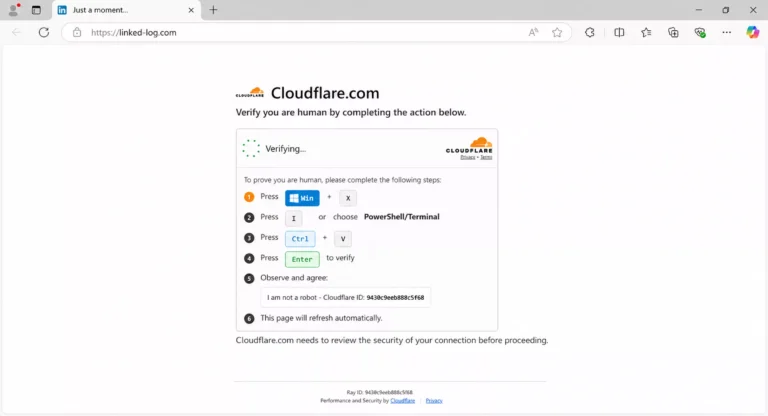
Microsoft has identified a new malware campaign called TerminalFix that uses fake CAPTCHA prompts to trick Windows users into executing malicious commands. This campaign is a variation of ClickFix attacks and employs deceptive pages that impersonate reputable services like Cloudflare. Instead of traditional CAPTCHA challenges, users are instructed to open PowerShell or Command Prompt and paste in commands, allowing attackers to execute complex scripts more easily. TerminalFix initiates a multi-stage intrusion, granting attackers persistent proxy access to the infected machine, which can lead to further exploitation of the company's network. The campaign relies on social engineering tactics, requiring user compliance with counterfeit verification instructions. Microsoft has released mitigation guidance, recommending restrictions on PowerShell access, monitoring for DLL sideloading, blocking outdated Flash plugins, and enabling cloud-delivered protection in Microsoft Defender Antivirus. The campaign poses significant risks to enterprise networks, but individual users should also be cautious about executing commands requested by websites.
Search