elevation

AppWizard
September 15, 2026
Android Auto enhances the in-vehicle experience for drivers, including motorcycle riders, with compatible apps designed for their needs. Sygic offers a Motorbike Mode for navigation, allowing riders to choose scenic routes and providing real-time data like lean angles and weather conditions. It integrates with Android Auto and requires a one-time fee for the Motorbike Mode. The app has over 50 million downloads and a 4.1-star rating. Calimoto is a navigation and route-discovery app for bikers that uses user-generated content to offer routes. It tracks essential ride data and integrates with Android Auto, displaying routes on the dashboard. The app has over one million downloads and a 4.3-star rating, though some users report issues with user-submitted routes. AccuWeather provides real-time weather alerts tailored for motorcycle riders, helping them anticipate adverse conditions. It integrates with Android Auto to display current weather and forecasts. The app has over 100 million downloads and a mixed 3.5-star rating, with a free version available. Campendium is a resource for finding campgrounds and overnight parking, featuring over 70,000 locations in the U.S. and Canada. It provides information on amenities and integrates with Android Auto for navigation. The app has mixed reviews and an overall rating of 1.8 stars. The selection of these Android Auto apps focused on enhancing the riding experience for motorcycle riders, evaluating features and integration with Android Auto.
Winsage
September 15, 2026
Microsoft has released an emergency patch for Windows 11, identified as KB5129195, which is being automatically downloaded to address critical issues, including privilege elevation vulnerabilities. The patch fixes CVE-2026-62721 and resolves remote desktop connection problems, as well as attempts to address USB audio issues that arose after the September update. Improvements have been noted for 8-channel and 3D audio modes, but users may still face problems such as missing volume controls and lack of audio output for some USB audio devices. Additionally, unresolved issues from the September update, KB5124008, persist, particularly for AMD Radeon GPU users experiencing system freezes, crashes, and driver timeouts. Complaints about File Explorer crashing or failing to launch have also been reported, affecting certain enterprise environments. Microsoft is using internal AI tools to enhance security, but this has led to a cycle of instability in the operating system. Nearly 1,000 CVE patches were applied just before this update.
Winsage
September 15, 2026
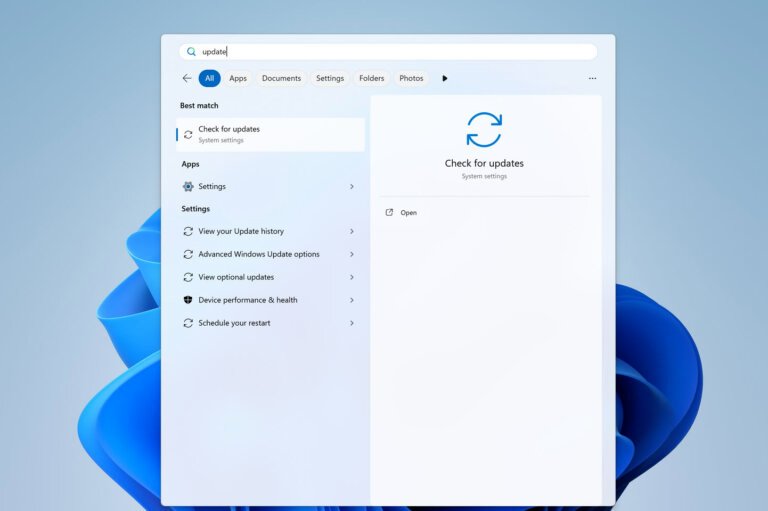
Microsoft has released out-of-band updates for Windows 11 versions 26H1, 25H2, and 24H2 to address security vulnerabilities and improve system performance. The KB5129194 patch for version 26H1 fixes a critical elevation-of-privilege vulnerability (CVE-2026-62721) related to the Windows User-Mode Power Service (UMPS). The KB5129195 update for versions 25H2 and 24H2 also addresses a similar UMPS vulnerability and resolves a connection issue with Remote Desktop Services. Additionally, the updates fix problems with multichannel audio features on certain USB Audio Class 1.0 devices. These updates include enhancements from the September 2026 Patch Tuesday release, such as Taskbar customization, a faster Windows Search experience, and new Start Menu options. Users with unmanaged PCs will receive these updates automatically but can also check for updates manually.
Winsage
September 10, 2026
Microsoft's Patch Tuesday on September 8, 2026, addressed two critical Windows privilege escalation vulnerabilities: CVE-2026-85880 and CVE-2026-81963, both with a CVSS score of 7.8. CVE-2026-85880 is a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC), allowing attackers with low-privilege local access to escalate privileges to SYSTEM. CVE-2026-81963 involves improper link resolution in the Windows Update Stack, enabling similar privilege escalation. Both vulnerabilities require no user interaction and have been actively exploited prior to the patch release. CISA added them to its Known Exploited Vulnerabilities catalog on September 8, 2026, with a remediation deadline of September 22 for U.S. federal agencies. CVE-2026-85880 affects various Windows 10 and Server versions but excludes Windows 11 and Windows Server 2025. CVE-2026-81963 impacts newer Windows platforms, including Windows 11 and Windows Server 2025. Microsoft released security updates for both vulnerabilities on September 8, 2026, and organizations are advised to prioritize these updates. Security teams should monitor for signs of privilege escalation and unusual SYSTEM-level activities related to these vulnerabilities.
Winsage
September 9, 2026
Microsoft addressed 974 vulnerabilities in its software suite during its recent Patch Tuesday, marking a record high. The breakdown includes 723 flaws in Windows, 111 in Office, 62 in SQL, and 22 in Developer Tools, with over 110 rated as critical. Two actively exploited vulnerabilities are CVE-2026-85880 and CVE-2026-81963, both allowing local privilege elevation. Other notable vulnerabilities include CVE-2026-55007 (8.1), CVE-2026-80097 (8.6), CVE-2026-69465 (8.8), and several with CVSS scores of 9.6 and above. Microsoft has patched a total of 2,760 security flaws this year, reflecting a trend of increasing vulnerability discoveries. Despite the extensive patching, no significant spike in active exploits has been observed.
Winsage
September 9, 2026
The September 2026 security cycle revealed a bifurcated approach to vulnerability management by Microsoft, focusing on cloud-side identity services with silent mitigations and traditional Patch Tuesday updates for on-premises Windows infrastructure. On September 3, Microsoft addressed nine cloud-side vulnerabilities, including two with a CVSS score of 10.0: CVE-2026-83711 (Azure AD B2C elevation of privilege) and CVE-2026-70352 (Azure AI Language Authoring missing authentication). Additionally, CVE-2026-83941 (Entra ID elevation of privilege, rated 9.9) and CVE-2026-80098 (Copilot Studio cryptographic flaw) were noted. On September 8, the Patch Tuesday update addressed 70 CVEs, including critical issues in the on-premises stack, such as CVE-2026-83939 (Windows Secure Kernel Mode elevation of privilege). CVE-2026-69414 (ShieldBreak), an elevation of privilege vulnerability in the Defender Malware Protection Engine, was patched out-of-band on September 3 after being publicly exposed for three weeks. Microsoft is shifting its Self-Service Password Reset (SSPR) enforcement to default to passkeys as of September 7, with plans to phase out SMS and voice-based authentication by February 2027. This aims to enhance security by moving away from legacy credentials.
Winsage
September 9, 2026
Microsoft's September 2026 security update revealed 973 vulnerabilities, with 113 classified as critical. Two actively exploited vulnerabilities are CVE-2026-81963 (Windows Update Stack, elevation of privilege, CVSS 7.8) and CVE-2026-85880 (Windows ALPC, elevation of privilege, CVSS 7.8). Among the 113 critical vulnerabilities, 82 are remote code execution (RCE) vulnerabilities. Notable vulnerabilities include: - CVE-2026-69676: RCE in Windows Kerberos, CVSS 8.8, authentication bypass. - CVE-2026-69852: RCE in Windows RRAS, CVSS 7.5, heap-based buffer overflow. - CVE-2026-72957: RCE in Windows Deployment Services, CVSS 7.8. - CVE-2026-69854: Elevation of privilege in Spring Cloud Azure, CVSS 9.0, improper authentication. - CVE-2026-83501: Information disclosure in Windows VBS, CVSS 5.5. - CVE-2026-69730: RCE in Windows DNS Server, CVSS 9.8. Less likely to be exploited vulnerabilities include: - CVE-2026-69845: RCE in Windows DHCP Server, CVSS 9.8, heap-based buffer overflow. - CVE-2026-65772: Vulnerability in Microsoft Dynamics 365 On-Premises, CVSS 8.8, deserialization of untrusted data. - CVE-2026-66302: RCE in Skype for Business, CVSS 9.8. Additional critical vulnerabilities include: - CVE-2026-62916: Elevation of privilege in Microsoft Entra ID, CVSS 9.1. - CVE-2026-83941: Elevation of privilege in Entra ID, CVSS 9.9. - CVE-2026-80098: Vulnerability in Copilot Studio, CVSS 9.3, improper verification of cryptographic signatures. Talos is releasing a new Snort ruleset to detect attempts to exploit these vulnerabilities, with specific SIDs for Snort 2 and Snort 3 rule coverage.
Winsage
September 8, 2026
Microsoft released its September 2026 Patch Tuesday updates for Windows 11, focusing on versions 26H1 and 25H2/24H2. Key features include: - Taskbar customization for versions 25H2 and 24H2, allowing users to choose the taskbar's location and size. - Faster Windows Search with options to hide web and Microsoft Store suggestions. - Touch scrolling support in the "Recommended" section of File Explorer. - Start Menu customization options for size and visibility of sections. - Stability improvements for Microsoft Teams and Outlook on Arm64 PCs. For version 26H1, updates include: - Improved app search and Settings relevance in Windows Search. - Voice Isolation technology in Voice Access. - Updated taskbar notification badges and Weather widget display on the Lock Screen. - New gesture controls for Precision Touchpads. - Enhanced Sign-in Security supporting peripheral fingerprint sensors. - Optimized Windows Update progression calculations and clean-up logic. - Power settings allowing users to set energy saver activation thresholds. Microsoft is using AI to identify vulnerabilities, with 997 Common Vulnerabilities and Exposures reported, including one actively exploited vulnerability (CVE-2026-81963). Windows 11 version 26H2 has been made available to Insiders, with a public rollout expected next month.
Winsage
September 8, 2026
Microsoft released its September 2026 security updates, addressing two critical Windows elevation-of-privilege vulnerabilities: CVE-2026-85880 and CVE-2026-81963. Both vulnerabilities were exploited before their public disclosure on September 8. CVE-2026-85880 involves a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC), allowing low-privileged attackers to gain SYSTEM privileges. CVE-2026-81963 affects the Windows Update Stack due to improper link resolution and access controls, enabling similar privilege escalation. The September release also includes 974 Common Vulnerabilities and Exposures (CVEs) across various Microsoft products, with 723 affecting Windows. Users of Windows 11 24H2 and 25H2 receive updates via KB5124008, while Windows 11 26H1 receives KB5124012. Windows 11 24H2 Home or Pro editions will reach end of servicing on October 13, 2026. Users are advised to install the updates promptly and back up important data.
Search