Escape

Winsage
September 24, 2026
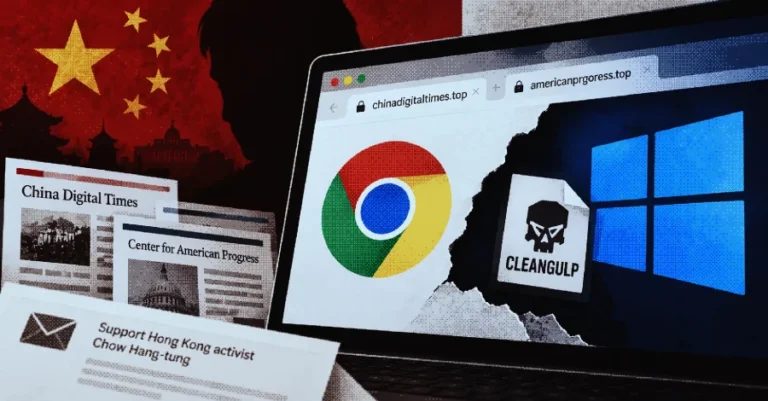
A Chinese threat actor, codenamed UTA0565, has exploited newly disclosed vulnerabilities in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) through deceptive websites, achieving remote code execution. The attacks were detected on September 3 and 4, 2026, and involved impersonating organizations to mislead victims, particularly targeting Asian government entities with phishing emails related to Hong Kong activist Chow Hang-tung. The phishing messages directed users to fraudulent sites that loaded an HTML element using the BlueMoon exploit kit, which delivered a payload named "chrome_cleanup.exe," associated with the CLEANGULP malware family. This malware allows for command execution, process listing, file uploads and downloads, and uses a hard-coded domain for command-and-control communications. The exploit's widespread use suggests a coordinated effort within the Chinese cyber espionage community, with indications that multiple groups are sharing and weaponizing the exploit.
AppWizard
September 23, 2026
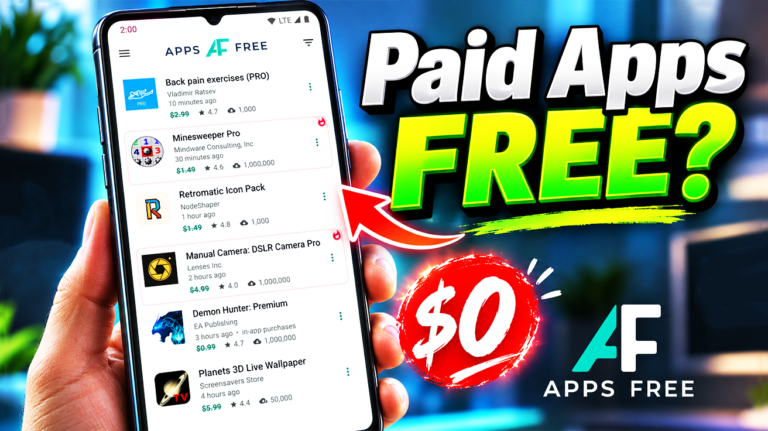
More than 70% of the world’s smartphones operate on the Android platform. Users often struggle to find apps that address specific issues, leading to a time-consuming search through numerous options. A curated list presents five applications that provide practical solutions to common mobile frustrations. 1. AppsFree: Monitors Google Play for premium apps, games, and wallpapers that temporarily drop to free, allowing users to snag deals that would otherwise be missed. Developed by ts-apps GmbH, it enables users to blacklist developers and filter low-quality offers. 2. Monocles Browser: Prioritizes user privacy by disabling JavaScript and cookies by default, reducing tracking. It has an APK size of approximately 13–14 MB and integrates ad blocking and supports Tor/Orbot proxy networks. Created by Arne-Brün Vogelsang, it offers a clean browsing experience. 3. Amarok: Allows users to instantly hide files and applications without resource-intensive encryption by obfuscating filenames and signatures. It supports multiple hiding modes and includes a “panic button” feature for quick data concealment. 4. Buckwheat: Budget manager: Requires manual input of total budget and days to cover, promoting financial reflection. It calculates daily spending allowances and provides detailed analytics. Developed by Danil Zakhvatkin, it has a user rating of around 4.6–4.7/5. 5. Chill Live Wallpaper: Offers minimalist landscapes that sync with local time and weather, providing a visually soothing experience. Compatible with Android 7.1+, it is ad-free and has a compact APK size of 5–6 MB.
AppWizard
September 20, 2026
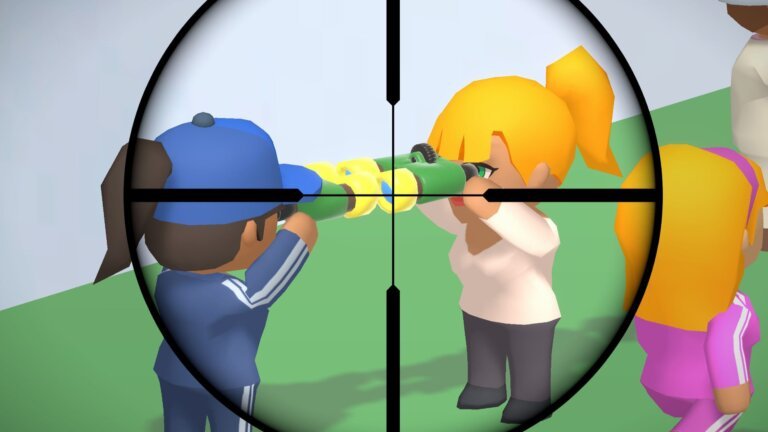
Sniper Dan is a game developed by Denki that combines hidden-object puzzles with first-person shooting mechanics. Players identify problems and resolve them with shots, engaging in quirky tasks like clearing leaves or planting seeds. The game features amusing animations and rewards players with coins for upgrades and cosmetic items. It is currently priced at £8.79, available until October 1.
Winsage
September 19, 2026
New Windows 11 Insider Preview builds have been released for the Beta and Experimental channels. Notable new features include: - A new animation for the Mouse indicator in the Experimental channel, which can be activated through accessibility settings and kept visible until the escape key is pressed. - A new contrast theme toggle in the Magnifier, also in the Experimental channel, designed to reduce screen glare without altering the appearance of images, charts, and videos. - Updates to the Cloud rebuild feature in the Experimental channel, allowing users to restore their Windows 11 PC to a clean state and sanitize device drives during the process. IT administrators can now configure and initiate Cloud rebuild remotely via the Recovery CSP.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
AppWizard
September 16, 2026
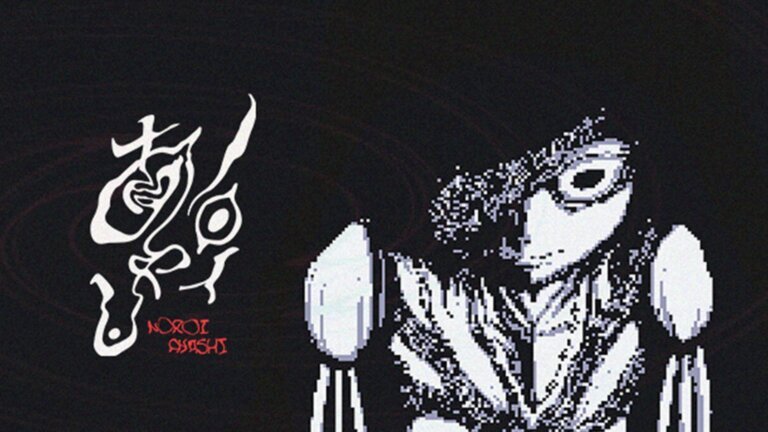
Game Source Entertainment, in collaboration with SuperNiche and Clover Lab, is set to release a game titled Noroi Ayashi: The ∞th Oddity in 2027. It is a "time-loop horror RTA stealth action adventure" available on Switch 2, Switch, and PC via Steam, supporting English, Japanese, Traditional Chinese, and Simplified Chinese. The protagonist, Seira, explores her school at night, facing seven mysteries and the curse of a doll named Aya. The narrative is told through Yuriko, a member of the U High School News Club, who investigates the urban legend of the Cursed Doll Aya. Key characters include Seira, Hime, and Tae, each with distinct traits and backgrounds. Gameplay involves navigating the school, avoiding and sealing the Seven Mysteries, and learning from repeated deaths to develop survival strategies. The development team includes Rensuke Oshikiri, known for his work in manga, and Sohei Niikawa, a former Nippon Ichi Software contributor. An announcement trailer has been released.
AppWizard
September 15, 2026
Embark Studios has announced a "pause" on the Expeditions feature in Arc Raiders, with plans to revisit it until early 2027 due to persistent player feedback. Executive producer Aleksander Grøndal indicated that the feature may be overhauled or eliminated entirely. Expeditions serve as a prestige system where players reset their progress for unique benefits, but many have criticized the extensive grind for minimal rewards. The fifth Expedition, ending in September, will be the last until the feature is reworked or potentially scrapped. The studio aims to make significant changes based on community concerns regarding departure windows, reward structure, and accessibility. A major update, Frozen Trails, is set to launch in October.
AppWizard
September 12, 2026
A new mod for Grand Theft Auto V allows players to target and "destroy" virtual surveillance cameras, specifically 235 Flock cameras, as a commentary on real-world surveillance culture. Flock operates over 100,000 cameras nationwide, with a significant number in Los Angeles County, the inspiration for the game's setting. The mod represents only one-tenth of the actual surveillance in the area. Players can engage in digital activism through this gameplay, but the modder warns that vandalizing real Flock cameras is illegal and offers no rewards. The mod is available for download on GitHub.
Winsage
September 10, 2026
Microsoft's Patch Tuesday on September 8, 2026, addressed two critical Windows privilege escalation vulnerabilities: CVE-2026-85880 and CVE-2026-81963, both with a CVSS score of 7.8. CVE-2026-85880 is a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC), allowing attackers with low-privilege local access to escalate privileges to SYSTEM. CVE-2026-81963 involves improper link resolution in the Windows Update Stack, enabling similar privilege escalation. Both vulnerabilities require no user interaction and have been actively exploited prior to the patch release. CISA added them to its Known Exploited Vulnerabilities catalog on September 8, 2026, with a remediation deadline of September 22 for U.S. federal agencies. CVE-2026-85880 affects various Windows 10 and Server versions but excludes Windows 11 and Windows Server 2025. CVE-2026-81963 impacts newer Windows platforms, including Windows 11 and Windows Server 2025. Microsoft released security updates for both vulnerabilities on September 8, 2026, and organizations are advised to prioritize these updates. Security teams should monitor for signs of privilege escalation and unusual SYSTEM-level activities related to these vulnerabilities.
Search