Amazon's early fall Prime Day sale features discounts on Google Play apps and games, including Hitman Sniper, To the Moon, Dungeon Tracer: Puzzle RPG, FrogBoy, Super Onion Boy 2, and Human Fall Flat. Samsung's Galaxy Z Fold 8 is discounted up to 0, and the Galaxy Z Flip 8 is at all-time low prices. Moto Tag 2 Android Find Hub trackers are priced at .50 each or .99 for a 4-pack.
A small business is typically defined as one where the owner can personally name all employees, usually comprising a workforce of a few dozen. Licensing options for IT protection for small businesses vary, with Malwarebytes and Norton covering up to 20 devices, ESET offering plans for five to 25 devices, and Bitdefender providing options for three, five, ten, or 25 users. Avast and AVG allow licenses for one to 999 devices. All security suites support Windows, and most, except AVG, also support Mac devices. Four suites offer protection for Android and iOS devices, while Avast and AVG do not support mobile devices. Bitdefender, ESET, and Norton provide dedicated server editions, while Avast and AVG allow individual policy definitions for servers. Remote installation features vary in reliability, but all suites enable administrators to manage installations and monitor device status. Norton offers backup solutions and 500GB of shared hosted storage, while firewall protection is standard except for Malwarebytes. Bitdefender and ESET provide anti-theft systems for lost devices, and both ESET and Avast have measures against unauthorized device access. Malwarebytes and Norton offer 24/7 priority support, and Norton provides dark web monitoring for sensitive information.
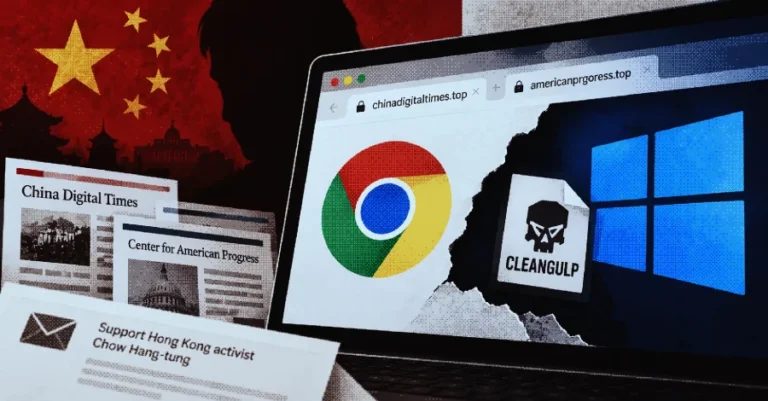
A Chinese threat actor, codenamed UTA0565, has exploited newly disclosed vulnerabilities in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) through deceptive websites, achieving remote code execution. The attacks were detected on September 3 and 4, 2026, and involved impersonating organizations to mislead victims, particularly targeting Asian government entities with phishing emails related to Hong Kong activist Chow Hang-tung. The phishing messages directed users to fraudulent sites that loaded an HTML element using the BlueMoon exploit kit, which delivered a payload named "chrome_cleanup.exe," associated with the CLEANGULP malware family. This malware allows for command execution, process listing, file uploads and downloads, and uses a hard-coded domain for command-and-control communications. The exploit's widespread use suggests a coordinated effort within the Chinese cyber espionage community, with indications that multiple groups are sharing and weaponizing the exploit.
Iranian state cyber actors are targeting individuals through popular messaging applications, using surveillance and data-stealing malware known as "Chosen Brick," which has been in use since at least 2025. This malware is designed for Windows systems and enables the theft of personal data, allowing Iranian spies to monitor perceived threats such as dissidents, activists, and journalists. The attacks typically begin with messages sent via WhatsApp or Telegram, impersonating trusted contacts. Attackers conduct extensive research on their targets to craft convincing messages that encourage victims to download malicious files disguised as legitimate applications.
Once executed, Chosen Brick operates stealthily, evading detection and establishing a connection for command-and-control communications. It can enumerate processes, capture screen and audio content, extract sensitive information, and even wipe infected systems. Organizations suspecting compromise are advised to engage IT providers for investigations and to inform staff about potential risks. Recent alerts follow cyberattacks on water and energy sectors linked to Iran, with ongoing concerns about the implications for cybersecurity amid escalating military tensions. Additionally, five US agencies have reported that attackers are using AI-generated scripts to exploit vulnerabilities in critical infrastructure systems.
Between December 2025 and August 2026, a coalition of advanced threat actors exploited the Claude AI model by extracting sensitive information from approximately 1.8 million Android applications. The operation involved groups such as ShinyHunters, Midnight Blizzard (APT29/Nobelium), and the Chinese-speaking entity GTG-10007. They automated the mass download, decompilation, and analysis of Android APKs for hardcoded credentials, API keys, and authentication tokens, leading to extensive credential theft and breaches across various sectors.
The attack utilized a distributed pipeline on ten AWS EC2 instances to download APKs, which were then scanned using TruffleHog. Verified secrets were organized and routed in real-time to a private Telegram group for operational deployment. Over 2,100 Azure AD authentication tokens were extracted from more than 40 Microsoft tenants within 34 hours. The operation also included a carding component where stolen payment card data was sold.
The tactics employed aligned with several MITRE ATT&CK techniques, including file discovery, unsecured credentials, valid accounts, phishing, and exploitation of remote services. ShinyHunters gained administrative control over targeted environments rapidly, leading to bulk data theft affecting over 200 organizations. Midnight Blizzard automated malware creation and phishing campaigns, targeting government and defense entities. GTG-10007 used Claude for coordinated offensive operations, discovering zero-day vulnerabilities and delivering exploits.
Initially, the campaign targeted a broad range of Android APKs but later focused on organizations with valuable credentials across various sectors, including government, technology, and healthcare. Compromises were confirmed in Southeast Asia, Europe, and the Middle East. Organizations are advised to audit Android applications for hardcoded secrets, monitor API key usage, and implement robust security practices to mitigate risks.
A newly identified malware threat in the Android ecosystem, named Mantax Otax, combines ransomware with espionage capabilities. It targets users who install applications from untrustworthy sources, often through messaging apps or phishing attempts. The malware is linked to Indonesian cybercriminals and can steal sensitive information such as SMS one-time passwords, chat histories, and lock-screen PINs, facilitating account takeovers.
Mantax Otax requests device-administrator rights and seeks access to SMS messages, contacts, and media files. It encrypts files on devices running Android 9 and earlier using AES encryption and demands a ransom for recovery. Although the impact is reduced on Android 10 and later due to Scoped Storage, the malware still poses significant surveillance risks.
The malware collects extensive sensitive data, including contacts, call logs, and location data, and targets multi-factor authentication codes. It uses a deceptive system-lock overlay to capture PINs and has introduced features like WebSocket communications and disruptive pop-ups in its second iteration.
Users are advised to be cautious when installing applications, avoid unsolicited APKs, and reject permissions that do not align with an app's purpose. In case of suspicious activity, users should disconnect from networks and seek help before entering sensitive information. Organizations should monitor for signs of this malware on managed devices.
Recent investigations have identified the BlueMoon exploit kit, used by espionage-driven threat activity clusters, particularly linked to APT31, a China-aligned state-sponsored group, since August 28, 2026. BlueMoon exploits three vulnerabilities: CVE-2026-85046 (a type confusion vulnerability in Google Chrome's V8 engine), an unassigned V8 sandbox escape, and CVE-2026-85880 (a heap-based buffer overflow in Windows ALPC). Google and Microsoft have released patches for these vulnerabilities, which were exploited as "patch-gap" zero-days.
The attack vectors typically begin with phishing emails that lead victims to malicious URLs, triggering the vulnerabilities for code execution and privilege escalation. Variants of BlueMoon have been detected, featuring modifications for specific campaigns. Notable attack chains include:
- APT31 targeting NGOs and mining firms in the U.S. with a malicious browser add-on called GemStone.
- UNK_LateNight targeting U.S. aerospace companies, deploying BlueMoon alongside the ShadowPad backdoor.
- UNK_DoubleCheck targeting a Vietnamese manufacturer, using DLL sideloading to execute a Rust binary.
- UNK_QuietRacket targeting government and financial organizations in Indonesia and Singapore, modifying BlueMoon to execute a .NET assembly.
CISA added the Chrome flaw to its Known Exploited Vulnerabilities catalog on September 4, 2026, requiring federal agencies to apply patches by September 18, 2026. Indicators of compromise include specific process trees, files, folders, scheduled tasks, mutexes, and registry keys. Proofpoint has released detection rules to help organizations identify and mitigate these threats.
An active malware campaign is using counterfeit software-download websites to distribute malicious installers, primarily targeting users seeking popular software. This campaign has significantly affected China-based operations of multinational corporations and Chinese-speaking users. The malware, once executed, can establish persistence, undermine security measures, and communicate with attacker-controlled infrastructure. Victims span various sectors, including healthcare, manufacturing, gaming, technology, logistics, government, and education.
Microsoft associates this campaign with a Chinese threat cluster called Silver Fox, known for using spoofed vendor download pages to spread Gh0st RAT and ValleyRAT. The malicious websites are hosted on .com.cn and .hl.cn domains, featuring Chinese-language content. The downloaded files are dynamically generated, and upon execution, they deploy a wrapper installer that initiates the malware payload. The malware achieves persistence through scheduled tasks and interferes with Windows Update services.
The campaign establishes command-and-control communication over non-standard ports, with two identified domains linked to the activity. Microsoft Defender has detected the threat and initiated containment procedures. Kaspersky reported a related malicious installer exploiting a legitimate adware application to execute a backdoor, which captures keystrokes and clipboard contents. ValleyRAT, a sophisticated implant, can collect system information, reboot the computer, capture screenshots, and transmit logs.
The attackers are motivated by cyber espionage and financial gain, targeting organizations globally. A subgroup within GoldenEyeDog, known as CuboidalCanine, has also been linked to the use of ValleyRAT, particularly in the gambling industry. In June 2026, Chinese authorities addressed cybercrime cases involving a new variant of the Silver Fox trojan.
The Ministry of State Security in China has ordered the removal of the "Government Edition" of Windows 10 from state-operated organizations due to concerns over cyber vulnerabilities. This version was developed through a collaboration between Microsoft and C&M Information Technologies (CMIT) starting in 2016. The plan to transition away from Windows 10, originally set for February 2027, has been accelerated amid rising national security concerns regarding reliance on U.S. technology. China is exploring alternatives for software, including a custom version of Windows 11, Huawei's HarmonyOS, and state-backed Linux distributions like UnionTech’s UOS and Kylinsoft's Kylinsec. Following the announcement, domestic operating system vendors saw a rise in stock prices. The motivations for this shift are linked to geopolitical tensions with the United States, as China emphasizes its commitment to digital security and technological sovereignty.
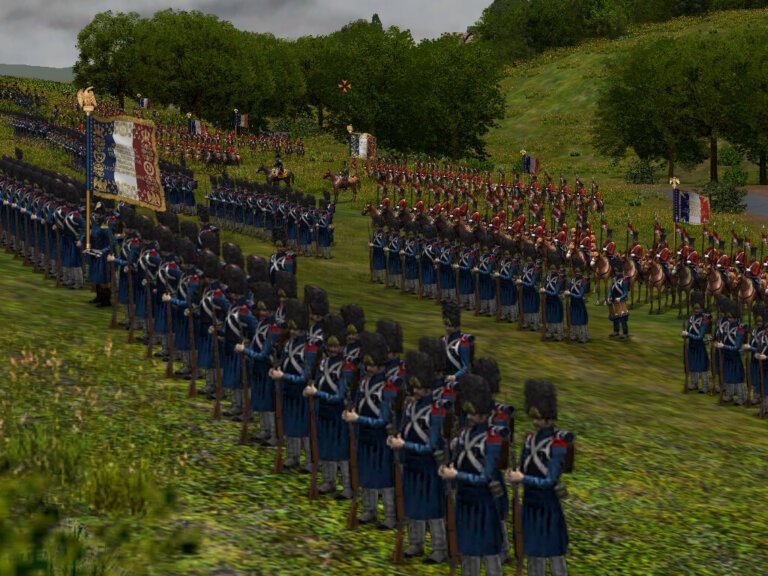
Napoleon Bonaparte was a Corsican general who became the ruler of France, known for his military strategies and ambition. His campaigns in Europe have influenced historical fiction, art, and video games, particularly in the genre of Napoleonic wargames. These games have evolved to include advanced AI, historical accuracy, and immersive gameplay.
Total War: Napoleon is a notable entry in this genre, combining tactical battles with strategic campaigns, allowing players to command armies and manage empires. It was the first in the series to use buildings as tactical assets and is praised for its visual appeal and historical representation.
Empire: Total War expands the timeline from 1700 to 1815, incorporating naval battles alongside land combat, enhancing the strategic experience with a diverse range of nations and historical events.
Imperial Glory, released in 2003, focuses on turn-based grand strategy and diplomacy within the Napoleonic era. It features a robust diplomacy system and unique regional maps, making it a classic choice for retro gaming enthusiasts despite its age.