executable files

Winsage
October 15, 2026
Microsoft has identified 1,416 vulnerabilities in its systems, with 85 classified as “critical.” Among these, 67 are categorized as remote code execution (RCE) vulnerabilities. One vulnerability is actively exploited, and two have been publicly disclosed. The upcoming Patch Tuesday is on November 10th, 2026, and users are advised to upgrade to Windows 11 25H2 or 26H2. A specific vulnerability, CVE-2026-96951, allows attackers to bypass system defenses by masking the origin of executable files. Microsoft has flagged 42 critical vulnerabilities, including 30 RCE vulnerabilities, which can allow attackers to execute malicious code remotely.
Winsage
October 14, 2026
Microsoft has identified 1,416 vulnerabilities within its systems, with 85 classified as "critical." Among these, 67 are remote code execution (RCE) vulnerabilities. One vulnerability is actively exploited, and two others were disclosed prior to the assessment. The next opportunity for users to address these vulnerabilities will be on November 10th, 2026, during Patch Tuesday. Users are encouraged to upgrade to Windows 11 versions 25H2 or 26H2. A specific vulnerability, CVE-2026-96951, allows attackers to bypass system defenses by masking executable file origins. Of the critical vulnerabilities, 30 are RCE vulnerabilities that enable remote execution of malicious code without authentication or user interaction.
AppWizard
October 9, 2026
The AnyPS5 project has achieved 100% implementation of graphics shader instructions, allowing for the direct porting and cross-linking of PlayStation 5 executable files to Windows and Linux without traditional emulation. The project has translated proprietary calls to the PS5's graphics chip into the SPIR-V format for rendering through the Vulkan API. While the complete instruction set coverage indicates successful implementation, it does not guarantee flawless operation in all scenarios. The project has demonstrated stable performance, running a 2D platformer at 60 frames per second on an Intel Core i5 processor and NVIDIA GeForce GTX 1050 Ti graphics card. The developers plan to implement key system libraries for the PRX format soon, leveraging architectural similarities between the PS5 and modern PCs. Additionally, advancements may support related initiatives like the kytyps5 translation layer for console games on PCs.
TrendTechie
August 19, 2026
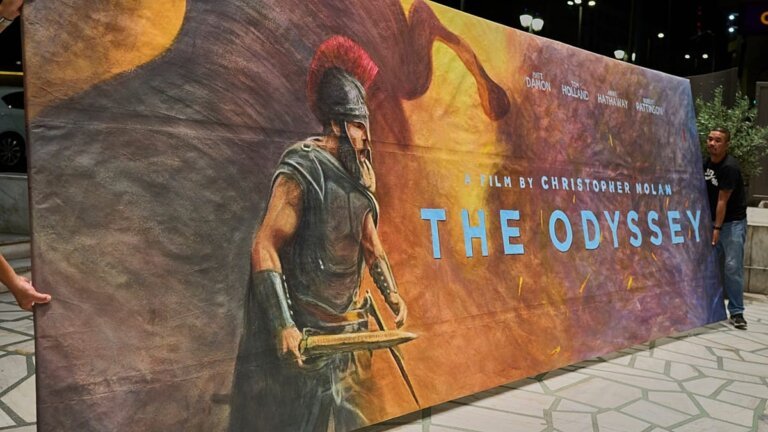
Pirated digital copies of the film "Odyssey" are being used to spread the Lumma Stealer malware, which compromises viewers' computers. Bitdefender's internal data shows that users have attempted to download malicious executable files disguised as the film, which has not yet been released on online platforms. These counterfeit copies are circulating on illegal sites, and the Lumma Stealer malware can steal sensitive information from infected devices. Bitdefender identified several bait file names that are actually executable files designed to infect computers rather than play the film. This tactic follows a trend of using popular films to disseminate malware, with similar campaigns documented in the past. Cybercriminals exploit the gap between a film's theatrical release and its availability on legal streaming platforms. Users are advised to watch films only through verified services and to keep their cybersecurity software updated.
Tech Optimizer
July 15, 2026
The Russian portal "Multiscanner" has resumed its service for scanning files for malicious software without mandatory registration. It allows users to upload files up to 256 MB in over 30 formats, including DOC, DOCX, PDF, PPTX, EXE, and ZIP. The scanning history is saved in the browser but can be deleted for privacy. "Multiscanner" is compatible with popular web browsers like Google Chrome, Yandex Browser, Firefox, Microsoft Edge, and Safari, but is not available on mobile browsers. The portal was originally developed between 2023 and 2024 and is now managed by the National Technology Center for Digital Cryptography, operating in pilot mode.
Winsage
June 8, 2026
Microsoft has integrated Sysmon into Windows 11 through a system update, allowing it to operate in the background and log activities in the Windows Event Log. Indicators of suspicious processes include the absence of icons or descriptions, incorrect parent processes, spelling errors in names, unsigned executable files, packed executables, suspicious DLLs or services, open TCP/IP endpoints, and unusual URLs or character strings. To install Sysmon, users must access the Control Panel, enable Sysmon, and restart their PC. Activation requires running a command in the Command Prompt. Sysmon logs can be viewed in the Event Viewer under Microsoft > Windows > Sysmon > Operational. Users can filter events using an XML configuration file. After analysis, suspicious processes should be scanned with antivirus software, and files can be uploaded to VirusTotal for further examination. Sysmon continuously logs events, while Process Monitor captures snapshots of running processes, and both tools are available for free from Microsoft.
Winsage
June 4, 2026
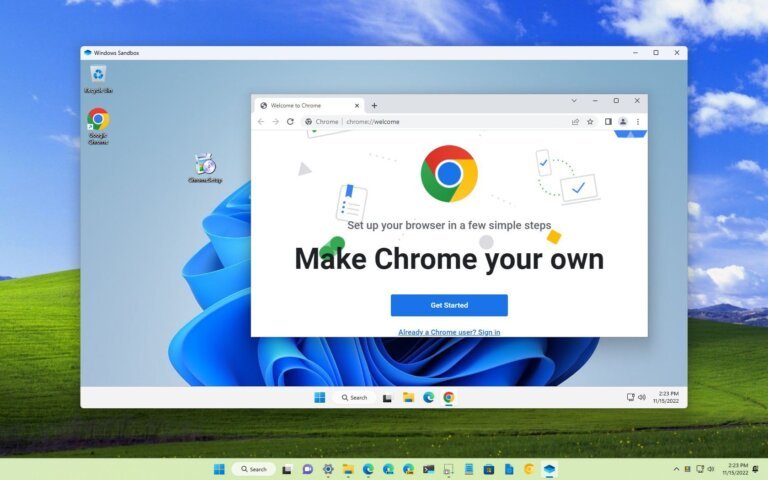
Windows 11 features Smart App Control to block untrusted applications and includes Windows Sandbox, a lightweight virtual machine that provides an isolated desktop environment for safely executing applications. Windows Sandbox uses container technology and hypervisor-based virtualization to mitigate risks associated with untrusted software. It ensures that each session starts fresh, with no data persisting after closing, and applications installed on the host system are not accessible within the Sandbox. Starting with Windows 11 version 22H2, data can persist through restarts initiated within the Sandbox. Windows Sandbox is included in supported Windows editions such as Pro, Enterprise, and Education, and offers quick launch times, a lower memory footprint, and a secure environment for testing untrusted software. Setting up Windows Sandbox involves searching for it in the Start menu, running it as an administrator, and transferring executable files for installation within the Sandbox.
Search