exploitation

Winsage
October 14, 2026
Microsoft's October 2026 Patch Tuesday updates addressed 1,413 vulnerabilities, including 1,102 in Windows, 134 in Office applications, 61 in developer tools, and 36 related to SharePoint Server. This total surpasses the vulnerabilities fixed by Microsoft in all of 2025, with over 4,000 vulnerabilities resolved in 2026. A critical zero-day vulnerability, CVE-2026-96951, with a CVSS score of 8.8, was also patched; it allows attackers to bypass Windows shell security features. The Cybersecurity and Infrastructure Security Agency (CISA) has included this vulnerability in its Known Exploited Vulnerabilities catalog. Additionally, two publicly disclosed vulnerabilities were patched, and Microsoft introduced 'risk cohorts' to help manage security updates.
Winsage
October 14, 2026
Microsoft released its October 2026 Patch Tuesday updates for Windows 11, addressing 1,413 vulnerabilities, including a critical fix for an exploited Windows Shell vulnerability (CVE-2026-96951) that bypasses Mark of the Web defenses. This update is the last monthly security update for Windows 11 24H2 Home and Pro users, who must upgrade to a supported version for future security fixes. The update packages KB5127648 and KB5127646 cover versions 24H2, 25H2, and 26H2, and also include fixes for reliability issues such as Explorer.exe startup failures, VPN connection problems, and gaming mouse stuttering. Additionally, the update resolves issues with AC-3 playback, printing failures, and fingerprint sign-in failures after a cold boot. Users are advised to install the updates promptly and restart their systems to complete the process.
Winsage
October 14, 2026
Microsoft's October 2026 security updates address 1,411 vulnerabilities, marking the largest Patch Tuesday release to date. The update includes 70 vulnerabilities classified as Critical, with 57 related to remote code execution, 11 to elevation of privilege, and two to spoofing. Key vulnerabilities include CVE-2026-96951, a Windows Shell security bypass being actively exploited, CVE-2026-108398, which affects .NET Framework and allows bypassing Windows Defender Application Control, and CVE-2026-92707, a denial-of-service vulnerability in MessagePack-CSharp. The release coincides with critical Windows support deadlines, with the final regular update for Windows 11 24H2 Home and Pro and Windows 10 Enterprise LTSB 2016 occurring on October 13. Organizations are advised to prioritize the exploited vulnerabilities, ensure relevant updates are applied, and validate application-control behavior.
AppWizard
October 6, 2026
On October 6, Google faced a legal challenge for allegedly imposing excessive charges on Android app developers for over a decade, inflating prices on the Play Store and affecting approximately 20 million customers in the UK. The case, initiated at the Competition Appeal Tribunal in London, claims Google's 30% commission on digital purchases violates competition law, with potential payouts of £1.2 billion for consumers affected since 2015. Lawyers argue that Google has exploited its market dominance to impose unfair prices, while Google denies any anti-competitive behavior. The scrutiny of app stores has increased globally, with both Google and Apple facing regulatory challenges, including fines imposed on Apple by the EU and a €430 million fine on Google for restricting app developers. The current case follows a ruling that Apple abused its dominant position, indicating potential changes in app store regulations.
AppWizard
October 4, 2026
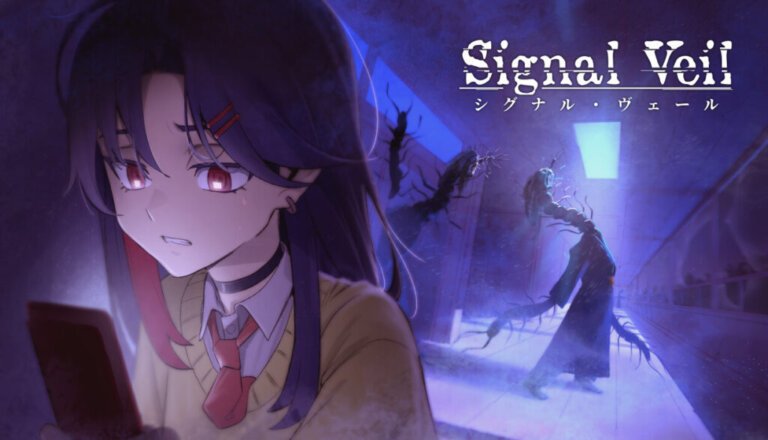
A new psychological survival horror game titled Signal Veil is being developed by the Chilean studio Time Hunters in collaboration with Tokyo-based publisher Serafini Productions. It will be available on Nintendo Switch 2, PS5, Xbox Series X|S, and PC via Steam and the Epic Games Store. The game features a ’90s anime aesthetic and follows Aki Mizuno, a teenage girl searching for her missing mother at Nishikawa High School. Aki inherits a supernatural cellphone that helps her detect spirits and interact with the environment. The gameplay includes fixed camera angles reminiscent of classic survival horror games, strategic combat with limited resources, and ritual-like enemy encounters. An official release date has not been announced, but players can add it to their digital wishlists.
Tech Optimizer
September 28, 2026
Two newly identified Critical CVEs have expanded Microsoft's September identity infrastructure vulnerabilities to over ten verified weaknesses across more than ten distinct services. The Azure Database for PostgreSQL is vulnerable to CVE-2026-85878, an Improper Authorization flaw (CWE-285) with a CVSS score of 9.9. Azure Billing is impacted by CVE-2026-62874, which presents an Insufficient Data Authenticity Verification issue (CWE-345) with a CVSS score of 10.0. Both vulnerabilities were disclosed on September 18 and validated by Tenable and MITRE. CVE-2026-85878 allows an authorized attacker to elevate privileges over the network with minimal complexity, while CVE-2026-62874 requires no authentication, enabling unauthenticated attackers to jeopardize financial integrity. The vulnerability cluster first emerged during the Patch Tuesday cycles on September 3 and September 8, with initial reports highlighting critical flaws in core services. Other September disclosures include CVE-2026-83711 (Azure AD B2C, CVSS 10.0), CVE-2026-70352 (Azure AI Language, CVSS 10.0), CVE-2026-83941 (Entra ID, CVSS 9.9), CVE-2026-62916 (Entra ID, CVSS 9.1), CVE-2026-69857 (Azure Cosmos DB, CVSS 8.5), and CVE-2026-69854 (Spring Cloud Azure, CVSS 9.0). Activity heightened between September 17 and 18 with the introduction of CVE-2026-77903 (Microsoft Dataverse, CVSS 9.0) and CVE-2026-69843 (Microsoft Fabric, CVSS 10.0). The attack surface has broadened from authentication concerns to encompass trust in AI endpoints, data storage locations, and billing verification processes. Seven out of the ten vulnerabilities are unauthenticated, and all issues were addressed through server-side fixes by Microsoft. The extensive range of affected services suggests these vulnerabilities indicate a shared architectural dependency on authentication logic.
Winsage
September 24, 2026
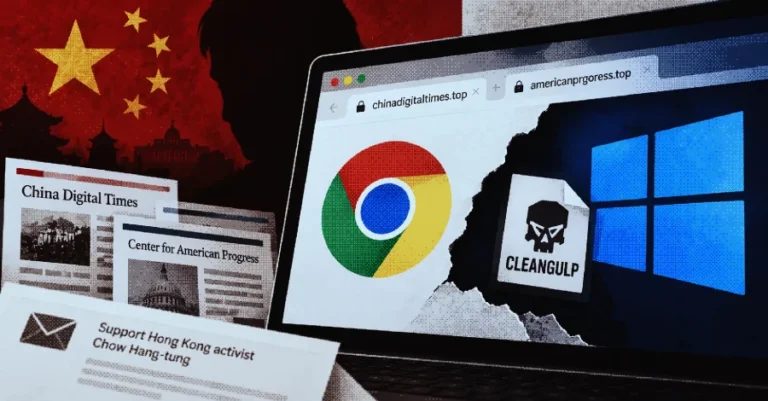
A Chinese threat actor, codenamed UTA0565, has exploited newly disclosed vulnerabilities in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) through deceptive websites, achieving remote code execution. The attacks were detected on September 3 and 4, 2026, and involved impersonating organizations to mislead victims, particularly targeting Asian government entities with phishing emails related to Hong Kong activist Chow Hang-tung. The phishing messages directed users to fraudulent sites that loaded an HTML element using the BlueMoon exploit kit, which delivered a payload named "chrome_cleanup.exe," associated with the CLEANGULP malware family. This malware allows for command execution, process listing, file uploads and downloads, and uses a hard-coded domain for command-and-control communications. The exploit's widespread use suggests a coordinated effort within the Chinese cyber espionage community, with indications that multiple groups are sharing and weaponizing the exploit.
Tech Optimizer
September 23, 2026
A new tool named BigDiskBuster has been released on GitHub, which disrupts Microsoft Defender Antivirus by preventing it from installing updates. It does this by consuming available disk space during the update process, causing Defender to remain on its current version and unable to receive new platform or signature updates. BigDiskBuster operates as a local denial-of-service technique and requires prior access to the target machine to execute. The tool was created by researcher Abdelhamid Naceri, known as Nightmare Eclipse, who has previously worked on similar projects. As of now, there is no CVE identifier, patch, or advisory from Microsoft regarding this issue.
Search