hypervisor

AppWizard
September 28, 2026
Irdeto's Denuvo has reached a milestone with the disbandment of DenuvOwO, a group that created a hypervisor-based bypass for Denuvo. This decision may be linked to Irdeto's legal action against a cracker known as Voices38. The CS.Rin forum has removed links to games using the DenuvOwO bypass and banned associated members to avoid legal issues. A proof-of-concept crack for Assassin's Creed: Mirage has been developed, removing Denuvo Anti-Tamper and VMProtect, resulting in a 15% increase in average frames per second (FPS) and a 76% improvement in minimum frame rates on a high-end setup.
Tech Optimizer
September 11, 2026
Lakebase Postgres employs a disaggregated storage model that enhances data management through efficient caching, utilizing an object store like S3 for backups. The caching operates on two layers: within distributed storage for optimizing write and read performance, and on the Postgres compute side for ultra-fast access to frequently accessed pages. Traditional Postgres caching involves shared buffers and the OS page cache, which leads to double buffering and inefficiencies. Lakebase Postgres addresses these issues by implementing a local file cache (LFC) and larger shared buffers, allowing for more effective memory utilization without the drawbacks of the OS page cache. The shared buffers are set to a maximum of 1 GB, while the LFC can utilize up to 75% of DRAM. The introduction of huge pages reduces memory management overhead and improves performance, resulting in significant throughput increases and reduced latency in production environments. Recent enhancements have shown up to 2× throughput improvements and substantial reductions in CPU usage. The focus is now on extending these benefits to autoscaling Postgres computes, with plans to implement dynamic shared buffers and autoscaling huge pages.
BetaBeacon
September 9, 2026
Android Studio Emulator is the official Android SDK tooling maintained by Google for app developers to test code against specific Android API levels, screen densities, and hardware profiles.
Winsage
September 5, 2026
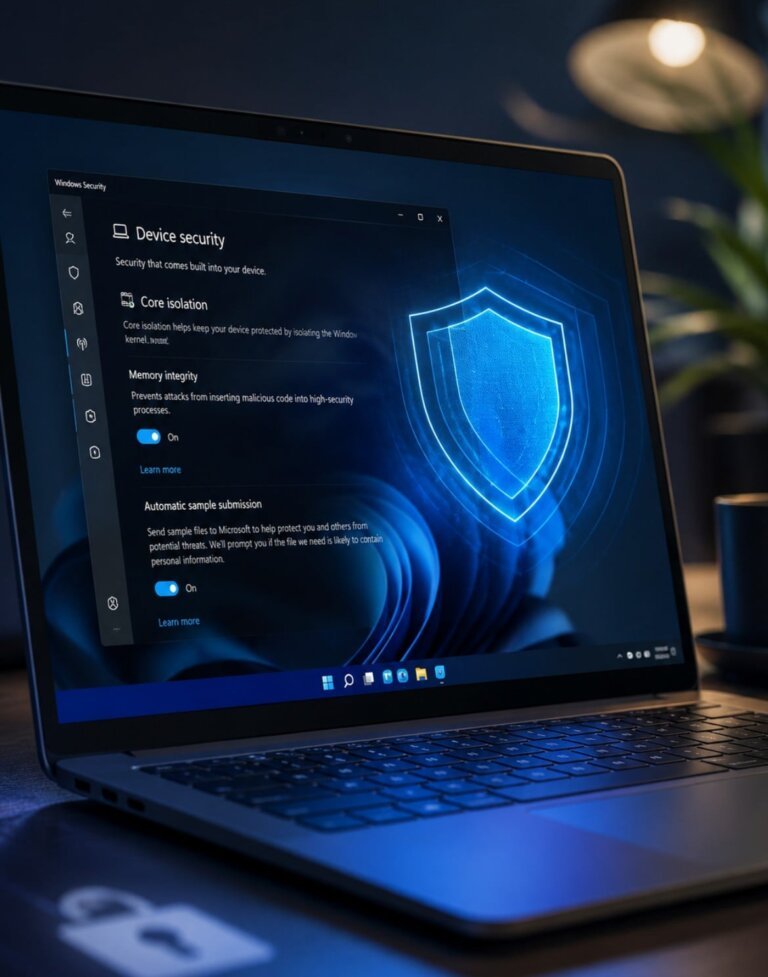
Memory Integrity enhances Windows 11 security by allowing only verified kernel-mode code to load, blocking unsigned rootkits and improving defenses against driver-based kernel attacks. It requires specific hardware for optimal functionality. The combination of Hypervisor-Protected Code Integrity (HVCI) and Virtualization-Based Security (VBS) may result in a performance decrease in gaming, with reported slowdowns of up to 15 percent. Microsoft acknowledged in 2022 that these features might impact gaming performance and advised gamers to consider temporarily disabling them for better performance, especially on older hardware. Tom’s Hardware reiterated this recommendation to balance security and user experience.
Winsage
September 3, 2026
Microsoft plans to automatically activate Memory Integrity on a broader range of eligible systems starting October 2026, rolling it out through standard Windows quality updates. Prior to activation, Windows will assess hardware, drivers, and performance to ensure compatibility. Memory Integrity, part of Virtualization-based Security (VBS), uses the Windows hypervisor to create a secure environment for integrity checks on kernel code. Compatibility with drivers is crucial, as many older applications may not meet the stricter standards required for HVCI. Potential compatibility issues may arise with anti-cheat solutions, third-party input methods, and banking protection programs, which could lead to software malfunctions or boot failures. A readiness check will evaluate hardware compatibility, with eligible systems including Intel processors from the 8th generation, AMD processors from Zen 2, and Qualcomm Snapdragon 8180 or newer, along with specific RAM and storage requirements. The rollout will be gradual, and users who previously disabled HVCI will not face unexpected reactivation. Microsoft recommends updating affected applications or drivers in case of compatibility issues.
Winsage
September 2, 2026
Microsoft will automatically enable its Memory Integrity feature on more eligible Windows PCs starting in October 2026, enhancing kernel-level protection. PCs with Memory Integrity currently disabled will retain their settings. Windows will also activate Virtualization-based Security (VBS) where necessary, which supports Memory Integrity. An automatic assessment will determine device eligibility based on hardware capabilities and compatibility. The rollout applies to Windows 11 installations meeting specific hardware specifications, including an 8th Generation or newer Intel processor or AMD Zen 2 or newer processor, at least 8GB of RAM, an SSD with a minimum of 64GB, compatible drivers, and enabled hardware virtualization. Memory Integrity, also known as Hypervisor-Protected Code Integrity (HVCI), has been part of Windows since the Windows 10 era and is now more integral to Windows 11 security for new installations. However, it may impact gaming performance, leading some gamers to disable it, which Microsoft has acknowledged in its recommendations.
Winsage
August 14, 2026
Researchers from the University of Birmingham and Durham University discovered a vulnerability in consumer DDR4 and DDR5 memory chips, termed "Download more RAM," which allows attackers to misreport memory configuration, potentially doubling the perceived RAM. This manipulation enables unauthorized access to memory allocations, bypassing Windows' Virtualization-based Security (VBS) and Hypervisor-Enforced Code Integrity (HVCI), and disabling antivirus software. The vulnerability affects major manufacturers like Corsair, G.Skill, and ADATA, which collectively hold over 55% of the high-performance memory market. Microsoft has patched the vulnerability, cataloged as CVE-2026-23670, with a medium severity score of 5.7/10, in the April 2026 Patch Tuesday update. Corsair has introduced a feature to enable write protection on their memory modules, and other tools are available for additional protection.
Search