India

AppWizard
September 10, 2026
SUNSOFT will release "SUNSOFT is Back! Retro Game Selection 2" on December 17 for PlayStation 5, Switch, and PC (Steam). Physical editions will be available in Japan for PlayStation 5 and Switch, including a special Collector’s Box. The collection features newly integrated save and rewind features and a Gallery Mode showcasing rare materials from the original games. Included titles are: - Super Arabian: An action-adventure game from 1985 where players rescue a kidnapped princess. - Ikki: A quirky action game where players collect gold coins and rice balls while rebelling against taxes. - The Mystery of Atlantis: A high-difficulty action game with 100 stages set on the island of Atlantis. - Maharaja: An adventure RPG from 1989 involving a mysterious wooden box in India.
Winsage
September 5, 2026
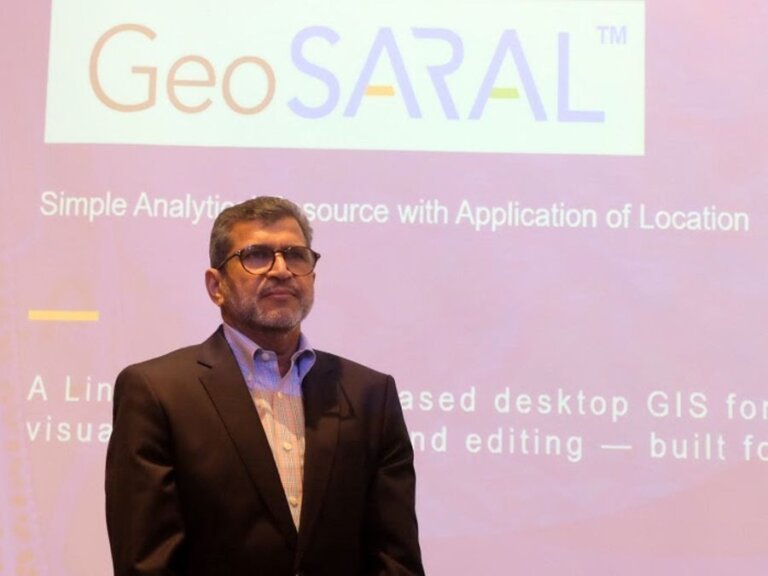
Esri India has launched GeoSARAL, a Linux-based desktop GIS software designed for users who need a straightforward solution for mapping, visualization, querying, and editing. GeoSARAL will also be available on Windows and plans for Android support are forthcoming. It integrates with existing ArcGIS infrastructures and allows users to access GIS data and basemaps locally, even without an internet connection. The software aims to meet the demands of Esri India's user community across enterprise and government sectors, enhancing domestic technology capabilities and promoting technological self-reliance in India.
AppWizard
August 31, 2026
Google will implement new memory usage regulations for Android applications starting in February 2027, due to a global RAM shortage. Apps exceeding the set memory limits may be throttled, terminated, or face reduced visibility on the Play Store. The memory thresholds vary based on device specifications, with specific limits for foreground, background, and bitmap memory usage. Non-compliance will result in penalties affecting app distribution and visibility. The memory crisis is attributed to increased demand from the AI data center industry, leading to rising RAM costs. The new limits will first apply to Pixel devices with Android 17, and other manufacturers are expected to follow. Additionally, by April 2027, all apps on the Play Store must support zero-tap credential restoration for users transitioning to new devices.
Tech Optimizer
August 31, 2026
Silver Fox is linked to the distribution of a backdoor malware called ValleyRAT, disguised as the legitimate QN Wallpaper adware application. Once installed, ValleyRAT provides complete control over the compromised machine. The malware uses DLL sideloading to operate under the guise of a legitimate process, bypassing security measures. It disables Windows Defender and adds itself to autorun entries, and can mark its process as critical, causing system crashes if terminated. Kaspersky has identified specific indicators of compromise (IoCs) including hashes, command-and-control servers, and associated domains. In 2026, Kaspersky recorded over 100,000 detections of ValleyRAT affecting more than 1,500 unique users, mainly in China and India.
AppWizard
August 31, 2026
India's cybercrime authorities have warned about the misuse of dating and adult-themed advertisements on social media platforms like Instagram and Facebook, which are being exploited by criminals to distribute malicious Android applications. These ads redirect users to external websites where they are prompted to download APK files, bypassing security measures of trusted app stores. The Indian Cybercrime Coordination Centre (I4C) has identified several malicious applications, including Night Play, Reloop, Kyss, Vimo, Rivo, Nexo, and Vixa, and cautions against installing unfamiliar applications promoted through unsolicited ads. These apps may request sensitive permissions, such as access to SMS messages, contacts, photos, device storage, and Accessibility Services, which can allow fraudsters to access valuable information. Compromised devices can lead to financial fraud by intercepting OTPs and other verification details. The I4C recommends using trusted app stores, keeping Google Play Protect active, reviewing app permissions, and being cautious with social media ads. If a suspicious app is installed, users should restart their phone in Safe Mode to uninstall it, disable its permissions if necessary, and consider a factory reset if removal fails. Users who suspect fraud are encouraged to report incidents promptly.
AppWizard
August 30, 2026
Security agencies in India have observed a shift in the tactics of terrorist groups, which are now using pornography websites and niche encrypted applications for communication instead of traditional social media. These groups, often collaborating with Pakistan's ISI, utilize platforms with real-time chat tools disguised as dating services to send instructions to recruits in Jammu and Kashmir. Security agencies are monitoring various digital tools, including Tor-based applications like Coatex and Conion, which obscure user identities. Some privacy-focused platforms do not require phone numbers for registration, complicating tracking efforts. Despite bans on certain pornography applications in India, they are still accessed illegally via VPNs, which mask users' IP addresses. The use of the Tor network presents additional tracking challenges, as it obscures data origins and destinations. Security agencies are adapting their surveillance methods in response to these developments, which include the use of virtual SIM cards in terrorist activities, as highlighted during investigations into the 2019 Pulwama attack.
AppWizard
August 26, 2026
The Google Play Store is the primary destination for Android applications, but many users seek alternative app stores for greater variety, different versions, or region-specific apps. In India, the search for alternative app stores is common due to the diverse needs of users. While the Play Store offers a wide selection of apps and automatic updates, alternative app stores may provide older versions, modded APKs, or apps not available in certain regions. Popular alternative app stores include HappyMod, APKPure, Aptoide, and Uptodown. Users should verify the developer, check reviews, be cautious about permissions, ensure compatibility, avoid unofficial sources, and keep their system updated before installing apps from these platforms.
Winsage
August 17, 2026
A suspected advanced persistent threat (APT) group linked to China exploited a newly patched vulnerability in VMware vCenter (CVE-2026-59310), which has a critical CVSS score of 9.8, allowing for arbitrary code execution and the deployment of Babuk-derived ransomware. A recently patched vulnerability in Apple macOS (CVE-2026-65400) has been exploited to deploy a cryptocurrency miner, granting unauthorized root access. The Lazarus Group from North Korea exploited a zero-day vulnerability in Microsoft Windows, targeting defense and aerospace sectors. GeoServer patched a critical SQL injection vulnerability that was actively exploited. A new macOS malware, Amnesia Stealer, targets users through ClickFix attacks, stealing data and allowing real-time access to authenticated sessions. A novel attack technique named GhostSplice can manipulate AI coding assistants. Research revealed a method exploiting Chromium's DevTools Protocol for data theft. Noteworthy CVEs this week include CVE-2026-68820, CVE-2026-58231, and multiple others across various platforms. A high-severity command injection flaw in FileRun allows remote code execution. An advanced ClickFix attack has been reported, deploying sophisticated malware. A heap overflow vulnerability in Citrix NetScaler was patched after indications of exploitation. A new malware loader targeting Portuguese-speaking users has been identified. A significant reduction in exposed Automatic Tank Gauge systems has been observed. A phishing campaign targeting Brazil has been detected, and an F.B.I. agent faces charges for unauthorized crypto withdrawals. Authorities in Ukraine dismantled fraudulent call centers, and a North Carolina man was sentenced for cyber extortion. Unauthorized access to sensitive data by the ExfilSquad group has been confirmed. LightSpy activity linked to China has been detected in over 13 countries. A supply chain attack exposed over 2,500 companies, and an Azure exfiltration campaign has exposed millions of enterprise records.
Search