investigations

AppWizard
October 11, 2026
A research team from Turkey, led by Erdal Başaran and Ömer Okucu of Ağrı İbrahim Çeçen University, along with Yusuf Alaca from Hitit University, has developed an innovative detection framework for Android malware that utilizes a visual approach. This framework transforms key features of Android applications into images, allowing a Vision Transformer to differentiate between benign software and malware. The researchers created two types of images from static and dynamic analysis features: a conventional 2D grayscale image and a QR code image. Separate Vision Transformer models were trained on each image type, and spatial pooling features were extracted from deeper layers to create a comprehensive representation of application behavior. To refine the fused feature vector, Recursive Feature Elimination (RFE) was employed, enhancing classification clarity and reducing computational load. The final classification utilized a majority-voting ensemble strategy, achieving a detection accuracy of 98.72 percent, surpassing standalone models. The study demonstrates that the multimodal system outperforms individual grayscale or QR code pathways. The dataset used is publicly available, promoting reproducibility. The framework's reliance on static and dynamic analysis features allows it to adapt to new threats, and the novel QR code representation offers distinctive visual signatures of malicious behavior. However, challenges remain regarding feature extraction quality and computational demands.
Winsage
October 8, 2026
On October 2, Microsoft announced that its optional preview update "KB5124010," released on September 22, causes crashes in applications using the Dolby Digital (AC-3) codec on Windows 11 versions 24H2, 25H2, and 26H2. The update does not include security fixes and affects media players, games, and certain line-of-business applications that rely on Windows' built-in AC-3 audio decoding. Symptoms include applications failing to launch or crashing during specific features like music playback. Users can check if they are affected by verifying their OS version, installed updates, and application implementation. Microsoft plans to address the issue in a future update, but a timeline is not provided. Users can uninstall KB5124010 or pause updates as temporary solutions. The update has already caused issues for the game "WARDOGS," leading to compatibility investigations by the publisher, Team17.
Winsage
October 3, 2026
Windows 11 uses a thumbnail caching mechanism to store previews of images in specific databases located in %LocalAppData%MicrosoftWindowsExplorer, such as thumbcache32.db and thumbcache1024.db. When a user deletes an image, the corresponding thumbnail may remain in the cache, as deletion does not automatically remove it from the thumbnail database. The cache retains only reduced versions of images, not the original files, which is significant in digital forensics where thumbnails can provide insights even when original files are missing. Users can manage their thumbnail cache using the cleanmgr tool to clear saved thumbnails or disable thumbnail caching through the Local Group Policy Editor or File Explorer settings.
AppWizard
September 29, 2026
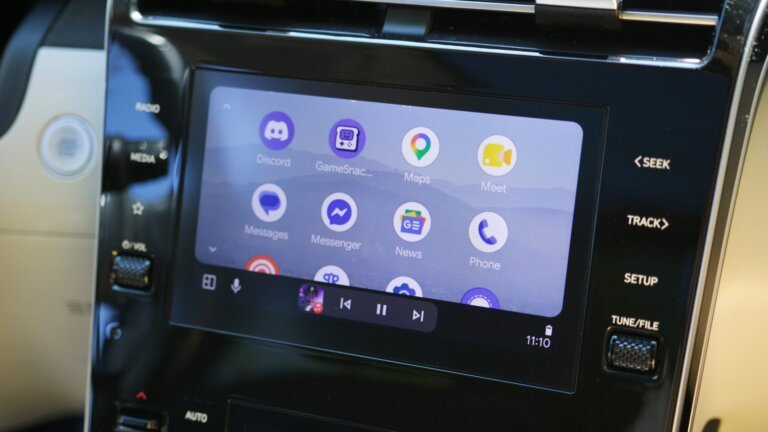
Motorola and Google are addressing an issue with Android Auto affecting users of clamshell foldable devices, specifically that outgoing calls cannot be made while the phones are closed. Incoming calls can be received without issues, but attempts to make outgoing calls result in no connection. This problem has been reported by owners of Motorola Razr and Samsung Galaxy Z Flip devices and appears to have arisen after the transition from Google Assistant to the new Gemini system. Reports of this malfunction have been ongoing for several months, with some claims dating back to September. No definitive solution has been announced yet, and users may need to keep their devices open to make calls while driving.
Tech Optimizer
September 25, 2026
Cybersecurity threats are on the rise, with Verizon’s 2026 Data Breach Investigations Report indicating that 48% of breaches involve ransomware and 31% arise from software vulnerabilities. A review of leading antivirus programs assessed their effectiveness against various threats. Top antivirus software includes: - Bitdefender: Best overall, effective against various threats, perfect score from AV-TEST. - Norton 360: Best all-in-one suite, includes VPN and parental controls, perfect score from AV-TEST. - McAfee+ Premium: Best for families, unlimited device coverage, full marks from AV-TEST. - Malwarebytes: Best for simple protection, user-friendly interface, rated 5.5/6 by AV-TEST. - ESET NOD32: Best for advanced users, lightweight and fast, includes Gamer Mode. - Avast: Best free option, offers various scanning options, straightforward upgrade path. - Microsoft Defender: Built-in for Windows, essential protection, perfect score from AV-TEST. - Intego ONE: Best for Mac users, includes firewall and VPN. - Surfshark Antivirus: Combines antivirus and VPN services, real-time protection. - TotalAV: Best for beginners, combines antivirus with web security tools. The evaluation process included lab data from AV-TEST and AV-Comparatives, hands-on experience, and criteria such as malware protection, false positives, system performance impact, phishing protection, ease of use, platform coverage, additional security features, and pricing. Key metrics from antivirus lab tests include protection scores, false positives, and performance impact. The choice between antivirus software and internet security suites depends on individual needs. Antivirus software remains necessary, especially for Windows PCs, to complement other security measures.
Winsage
September 22, 2026
Recent investigations have shown that a specific update to Microsoft Defender has caused performance issues for VLC Media Player, particularly a slowdown in startup times. Jean-Baptiste Kempf, a VideoLAN developer, attributed this sluggishness to a bug in the Microsoft Defender update, which quarantined VLC's plug-in cache. The problematic Defender signature update is version 1.455.50.0, linked to Windows Update KB5121003 released on August 11th. Users can reset the plug-in cache to improve performance by either reinstalling VLC or using the built-in functionality to regenerate the cache with vlc-cache-gen.exe. Alternatively, users can reset preferences and cache files by searching for "VLC" and selecting the reset option. Microsoft has not yet provided a fix for these issues, and users may need to set an exclusion in Microsoft Defender for VLC Media Player to prevent unnecessary scans, enhancing its performance.
AppWizard
September 19, 2026
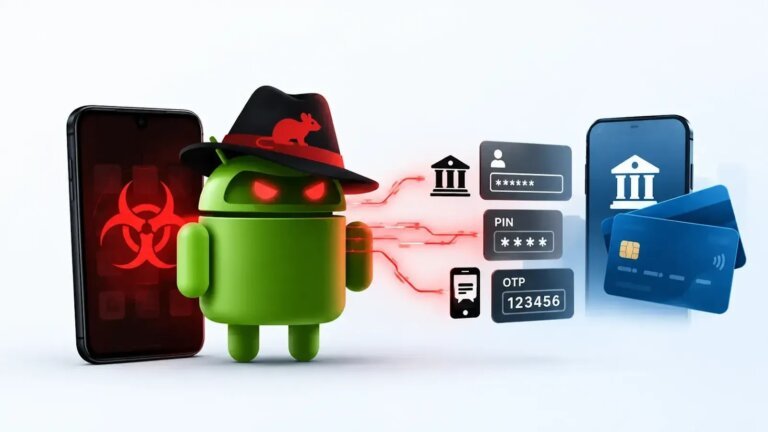
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
Winsage
September 15, 2026
Iranian state cyber actors are targeting individuals through popular messaging applications, using surveillance and data-stealing malware known as "Chosen Brick," which has been in use since at least 2025. This malware is designed for Windows systems and enables the theft of personal data, allowing Iranian spies to monitor perceived threats such as dissidents, activists, and journalists. The attacks typically begin with messages sent via WhatsApp or Telegram, impersonating trusted contacts. Attackers conduct extensive research on their targets to craft convincing messages that encourage victims to download malicious files disguised as legitimate applications. Once executed, Chosen Brick operates stealthily, evading detection and establishing a connection for command-and-control communications. It can enumerate processes, capture screen and audio content, extract sensitive information, and even wipe infected systems. Organizations suspecting compromise are advised to engage IT providers for investigations and to inform staff about potential risks. Recent alerts follow cyberattacks on water and energy sectors linked to Iran, with ongoing concerns about the implications for cybersecurity amid escalating military tensions. Additionally, five US agencies have reported that attackers are using AI-generated scripts to exploit vulnerabilities in critical infrastructure systems.
Search