kernel

AppWizard
September 18, 2026
Google's September 2026 Pixel Update Bulletin includes patches that affect standard Android platform code, relevant to both Pixel and non-Pixel devices, which have not been included in the regular monthly Android Security Bulletin. GrapheneOS has noted that Android 17 QPR1 introduced new developer APIs not present in the Android Open Source Project (AOSP) for the first time since Android Honeycomb, with one new package and modifications to sixteen others. GrapheneOS is backporting Pixel firmware and drivers from QPR1 onto Android 17 but lacks permissions to distribute this work. Additionally, there has been a delay in Google’s compliance with a GPL source request, with access granted over two weeks after the initial request. Starting in 2027, Google will require all Android app developers to register with them and provide legal identification and signing key evidence, complicating the process of sideloading unverified apps. GrapheneOS and other organizations are advocating for the Keep Android Open campaign against these developments, which may restrict competition and tighten Google's control over the Android ecosystem.
AppWizard
September 18, 2026
The new AndroidX Security State libraries, with stable releases of Security State v1.1.0 and Security State Provider v1.0.0, allow developers to evaluate the security status of individual device components. They provide three levels of security patch information: Device Security Patch Level (DSPL), Published Security Patch Level (PSPL), and Available Security Patch Level (ASPL). These libraries enable checks on critical components of the Android operating system, including system modules and the Linux kernel, which are represented by version numbers rather than monthly patch dates. Applications that prioritize security can utilize this detailed patch information to assess vulnerabilities, particularly those tracked as Common Vulnerabilities and Exposures (CVEs). The libraries also integrate with the Open Source Vulnerabilities (OSV) database for access to Android Security Bulletin data and device-specific vulnerability reports. Additionally, Android 17 allows manufacturers to declare individual security fixes beyond the stated security patch level, and Google is working with manufacturers to transition their OTA update clients to this new standardized system.
Winsage
September 18, 2026
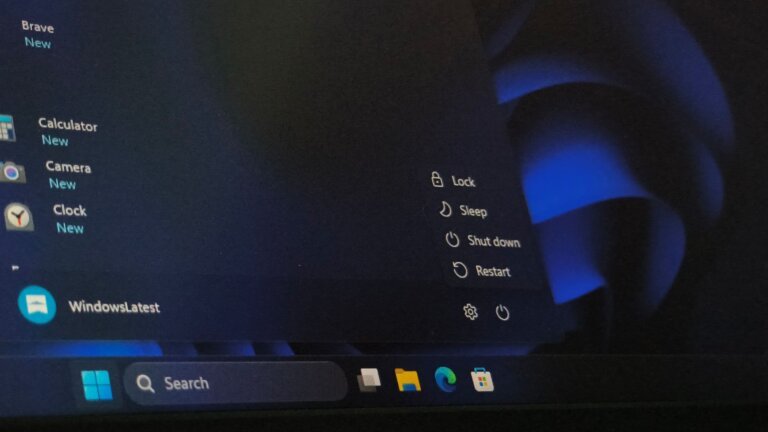
The Fast Startup feature in Windows, enabled by default, allows the kernel session to remain hibernated during shutdown, which results in quicker boot times by restoring a saved state. In contrast, selecting Restart clears the kernel session entirely, performing a complete boot of Windows. The process of shutting down with Fast Startup involves closing applications, logging off, keeping the kernel loaded in memory, saving the kernel and drivers to hiberfil.sys, and powering off, while Restart closes applications, logs off, ends the kernel session, and reboots immediately without saving a kernel snapshot. Fast Startup can lead to persistent issues from previous sessions, making Restart a better option for troubleshooting. To perform a full shutdown bypassing Fast Startup, users can execute the command "shutdown /s /t 0." Microsoft advises against permanently disabling Fast Startup, as it enhances shutdown-to-boot transitions.
Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
Tech Optimizer
September 11, 2026
Lakebase Postgres employs a disaggregated storage model that enhances data management through efficient caching, utilizing an object store like S3 for backups. The caching operates on two layers: within distributed storage for optimizing write and read performance, and on the Postgres compute side for ultra-fast access to frequently accessed pages. Traditional Postgres caching involves shared buffers and the OS page cache, which leads to double buffering and inefficiencies. Lakebase Postgres addresses these issues by implementing a local file cache (LFC) and larger shared buffers, allowing for more effective memory utilization without the drawbacks of the OS page cache. The shared buffers are set to a maximum of 1 GB, while the LFC can utilize up to 75% of DRAM. The introduction of huge pages reduces memory management overhead and improves performance, resulting in significant throughput increases and reduced latency in production environments. Recent enhancements have shown up to 2× throughput improvements and substantial reductions in CPU usage. The focus is now on extending these benefits to autoscaling Postgres computes, with plans to implement dynamic shared buffers and autoscaling huge pages.
Winsage
September 9, 2026
The September 2026 security cycle revealed a bifurcated approach to vulnerability management by Microsoft, focusing on cloud-side identity services with silent mitigations and traditional Patch Tuesday updates for on-premises Windows infrastructure. On September 3, Microsoft addressed nine cloud-side vulnerabilities, including two with a CVSS score of 10.0: CVE-2026-83711 (Azure AD B2C elevation of privilege) and CVE-2026-70352 (Azure AI Language Authoring missing authentication). Additionally, CVE-2026-83941 (Entra ID elevation of privilege, rated 9.9) and CVE-2026-80098 (Copilot Studio cryptographic flaw) were noted. On September 8, the Patch Tuesday update addressed 70 CVEs, including critical issues in the on-premises stack, such as CVE-2026-83939 (Windows Secure Kernel Mode elevation of privilege). CVE-2026-69414 (ShieldBreak), an elevation of privilege vulnerability in the Defender Malware Protection Engine, was patched out-of-band on September 3 after being publicly exposed for three weeks. Microsoft is shifting its Self-Service Password Reset (SSPR) enforcement to default to passkeys as of September 7, with plans to phase out SMS and voice-based authentication by February 2027. This aims to enhance security by moving away from legacy credentials.
Winsage
September 7, 2026
Microsoft has launched Project Zenith to improve the Windows 11 experience for developers, providing a streamlined environment primarily for high-end PCs. Devices under this initiative will come preloaded with essential development tools and optimized settings to reduce setup time. While the features are tailored for developers, similar configurations can be achieved on any Windows 11 machine by adjusting settings and installing applications like Visual Studio Code. Additionally, Microsoft plans to enhance security in Windows 11 by automatically enabling memory integrity protection on eligible devices starting next month.
Tech Optimizer
September 6, 2026
Iran has introduced its second domestically developed antivirus software, Ayyza, which utilizes artificial intelligence and machine learning to detect known and unknown cyber threats. The antivirus is designed to protect against malware, viruses, Trojans, ransomware, and advanced persistent threats (APTs). Ayyza's detection engine is developed in-house and operates at the Windows kernel level to enhance detection accuracy and speed while minimizing hardware resource consumption. It can receive updates offline or via Iran’s National Information Network. Ayyza's machine-learning capabilities allow it to identify emerging threats, including previously unknown malware and zero-day vulnerabilities. The company has also created complementary security tools, such as privileged access management (PAM) systems and data leakage prevention tools, to enhance overall cybersecurity. The company's products are currently used in various Iranian infrastructures, including banking, financial, and governmental systems.
Search