location data

AppWizard
October 2, 2026
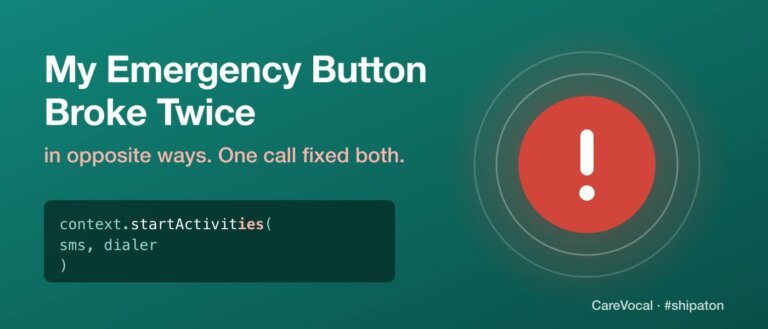
An Android application named CareVocal (internally referred to as CareBridge) was developed to facilitate communication for the user's mother living in a village. The app features three buttons: green for "feeling good," yellow for "something hurts," and red for "need help." Tapping the red button triggers three actions: saving an entry for her doctor, generating a pre-filled SMS to trusted contacts, and opening the phone dialer with the local emergency number pre-typed. The app requires the user to confirm sending the SMS and calling the emergency number to comply with Google Play's restrictions. During testing, issues arose where the SMS draft would not appear if the dialer was opened first, leading to adjustments in the code. A method was implemented to launch multiple intents simultaneously, ensuring that the SMS draft and dialer could be accessed without conflicts. Additionally, the recording feature was modified to start only after a second tap on the red button, separating it from the alert process to avoid distractions during emergencies. The app does not collect location data and is designed solely for logging and communication without diagnostic capabilities.
AppWizard
September 24, 2026
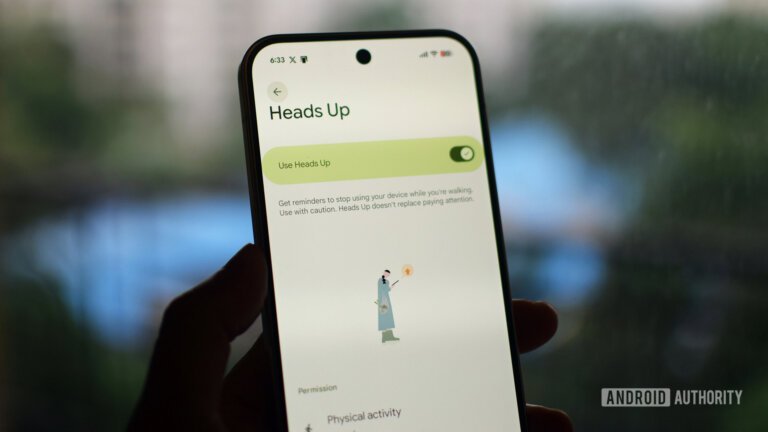
Google is winding down its "Heads Up" pedestrian safety feature within the Digital Wellbeing suite. The latest beta version of Digital Wellbeing has revealed code strings indicating that users will soon receive an in-app alert about the feature's impending removal. Heads Up, launched in 2021, was designed to enhance pedestrian safety by using motion sensors and location data to remind users to stay aware of their surroundings while walking with an unlocked screen. Initially available for Pixel devices, it later expanded to other Android phones. There is currently no specified timeline for the feature's removal, and Google has not provided a formal statement regarding its discontinuation.
AppWizard
September 7, 2026
Recent investigations have revealed that the Russian messaging application Blink sends user data directly to VK servers, despite publicly opposing VK. The app continuously tracks users' movements and transmits location data to MyTracker, an analytics system owned by VK, every few seconds. Additionally, Blink's main feature, Blink Maps, is hosted on VK's servers. Eight senior Blink employees and a former CEO have connections to VK, either having transitioned from VK to Blink or still maintaining roles at VK.
AppWizard
August 9, 2026
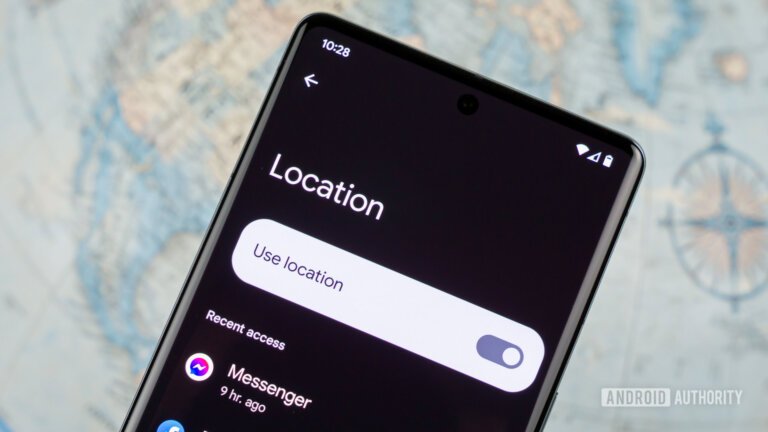
Third-party advertising tools embedded in Android applications are automatically collecting location data, often without the app developers' awareness. Software development kits (SDKs) used for advertising come with location data collection enabled by default, unless developers actively disable this feature. Historical location data has been sold to military and intelligence agencies, including the FBI, and used in immigration enforcement actions in the US. The Electronic Frontier Foundation (EFF) reported that app-level location permissions do not provide meaningful consent for location collection by third-party advertising SDKs. The EFF identified four advertising SDKs—InMobi, BidMachine, Verve's HyBid, and Huawei's Petal Ads—that collect and share location data by default. Two analyzed apps had been downloaded 60 million times without providing a privacy notice or seeking user consent for third-party location sharing. Users can manage location permissions through their device settings, but the EFF emphasizes that developers should ensure user data is not shared by default.
AppWizard
August 6, 2026
A recent investigation by the Electronic Frontier Foundation (EFF) revealed that many Android applications contain third-party code that automatically transmits users' precise location data to external companies, including advertisers and data brokers, once location permission is granted. There are no specific location permissions for Software Development Kits (SDKs) on Android, meaning that granting one app access allows all bundled components to access the same data. Developers may be unaware that their apps are configured to share location histories with external firms, as advertising SDKs often prioritize data collection for revenue generation. The EFF calls for advertising SDKs to stop making personal data sharing the default setting and urges developers to disable unnecessary data collection. Location data can reach data brokers, which may experience breaches, compromising user privacy and security. This situation poses hidden risks for investors in the mobile advertising sector, as legal challenges and reputational damage may arise from regulatory scrutiny of location data practices. The EFF emphasizes that app-level permissions do not provide meaningful consent for third-party data sharing, highlighting the value and risks associated with location data.
AppWizard
August 6, 2026
A report from the Electronic Frontier Foundation (EFF) highlights concerns about third-party software development kits (SDKs) in mobile applications collecting and sharing user location data with advertising companies, often without user consent. Many developers use these advertising SDKs for monetization, but their default settings allow for location data collection. This data is sent to advertising companies and location data brokers, which can misuse it in sensitive contexts. Users may unknowingly expose their location data when granting permissions to apps, as third-party SDKs can access this information without clear user awareness. The EFF identified several advertising SDKs, including InMobi, BidMachine, Verve’s HyBid, and Huawei’s Petal Ads, that collect and share location data by default. Developers are encouraged to review SDK settings to protect user privacy, and the EFF calls for regulatory scrutiny of data harvesting practices.
AppWizard
August 5, 2026
Advertising companies provide software development kits (SDKs) for mobile app monetization, which often automatically transmit users' location data to ad systems and location data brokers, raising privacy concerns. Many developers and users may be unaware of this data sharing. When developers allow SDKs to collect location data, it poses risks beyond targeted ads, including potential misuse by agencies like ICE and global surveillance. Location data brokers harvest precise movements of individuals, often without their consent, through mobile applications. Some apps directly collaborate with data brokers, while others leak data through advertising SDKs during real-time bidding (RTB) auctions. An incident in 2025 revealed that many apps unknowingly contributed to a location data broker's database. Developers must understand their SDKs' location-sharing practices to mitigate risks. Advertising SDKs can collect location data automatically once users grant permission, without specific permissions for the SDKs themselves. Precise location data can be collected when apps have location permissions, leading to potential privacy violations. Several SDKs have been identified as collecting location data by default, increasing the risk of unintentional data leaks. The Electronic Frontier Foundation (EFF) found that four advertising SDKs collect users' location data by default when location permissions are granted. InMobi encourages location sharing for higher revenue, while BidMachine updated its documentation after EFF's inquiry, confirming precise location data collection. Verve's SDK also collects location data by default but presents a cautious narrative in its Play Store guidance. Huawei's SDK recommends obtaining location permissions to enhance revenue, with default location sharing occurring if permissions are granted. Location data can be shared without users' knowledge or meaningful consent, complicating informed consent issues. The focus on four SDKs does not imply that others adequately protect location data, as many have faced criticism for similar practices. Studies indicate that SDKs often encourage increased data collection through design and documentation, leading to minimal control for developers over data transmission. The EFF's analysis highlights that advertising SDKs incentivize location data sharing through default settings and unclear documentation. Developers should assess third-party SDKs and disable unnecessary data collection. Regulators must hold developers accountable for unlawful data sharing, while legislators should enact laws to protect location privacy and address online behavioral advertising, which drives data tracking.
AppWizard
August 5, 2026
Developers often rely on third-party software development kits (SDKs) for mobile app monetization, which can compromise user privacy due to invasive data-collection features. The Electronic Frontier Foundation (EFF) has raised concerns about these SDKs' default settings that collect sensitive location data without explicit user consent. Location data is valuable for advertisers, allowing targeted marketing, but permissions granted to apps often extend to SDKs, enabling data collection without informed consent. The EFF emphasizes that app-level location permissions do not signify meaningful consent for third-party SDKs. The location data collected has been used by intelligence agencies and law enforcement, raising ethical privacy concerns. The EFF recommends that developers prioritize user privacy, regulators hold app developers accountable for unlawful data sharing, and legislators consider enacting federal laws similar to the GDPR to protect user privacy and potentially ban behavioral advertising.
Search