modifications

AppWizard
September 17, 2026
The Blood of Dawnwalker features a time mechanic that serves as a limited resource, creating a sense of urgency that some players find restrictive. Shaun Prescott expressed a desire for a more leisurely gameplay experience, which has led to the creation of the "Better Story Timer" mod, the most popular modification for the game. Konrad Tomaszkiewicz, the studio CEO, acknowledged player feedback regarding the time mechanic and indicated that it may be adjusted in the sequel, aiming to enhance urgency without compromising the overall experience. He noted that players can complete around 80 percent of the content despite the time constraint and observed a decline in complaints as more players finished the game, discovering they had more time than expected. The studio is also seeking a lead writer for the next installment in the Dawnwalker series.
Winsage
September 14, 2026
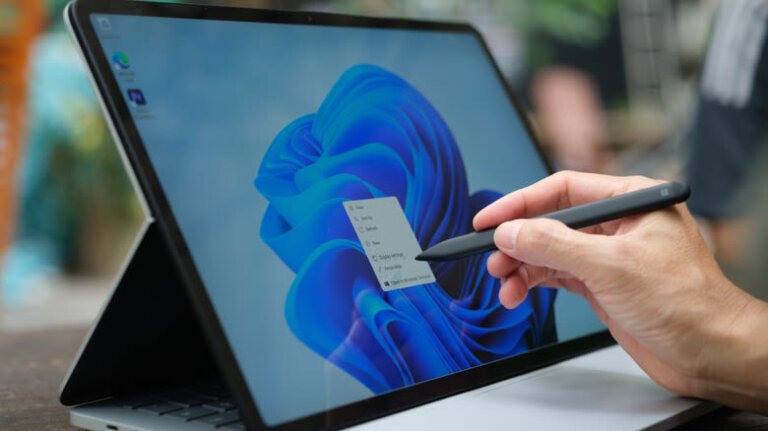
Many users are transitioning from Windows 10 to Windows 11 but are facing issues, leading some to consider alternatives like Linux due to performance, privacy, and AI integration concerns. The right-click menu in Windows 11 has been criticized for being cluttered and slow. Microsoft is addressing these issues with an update to streamline the context menu, making it more organized and faster-loading. This redesigned menu is currently available to users of the Windows 11 Insider Experimental Preview Build 26340.9212, released on August 17, 2026, with broader availability expected in the upcoming Windows 11 version 26H2 or later updates. The new context menu will feature a lighter design with frequently used functions like Cut, Copy, and Rename at the top, and options will be simplified and reorganized. Users will also be able to customize their right-click menus through the Settings menu and revert to the traditional Windows 10 context menus if desired.
AppWizard
September 12, 2026
Google Maps is experiencing a bug that affects traffic information, coinciding with the rollout of a redesigned media player interface for Android Auto that features a new squiggly audio playback progress line inspired by Material 3 design. User reactions to the new interface have been mixed, with some appreciating the improved visibility of the current track while others criticize the layout changes and seek ways to revert to the previous design, which is not straightforward. The rollout of these updates has been slow and inconsistent, with some users reporting different experiences based on their devices. Enhancements in the new design include expanded album art display and repositioned media playback buttons, which many users find beneficial for easier track changes while driving.
AppWizard
September 12, 2026
Enthusiasts in the emulation community have acquired a toolkit for the static recompilation of Nintendo Switch games on PCs, following the final update of the suyu emulator, which introduced Recompiler mode. This tool pre-compiles static code from the ARM AArch64 architecture into instructions for modern 64-bit x86 chips, allowing game logic to operate natively and reducing CPU overhead. The implementation is about 50% complete, focusing on code execution, while the graphics and audio components still rely on high-level emulation. Fully functional native ports will require third-party developers to create their own renderers for the Tegra GPU's graphics calls. The codebase allows the community to explore game structures, develop modifications, and create semi-native executables for PCs.
Winsage
September 10, 2026
Microsoft's Patch Tuesday on September 8, 2026, addressed two critical Windows privilege escalation vulnerabilities: CVE-2026-85880 and CVE-2026-81963, both with a CVSS score of 7.8. CVE-2026-85880 is a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC), allowing attackers with low-privilege local access to escalate privileges to SYSTEM. CVE-2026-81963 involves improper link resolution in the Windows Update Stack, enabling similar privilege escalation. Both vulnerabilities require no user interaction and have been actively exploited prior to the patch release. CISA added them to its Known Exploited Vulnerabilities catalog on September 8, 2026, with a remediation deadline of September 22 for U.S. federal agencies. CVE-2026-85880 affects various Windows 10 and Server versions but excludes Windows 11 and Windows Server 2025. CVE-2026-81963 impacts newer Windows platforms, including Windows 11 and Windows Server 2025. Microsoft released security updates for both vulnerabilities on September 8, 2026, and organizations are advised to prioritize these updates. Security teams should monitor for signs of privilege escalation and unusual SYSTEM-level activities related to these vulnerabilities.
Winsage
September 9, 2026
Recent investigations have identified the BlueMoon exploit kit, used by espionage-driven threat activity clusters, particularly linked to APT31, a China-aligned state-sponsored group, since August 28, 2026. BlueMoon exploits three vulnerabilities: CVE-2026-85046 (a type confusion vulnerability in Google Chrome's V8 engine), an unassigned V8 sandbox escape, and CVE-2026-85880 (a heap-based buffer overflow in Windows ALPC). Google and Microsoft have released patches for these vulnerabilities, which were exploited as "patch-gap" zero-days. The attack vectors typically begin with phishing emails that lead victims to malicious URLs, triggering the vulnerabilities for code execution and privilege escalation. Variants of BlueMoon have been detected, featuring modifications for specific campaigns. Notable attack chains include: - APT31 targeting NGOs and mining firms in the U.S. with a malicious browser add-on called GemStone. - UNK_LateNight targeting U.S. aerospace companies, deploying BlueMoon alongside the ShadowPad backdoor. - UNK_DoubleCheck targeting a Vietnamese manufacturer, using DLL sideloading to execute a Rust binary. - UNK_QuietRacket targeting government and financial organizations in Indonesia and Singapore, modifying BlueMoon to execute a .NET assembly. CISA added the Chrome flaw to its Known Exploited Vulnerabilities catalog on September 4, 2026, requiring federal agencies to apply patches by September 18, 2026. Indicators of compromise include specific process trees, files, folders, scheduled tasks, mutexes, and registry keys. Proofpoint has released detection rules to help organizations identify and mitigate these threats.
Search