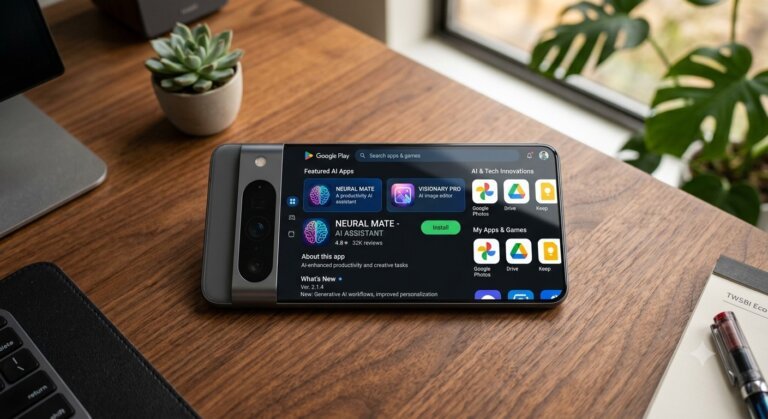
Google has introduced a feature that allows users to run privately created, AI-built Android applications on their smartphones via Google Play without public publication. This enables users to launch their apps using standard Google accounts while keeping them private, as these apps will not appear in Google Play search results or listings. The feature is available to users aged 18 and older in the United States, provided the apps comply with Google Play policies. Users can create apps using Google AI Studio through a process called “vibe coding.” Google plans to allow users to share their AI-built applications with trusted friends in the future and offers the possibility of transitioning popular personal apps into publicly published ones after passing trust and safety reviews. Additionally, Google is developing AI-driven tools to enhance the Google Play experience, including a personalized game recommendation engine called Game Finder, which will be available in English in the U.S. Users can curate game lists, engage in community discussions, and participate in gaming challenges. The Play Store's AI assistant, Ask Play, will receive updates for better app comparisons, and a new age-range feature will help developers create age-appropriate experiences for children.
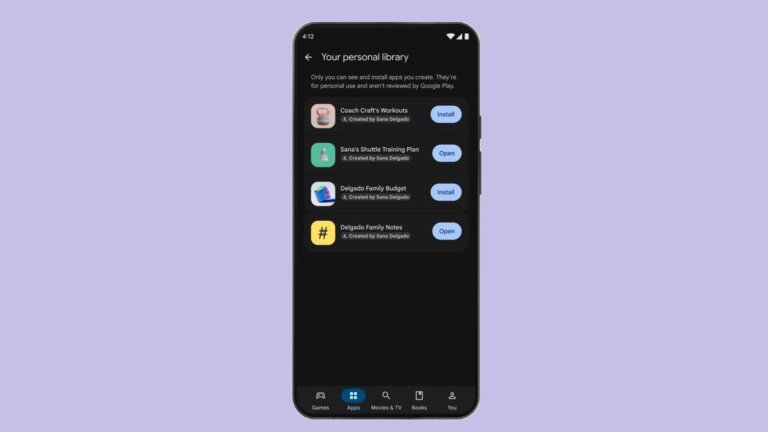
Google AI Studio is introducing tools for sharing personal software through a private section of the Play Store called "Your personal library," which does not require a developer account. This feature is currently available to U.S. users over 18 and allows them to upload or download their creations using standard login credentials. Users can initially share their vibe-coded software with a close circle of friends and family for testing purposes. Google plans to roll out this sharing feature in the coming months. Additionally, upgrades to the AI-powered Ask Play feature now allow users to compare applications, and enhancements to the Play Family Link service enable parents to set age ranges for their children's app access.
Researchers have identified a new Android malware called Hirudo, which steals bank account credentials by replacing legitimate banking applications with modified versions that disable security checks. Hirudo impersonates at least seven banks in Indonesia and targets financial institutions in China, India, Mexico, Morocco, and Thailand. It is delivered through seemingly legitimate applications related to shopping, adult content, or short drama, which prompt users to grant permissions, including Accessibility services.
Once installed, Hirudo uninstalls the genuine banking app, downloads a patched version, and uses Accessibility permissions to complete the installation. The malicious app retains nearly all of the original app's code but integrates a hooking engine based on open-source frameworks YAHFA and Dobby, employing evasion tactics such as substituting signing certificates, concealing Accessibility services, disabling screenshot protection, and altering key-attestation certificates.
Despite its advanced capabilities, Hirudo has limitations, including a publicly leaked attestation keybox and compromised certificates flagged by Google. Once operational, it can extract sensitive information, stream the screen, access cameras, and use fake checkout pages to collect payment PINs while misleading victims with fabricated success messages.
Hirudo represents an escalation in Android banking malware tactics, focusing on the security mechanisms of banking applications. Researchers recommend that banks enhance security measures and that Android users keep devices updated, avoid unofficial APK files, and conduct regular Play Protect scans.
Cybersecurity experts from Bitdefender have found that budget Android smartphones, such as the Doogee S200 X, Doogee Fire 3 Max, and Cubot KINGKONG X, may come pre-loaded with malware embedded in their firmware, posing significant security risks. This malware is introduced during the manufacturing process, particularly affecting devices with MediaTek chipsets. Thousands of users in around 150 countries, including Mexico, France, Italy, the United States, Germany, Brazil, and Spain, have been impacted. Bitdefender identified a network of 32 malicious applications disguised as legitimate utilities that generate fraudulent ad impressions. Some infected phones can function as residential proxies for criminal activities, including spam campaigns and DDoS attacks. Uninstalling the malicious app may not eliminate the infection if it is integrated into the system software, potentially requiring firmware-level remediation. Buyers of budget phones should research manufacturers' supply chain control and commitment to security updates.
The Pocket Casts app is now available for download on Android TV and Google TV devices, following its debut on Apple TV. This native app is designed for television screens and allows users to pair it with their existing accounts using a QR code, synchronizing all podcast subscriptions, playlists, and account data. It features a "Made for TV" section for video podcasts and maintains a similar interface to its Apple TV version. Users can continue audio playback while minimizing the app and easily access upcoming podcasts. Some users may face difficulties searching for the app directly on their devices, but it can be downloaded via a web browser on the Play Store.
Z.ai's GLM model identified 23 vulnerabilities in the Windows operating system, confirmed by Microsoft's Security Response Center (MSRC). This marks a significant advancement in commercial software security, demonstrating the model's autonomous capability in independent vulnerability discovery. Since the release of GLM-5.2, Z.ai has uncovered over 4,200 vulnerabilities across about 390 open-source projects, with over a thousand categorized as critical to high severity. Z.ai has established a public Security Disclosure Ledger to track its findings through a coordinated disclosure process. The confirmation of vulnerabilities by MSRC is notable due to the rigorous nature of their vulnerability triage operations. Z.ai's GLM-5.3 achieved a score of 84.5% on CyberGym, outperforming competitors like Anthropic's Mythos 5 and OpenAI's GPT-5.6 Sol. Reports indicate that NIST's AI safety division has flagged GLM-5.3 due to concerns about its cyber capabilities, particularly regarding the potential for modified versions to reduce safety features. Z.ai plans to continue targeting commercial software in its efforts.
Canada is focusing on digital sovereignty in sectors like cloud computing and telecommunications, but the operating systems for government computers have received less attention. A study suggests that adopting a national, free, and open-source operating system could save Canada millions over the next decade and reduce reliance on U.S. technology providers. Currently, Microsoft Windows dominates the Canadian desktop market with a 63.75 percent share, costing the government over 0 million annually. Trust in U.S. technology has declined among Canadians, with 60 percent feeling they can never trust Americans the same way again.
Open-source alternatives like Linux exist, which could be adapted into a national operating system based on Debian, allowing Canada to inspect and modify the code. Other countries, such as China and Germany, have developed their own operating systems, achieving significant savings. Transitioning to an open-source system would involve costs estimated between million and million over two years, compared to Germany's ZenDiS initiative. The projected gross savings from switching operating systems over ten years could range from 0 million to .13 billion, benefiting various sectors by reducing licensing fees and enhancing national security.
Google Play is transitioning from a traditional app store to a personalized hub for users. A key feature introduced is "vibe-coding," allowing users to create custom Android applications using natural language prompts without needing coding skills or a developer account. Personal apps remain private to the user's profile and can later be transitioned to a standard developer account for public release. Additionally, Google Play is enhancing app discovery through "Ask Play," which enables users to ask open-ended questions for tailored app recommendations, and integrating app suggestions into conversations via Gemini. For gamers, Google is launching Game Finder, which includes features like Gamer DNA for personalized gaming profiles, custom filters, peer insights, and game playlists. The Play Store is also being adapted for various hardware formats, including vehicles and large screens.
Epic Games is working on expanding Fortnite to the Linux gaming ecosystem by rebuilding Easy Anti-Cheat (EAC) to support Linux platforms. They plan to launch Fortnite on Linux via the Epic Games Launcher once EAC Linux v2 is functional with a critical mass of distribution maintainers. This initiative aims to enhance the gaming landscape for Linux users and encourage other developers to bring their games to the platform. Despite growing interest in Linux gaming, many major multiplayer titles remain hesitant due to security concerns. Epic is collaborating with Valve to address compatibility issues with the Steam Deck and has launched a new version of the Epic Games Store client that supports Linux.