quality updates

Winsage
October 14, 2026
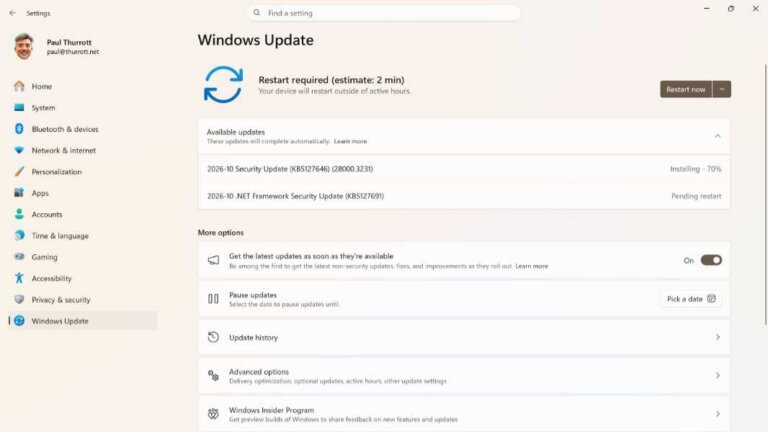
Microsoft has released its monthly quality updates for all supported versions of Windows 11 on the second Tuesday of October. This update marks the first Patch Tuesday update for Windows 11 version 26H2 and the end of support for version 24H2. Cumulative update KB5127648 is available for Windows 11 versions 24H2, 25H2, and 26H2, upgrading them to builds 26100.9711, 26200.9711, or 26300.9711. Key features include enhancements to File Explorer, support for Emoji 17.0, a new Tips widget, personalization improvements, an Accessibility setting for maximizing apps, precision touchpad functionality improvements, enhanced configuration options for the Copilot key, upgrades to the Windows Recovery Environment, and changes to Windows Backup. Windows 11 version 26H1 will receive cumulative update KB5127646, advancing it to build 28000.3231. This update features a redesigned Taskbar, a revamped Start menu, a new Windows Search experience, performance improvements in File Explorer, modernized progress indicators, Administrator Protection, and enhancements to the Get Started app.
Winsage
October 12, 2026
Microsoft has reminded IT administrators about the expiration of certificates that enable trusted connections between Windows devices and Windows Update servers, set to expire in May and June of 2027. Devices without replacement certificates by these deadlines may lose access to Windows Update services. Most supported Windows devices will receive new certificates automatically through security updates, but older or infrequently updated systems may require manual intervention. Organizations that do not update their devices risk losing access to critical updates, particularly unsupported Windows versions that will not receive necessary certificate updates. IT teams should audit device inventories and ensure compliance with updates, as systems on supported versions will obtain replacement certificates seamlessly. Upgrading unsupported systems is essential, and organizations are encouraged to conduct audits and expedite upgrade projects to avoid losing access to Windows Update.
Winsage
September 12, 2026
Windows 11 KB5124008, released on September 8, has caused various issues, including disruptions to WSL-based applications and Remote Desktop sessions. Users have reported problems with File History backups and instability in Explorer.exe, leading to system and GPU crashes. Microsoft confirmed a bug affecting applications using HCS-managed Linux virtual machines, particularly Claude Cowork, which is experiencing connectivity issues. Remote Desktop Services (RDS) are malfunctioning, leading to connection failures and sign-in problems. Additionally, some users face black screens upon sign-in due to Explorer.exe crashes. Reports indicate that File History is not recognizing external backup drives, and serious GPU issues have been reported on AMD Radeon systems, including driver timeouts and system freezes.
Winsage
September 3, 2026
Microsoft plans to automatically activate Memory Integrity on a broader range of eligible systems starting October 2026, rolling it out through standard Windows quality updates. Prior to activation, Windows will assess hardware, drivers, and performance to ensure compatibility. Memory Integrity, part of Virtualization-based Security (VBS), uses the Windows hypervisor to create a secure environment for integrity checks on kernel code. Compatibility with drivers is crucial, as many older applications may not meet the stricter standards required for HVCI. Potential compatibility issues may arise with anti-cheat solutions, third-party input methods, and banking protection programs, which could lead to software malfunctions or boot failures. A readiness check will evaluate hardware compatibility, with eligible systems including Intel processors from the 8th generation, AMD processors from Zen 2, and Qualcomm Snapdragon 8180 or newer, along with specific RAM and storage requirements. The rollout will be gradual, and users who previously disabled HVCI will not face unexpected reactivation. Microsoft recommends updating affected applications or drivers in case of compatibility issues.
Winsage
September 2, 2026
Microsoft will automatically enable its Memory Integrity feature on more eligible Windows PCs starting in October 2026, enhancing kernel-level protection. PCs with Memory Integrity currently disabled will retain their settings. Windows will also activate Virtualization-based Security (VBS) where necessary, which supports Memory Integrity. An automatic assessment will determine device eligibility based on hardware capabilities and compatibility. The rollout applies to Windows 11 installations meeting specific hardware specifications, including an 8th Generation or newer Intel processor or AMD Zen 2 or newer processor, at least 8GB of RAM, an SSD with a minimum of 64GB, compatible drivers, and enabled hardware virtualization. Memory Integrity, also known as Hypervisor-Protected Code Integrity (HVCI), has been part of Windows since the Windows 10 era and is now more integral to Windows 11 security for new installations. However, it may impact gaming performance, leading some gamers to disable it, which Microsoft has acknowledged in its recommendations.
Winsage
August 14, 2026
Windows 11's August 2026 Patch Tuesday update has been released, addressing 421 security vulnerabilities, including 400 specific to the Patch Tuesday release. The update rectifies at least 37 remote code execution bugs and five elevation-of-privilege vulnerabilities. Microsoft advises users to implement the update within three days for security. The update includes fixes for other Microsoft products like Entra, Office, and Teams. Users should verify their Windows 11 build number, with recommended versions being 26200.9168 for 25H2 and 26100.9168 for 24H2. The update is identified as KB5121003 and may require up to two reboots to apply fully. Key areas of focus in the update include the kernel, Remote Desktop, DNS, DHCP, SMB, and Windows Defender Firewall. Microsoft emphasizes the importance of timely updates and recommends limiting the deferral period for quality updates to less than three days.
Winsage
July 14, 2026
Microsoft has revised its guidance on Windows updates, urging users to install them within three days due to the rise of AI-driven cyber threats. Jeremy Chapman from Microsoft 365 emphasized the need for timely updates, recommending a maximum deferral period of two days for quality updates. In June, Microsoft patched 206 vulnerabilities, highlighting the importance of these updates to avoid significant risks. AI can help attackers exploit vulnerabilities quickly, making the practice of delaying updates obsolete. Microsoft has also developed an AI tool, MDASH, to identify vulnerabilities in Windows code.
Winsage
July 11, 2026
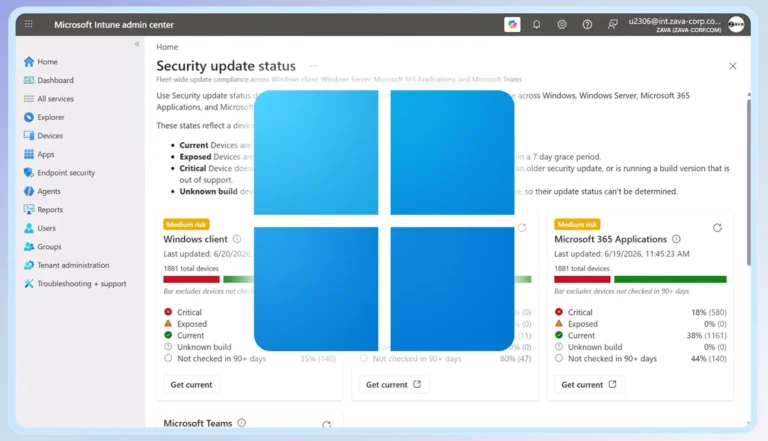
Microsoft is advocating for a reevaluation of Windows patch management practices due to the rapid evolution of artificial intelligence (AI) impacting cybersecurity. The company emphasizes that traditional timelines for patch deployment, typically spanning several weeks after the monthly Patch Tuesday, are inadequate against modern cyber threats. Microsoft recommends organizations shorten deployment windows to under three days for quality updates, with immediate installation deadlines and minimal user grace periods. To support these changes, Microsoft is enhancing Windows Autopatch with a new reporting dashboard for patch compliance and security insights. The company is promoting cloud-managed deployment through Microsoft Intune and Windows Autopatch while continuing to support legacy tools. Additionally, Microsoft is introducing Windows Hotpatch technology, allowing security updates to be installed without immediate reboots, and advocating for the use of identity-based access controls to isolate unpatched devices. The guidance reflects a shift from scheduled patching to continuous risk management, encouraging organizations to prioritize high-risk assets and automate update deployments. Microsoft is also investing in AI-assisted vulnerability discovery and automated code analysis to improve defensive capabilities. The overarching message is that enterprises must adapt their update strategies to address the accelerated pace of AI-driven exploitation.
Winsage
July 10, 2026
Microsoft advises organizations to expedite their Windows update deployment timelines due to advancements in artificial intelligence that allow cyber attackers to quickly exploit vulnerabilities after security updates are released. Jeremy Chapman, Director of Microsoft 365, warns that delaying critical quality updates with security fixes increases the risk of exploitation. Microsoft recommends a quality update deferral period of fewer than three days, update deadlines of zero or one day, and a grace period of no more than two days. The Windows Autopatch report within Microsoft Intune helps identify unpatched devices, allowing administrators to adjust update deferral policies. Organizations can configure update delivery settings through policy controls in Windows Autopatch and Microsoft Intune, as well as other management tools like Microsoft Configuration Manager and Windows Server Update Services. Microsoft also promotes the use of Hotpatch for quicker installation of security updates without rebooting and encourages Conditional Access policies to restrict access to corporate resources for devices that lack required updates.
Winsage
July 10, 2026
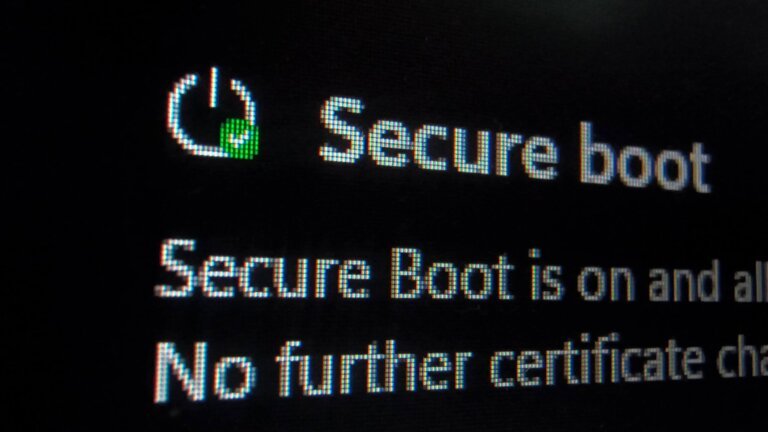
Microsoft has acknowledged that some Windows 11 PCs are facing issues with Secure Boot certificate updates, which may fail to install or be blocked. The company is working with PC manufacturers to develop a patch, while users may need to take proactive measures if their certificates are obstructed. Microsoft has temporarily halted the rollout of Secure Boot for certain devices due to complications, and affected users will receive detailed error messages in the Windows Security app regarding their Secure Boot certificates. Secure Boot certificates issued in 2011 have expired, and Microsoft is replacing them with new certificates issued in 2023. Most modern hardware is already utilizing the new certificates, but some devices may have disabled Secure Boot or faulty firmware. Users can check their Secure Boot status in the Windows Security app. HP has confirmed that Secure Boot updates are being blocked on some of its PCs due to a BitLocker issue, which prevents the installation of new certificates. Microsoft has paused Secure Boot certificate updates for devices affected by known issues while collaborating with manufacturers to identify specific devices or firmware complications. A firmware update will be necessary for affected devices, but it is not yet available. The majority of PCs have received the Secure Boot certificates via Windows Update, but compatibility issues may prevent some devices from receiving the update. Older devices or those not among the OEM’s top-selling models may not receive updates if the UEFI firmware is unsupported. Secure Boot is a security feature required for Windows 11, preventing unauthorized software from executing at boot. While an expired Secure Boot certificate does not stop a PC from functioning, it may limit long-term security protection. Microsoft advises users not to disable Secure Boot, as it would compromise security further.
Search