regulatory scrutiny

Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If you hold Microsoft 365 E5, you have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly platform. CrowdStrike is suggested for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses, VIPRE for budget-conscious mixed estates, and Expel for tool-agnostic managed detection and response. Antivirus and EDR are now unified under a single agent, and organizations should inquire about update staging processes to avoid issues like those experienced in July 2024 with a major vendor's faulty content update. Independent tests from organizations like AV-Comparatives and AV-TEST are crucial for evaluating protection rates and false positives. Linux servers require attention as they are often targeted by ransomware. When deploying endpoint protection, avoid running two real-time agents simultaneously, activate prevention features promptly, and test deployments on critical applications first. Organizations should confirm their Microsoft licensing covers necessary features and ensure there is a plan for responding to alerts. Common pitfalls include neglecting identity management and failing to test response workflows before incidents occur.
Tech Optimizer
September 10, 2026
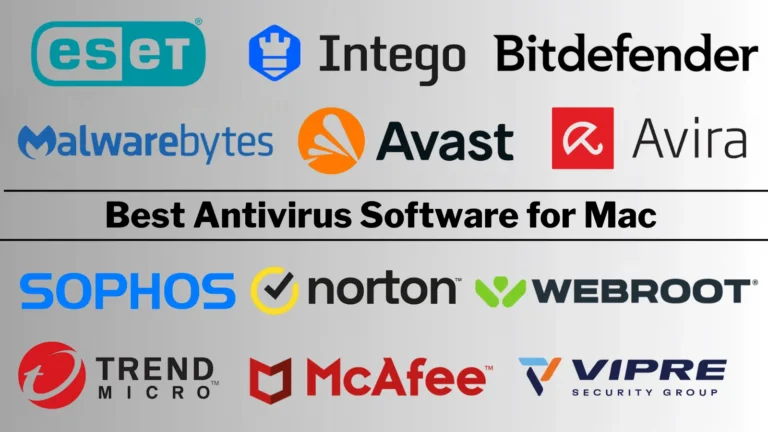
Apple provides built-in security features for macOS, including XProtect, Gatekeeper, and automatic malware removal, which contribute to the safety of Macs. However, these protections do not effectively address threats like infostealers, phishing, and adware. For enhanced security, third-party antivirus solutions are recommended. Bitdefender is noted for its strong detection rates and minimal system impact, making it suitable for most users. Intego specializes in Mac-specific threats and is ideal for users focused solely on Apple products. ESET and Trend Micro are recommended for businesses needing centralized management. F-Secure is recognized for its privacy-focused approach, while Norton offers a comprehensive suite of security features. AVG provides free real-time protection suitable for low-risk personal use, but may not be adequate for business needs. CleanMyMac is a maintenance tool rather than a traditional antivirus, focusing on system cleanup and optimization. Users should avoid running multiple real-time scanners simultaneously and ensure they purchase appropriate licenses for business use. It's important to evaluate the necessity of additional features and consider long-term pricing when selecting antivirus software.
Tech Optimizer
September 10, 2026
Bitdefender is recognized for its strong detection capabilities, mid-range pricing, and minimal system impact. Malwarebytes offers a free scanner for cleaning infected Macs, while Intego specializes in macOS with features tailored for Apple users. Norton provides a comprehensive security package with VPN, backup, and identity monitoring features. Gen Digital owns Norton, Avast, AVG, and Avira, indicating that these brands share threat intelligence and engineering resources. The 2026 Mac Antivirus Scorecard ranks Bitdefender highest with a score of 8.8, followed by Intego (8.2), Malwarebytes (8.3), ESET (8.3), and Norton (7.4). Pricing structures often include discounted first-year rates that can double upon renewal. Free options include Avast and Avira with real-time protection, while Malwarebytes offers a free on-demand scanner. Multi-device licensing can provide better value, and business Macs should use business licenses for essential features. macOS has built-in protections like XProtect and Gatekeeper, but third-party antivirus solutions can enhance security against newer threats.
AppWizard
August 6, 2026
A recent investigation by the Electronic Frontier Foundation (EFF) revealed that many Android applications contain third-party code that automatically transmits users' precise location data to external companies, including advertisers and data brokers, once location permission is granted. There are no specific location permissions for Software Development Kits (SDKs) on Android, meaning that granting one app access allows all bundled components to access the same data. Developers may be unaware that their apps are configured to share location histories with external firms, as advertising SDKs often prioritize data collection for revenue generation. The EFF calls for advertising SDKs to stop making personal data sharing the default setting and urges developers to disable unnecessary data collection. Location data can reach data brokers, which may experience breaches, compromising user privacy and security. This situation poses hidden risks for investors in the mobile advertising sector, as legal challenges and reputational damage may arise from regulatory scrutiny of location data practices. The EFF emphasizes that app-level permissions do not provide meaningful consent for third-party data sharing, highlighting the value and risks associated with location data.
AppWizard
August 6, 2026
A report from the Electronic Frontier Foundation (EFF) highlights concerns about third-party software development kits (SDKs) in mobile applications collecting and sharing user location data with advertising companies, often without user consent. Many developers use these advertising SDKs for monetization, but their default settings allow for location data collection. This data is sent to advertising companies and location data brokers, which can misuse it in sensitive contexts. Users may unknowingly expose their location data when granting permissions to apps, as third-party SDKs can access this information without clear user awareness. The EFF identified several advertising SDKs, including InMobi, BidMachine, Verve’s HyBid, and Huawei’s Petal Ads, that collect and share location data by default. Developers are encouraged to review SDK settings to protect user privacy, and the EFF calls for regulatory scrutiny of data harvesting practices.
AppWizard
August 4, 2026
Google will require mandatory identity verification for all developers creating applications for the Android platform, affecting those from countries under U.S. sanctions, such as Russia, Iran, Cuba, and North Korea, who will be excluded from the verification system and may not distribute their apps internationally. The new regulations apply to developers of apps for Android 7 and later versions.
Search