scripts

Tech Optimizer
September 21, 2026
More than 5,400 websites across over 2,200 organizations have been compromised to propagate malware, primarily affecting small businesses like clinics and online retailers. The attack mechanism involves malicious code that triggers a deceptive CAPTCHA, instructing users to execute commands that can download malware. Attackers are using the BNB Smart Chain test network to store instructions, making it harder for investigators to shut down operations. A newer variant of the attack uses WebRTC technology to establish encrypted connections for delivering additional malicious code. To protect against these threats, users should avoid pasting commands from websites, be suspicious of unusual CAPTCHA instructions, use strong antivirus protection, keep systems updated, take action if commands are executed, and small business owners should regularly verify their website's integrity.

AppWizard
September 19, 2026
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
BetaBeacon
September 18, 2026
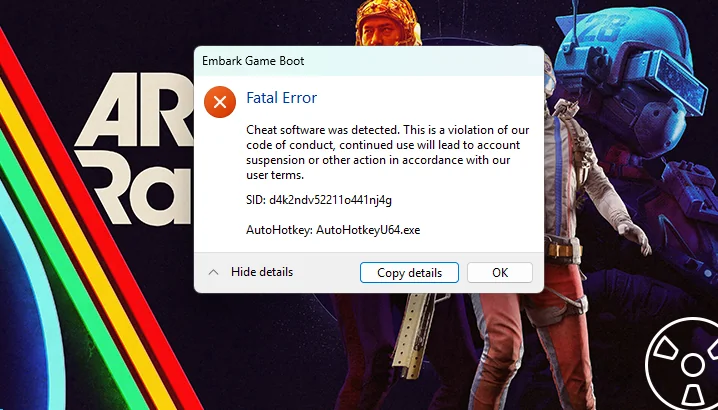
- Pokémon Infinite Fusion is a standalone game built in RPG Maker XP, using the RGSS scripting layer. - The game is not a ROM, cartridge dump, or console to emulate, but rather a folder of Ruby scripts, tileset graphics, and audio files. - The mainline build of the game reached version 6.7.2 on October 2, 2025, and was updated to version 6.8.2 by August 2026. - The game combines two Pokémon into a single custom sprite and blended stat line, generating the combined artwork procedurally. - The Android-specific performance complaints come from the CPU doing image layering work in real time when compositing fusion sprites on lower-end devices.
Winsage
September 15, 2026
Iranian state cyber actors are targeting individuals through popular messaging applications, using surveillance and data-stealing malware known as "Chosen Brick," which has been in use since at least 2025. This malware is designed for Windows systems and enables the theft of personal data, allowing Iranian spies to monitor perceived threats such as dissidents, activists, and journalists. The attacks typically begin with messages sent via WhatsApp or Telegram, impersonating trusted contacts. Attackers conduct extensive research on their targets to craft convincing messages that encourage victims to download malicious files disguised as legitimate applications. Once executed, Chosen Brick operates stealthily, evading detection and establishing a connection for command-and-control communications. It can enumerate processes, capture screen and audio content, extract sensitive information, and even wipe infected systems. Organizations suspecting compromise are advised to engage IT providers for investigations and to inform staff about potential risks. Recent alerts follow cyberattacks on water and energy sectors linked to Iran, with ongoing concerns about the implications for cybersecurity amid escalating military tensions. Additionally, five US agencies have reported that attackers are using AI-generated scripts to exploit vulnerabilities in critical infrastructure systems.
Winsage
September 12, 2026
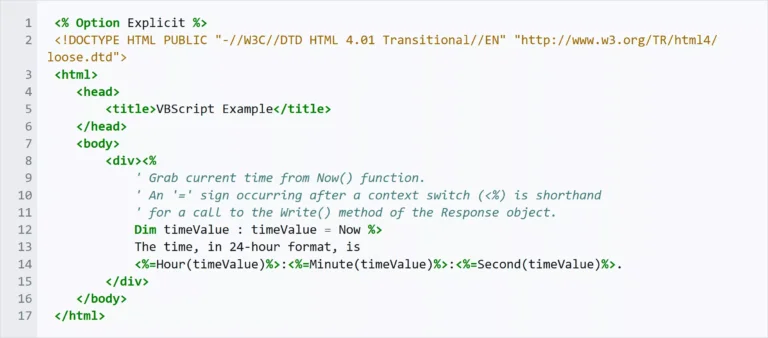
Microsoft is phasing out VBScript and urging organizations to transition to PowerShell. The Slmgr.vbs tool, used for managing Windows activation, will lose functionality as VBScript is deprecated. Slmgr.vbs allows users to install product keys, activate Windows, and check licensing status. VBScript will soon only be available as a Feature on Demand, requiring manual installation in future updates. PowerShell's OSLicense module offers similar capabilities to Slmgr.vbs for managing activation information. The OSLicense module is available for Windows 11 users after the August 2026 Preview update and will be supported in the next major release of Windows Server. Organizations are advised to review their existing scripts and tools to adapt to this transition.
Winsage
September 11, 2026
Many organizations still use legacy Windows activation scripts based on slmgr.vbs, which are integrated into deployment workflows and IT management tools. Microsoft is phasing out VBScript, which these automations rely on, leading to potential activation failures in newer Windows versions. Microsoft recommends transitioning to the OSLicense PowerShell module to replace slmgr.vbs functions. Organizations should identify dependencies on VBScript components and test replacement scripts before production deployment. Compatibility of OSLicense with various Windows releases must be confirmed, and organizations may need to invest time in testing, documentation, retraining, and fallback planning during the migration process. Proactive migration planning can ease the transition compared to delaying until VBScript is fully removed.
Winsage
September 4, 2026
There is a divide between casual Windows users and engaged enthusiasts, with passive users often accepting default settings that contribute to system bloat. Passive users enable telemetry and promotional content by not customizing their installations, while active users take steps to enhance privacy and performance. Microsoft interprets user inaction as approval for unwanted features, leading to an accumulation of bloatware and unnecessary updates. The Connected User Experiences and Telemetry service collects user data, justifying the inclusion of features like Copilot, which many users may not want. Users face challenges in maintaining control over their systems, often needing technical knowledge to opt out of unwanted features. Microsoft's feedback system is inadequate, interpreting silence as consent rather than a lack of interest, making it difficult for users to effect meaningful change.
Search