Security Assessment

AppWizard
October 6, 2026
Apple has removed the decentralized messaging application Bitchat, developed by Twitter co-founder Jack Dorsey, from its App Store in India following a directive from the Indian federal government under Section 69A of the Information Technology Act, citing national security. The notice from Apple's App Review team, shared by Dorsey on October 3, 2026, did not specify the illegal content. The app remains available in other regions, but users in India will lose access to TestFlight testing and public beta links. This action follows a previous request made on July 23, 2026, by the Indian Cyber Crime Coordination Centre to GitHub to disable access to three Bitchat repositories, invoking Section 79(3)(b) and Rule 3(1)(d). The Internet Freedom Foundation has contested the July order, claiming authorities bypassed established blocking frameworks. Bitchat, introduced as open-source software in July 2025, allows local Bluetooth mesh communication and internet messaging without relying on a central server, raising concerns for law enforcement. The timing of the restrictions coincided with youth-led protests in India, which led to a significant increase in Bitchat downloads, accounting for about 85% of the app's global downloads during a protest period from July 17-23. Despite the removal, existing installations can still communicate locally without needing app store access. Previously, in May 2023, India invoked Section 69A against other messaging applications, and China also mandated Bitchat's removal in April 2026 for similar reasons. Digital rights advocates argue the government's justification for the ban is concerning as it sets a precedent for restricting software based on technical capabilities.
AppWizard
October 5, 2026
Google has launched AndroidX Security State libraries, enabling applications to verify security patch status at a granular level for individual components. This allows developers to conduct precise security verifications tailored to their applications' needs. The libraries categorize security patch levels into Device SPL, Published SPL, and Available SPL, providing enhanced visibility into device security. Functions such as queryAllAvailableUpdates() and areCvesPatched() help identify pending updates and check CVE status. The Security State Provider library standardizes communication for update notifications among OEMs.
Tech Optimizer
October 2, 2026
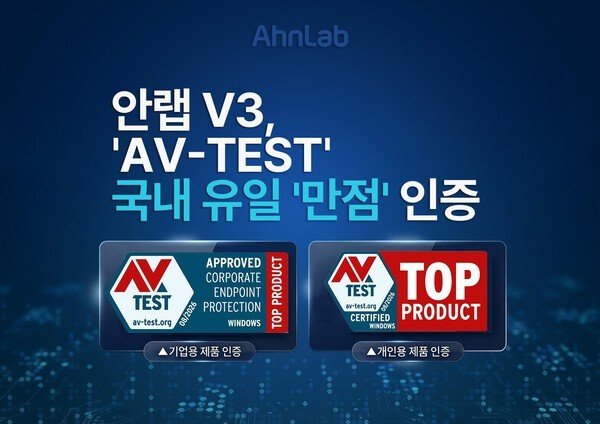
AhnLab’s V3 security software achieved a perfect score of 18 points in AV-TEST’s evaluation for antivirus software targeting the Windows operating system, conducted for July-August 2026. The evaluated products were V3 Endpoint Security and V3 Internet Security. AV-TEST assesses security products based on protection, performance, and usability, with each category scoring up to 6 points. AhnLab has participated in AV-TEST’s evaluations since 2013 and competes with major security companies like Microsoft, Kaspersky, and Bitdefender.
Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Tech Optimizer
August 27, 2026
A network of fraudulent websites, branded as SysScan, has been discovered, which falsely claims to evaluate antivirus software effectiveness through deceptive security scans. These sites manipulate users into uninstalling legitimate antivirus products and disclosing sensitive personal and banking information. Eleven distinct domains associated with SysScan have been identified, all hosted on a single server. The fraudulent scans generate misleading results based on static findings rather than actual system assessments, and users are coerced into believing their computers are at risk. The scams misrepresent normal browser behaviors as security threats and instruct victims to uninstall their antivirus software, compromising their defenses. The operation targets both individual and business users, collecting extensive personal information and utilizing remote-access tools. The data submitted is sent to Telegram via its bot API. Users are advised to disconnect from the internet and secure their devices if they suspect they have been compromised. Indicators of compromise include specific IP addresses and domains associated with the scam.
Tech Optimizer
May 28, 2026
CertiK has launched the CertiK Skill Scanner, a security solution designed to protect AI Agents and third-party AI Skills. It targets AI Skill marketplaces, enterprises, developers, and users, focusing on identifying risks during execution, particularly in financial transactions. The scanner can be integrated into publishing pipelines for automatic reviews and provides a scored assessment of risks with verdicts of “pass,” “warn,” or “fail.” It boasts a 90.5% precision rate in identifying security risks. The scanner is already deployed in select Web3 environments and aims to expand its integrations. CertiK, founded in 2017, is a leading Web3 security service provider, having worked with over 5,000 enterprise clients, including Binance and Ant Group.
Search