security issues

Tech Optimizer
September 23, 2026
A new tool named BigDiskBuster has been released on GitHub, which disrupts Microsoft Defender Antivirus by preventing it from installing updates. It does this by consuming available disk space during the update process, causing Defender to remain on its current version and unable to receive new platform or signature updates. BigDiskBuster operates as a local denial-of-service technique and requires prior access to the target machine to execute. The tool was created by researcher Abdelhamid Naceri, known as Nightmare Eclipse, who has previously worked on similar projects. As of now, there is no CVE identifier, patch, or advisory from Microsoft regarding this issue.
Winsage
September 23, 2026
Security researcher Abdelhamid Naceri, known as Nightmare Eclipse, released a zero-day exploit called BigDiskBuster that targets Microsoft Defender, preventing antivirus updates and leaving systems vulnerable. BigDiskBuster operates across all supported Windows versions and must run in the background to block updates. Naceri has previously released a similar exploit called UnDefend and has a history of releasing multiple zero-day exploits since April 2026 amid a dispute with Microsoft. Two weeks before BigDiskBuster, he introduced another exploit named ShieldCrash, which grants SYSTEM access and circumvents a patched flaw. Naceri's recent exploits include tools like LegacyHive, BlueHammer, RedSun, YellowKey, GreenPlasma, and MiniPlasma, all targeting Microsoft Defender and other Windows components. Microsoft has warned of potential legal action against malicious activities but has not commented on BigDiskBuster.
Tech Optimizer
September 7, 2026
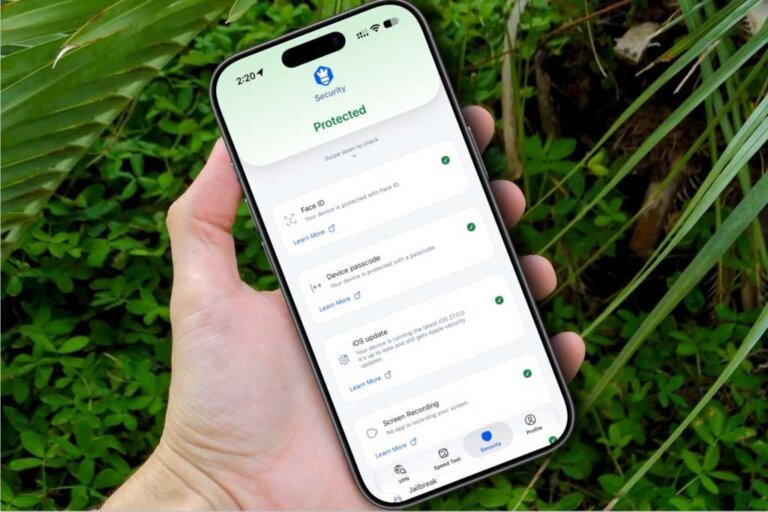
Intego ONE Complete has launched the Intego ONE: VPN & Wi-Fi Security app for iPhone, available at no extra charge to Complete subscribers. The app provides VPN protection, Wi-Fi security assessments, and checks on built-in iPhone security settings but does not function as antivirus software. It enhances existing Apple security measures by addressing vulnerabilities related to insecure Wi-Fi connections and unprotected internet access. The app is accessible to both new and existing subscribers, and Intego is currently offering a 50% discount on subscriptions until September 30, 2026. Intego ONE is available in three tiers: Essential, Advanced, and Complete, with the Complete tier including the new iPhone app. The app features a VPN that encrypts internet connections on public Wi-Fi, Wi-Fi security checks, and assessments of iPhone security settings. While traditional viruses are rare on iPhones, threats like spyware and exploits still exist. The app does not replace Apple's malware protection but complements it. Intego ONE Complete is recommended for Mac and iPhone owners, particularly those who travel frequently or connect to public Wi-Fi. The pricing includes various deals, with a 50% discount currently available and a subsequent 35% discount after the promotional period.
Winsage
August 29, 2026
Nvidia will stop regular support for Windows 10 drivers for GeForce graphics cards by October 2026, after which users will receive only quarterly security updates until October 2029. The last Game-Ready driver for Windows 10 will be released in October 2026, with the first driver lacking Windows 10 support scheduled for November 2026. Modern GeForce RTX graphics cards will not receive new drivers if running on Windows 10 after October 2026. Nvidia's support for older architectures like Maxwell, Pascal, and Volta will end in October 2025, with quarterly updates until October 2028. Users are encouraged to transition to Windows 11, as Microsoft will conclude general support for Windows 10 on October 14, 2025. Users should check hardware compatibility for Windows 11, including TPM 2.0 and Secure Boot. The last regular driver version for Windows 10 will remain available after October 2026, but Nvidia will not be obligated to address routine bugs or compatibility issues thereafter.
Tech Optimizer
August 27, 2026
A network of fraudulent websites, branded as SysScan, has been discovered, which falsely claims to evaluate antivirus software effectiveness through deceptive security scans. These sites manipulate users into uninstalling legitimate antivirus products and disclosing sensitive personal and banking information. Eleven distinct domains associated with SysScan have been identified, all hosted on a single server. The fraudulent scans generate misleading results based on static findings rather than actual system assessments, and users are coerced into believing their computers are at risk. The scams misrepresent normal browser behaviors as security threats and instruct victims to uninstall their antivirus software, compromising their defenses. The operation targets both individual and business users, collecting extensive personal information and utilizing remote-access tools. The data submitted is sent to Telegram via its bot API. Users are advised to disconnect from the internet and secure their devices if they suspect they have been compromised. Indicators of compromise include specific IP addresses and domains associated with the scam.
AppWizard
August 22, 2026
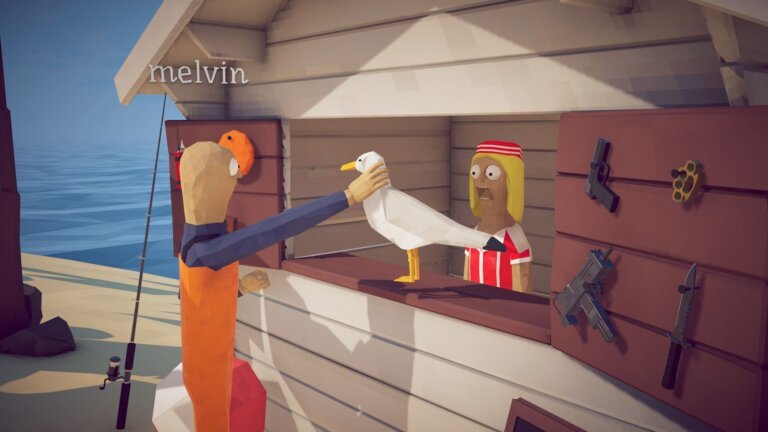
How to Fish is a physics-based fishing simulator available on Steam for 1 to 4 players, allowing them to engage in absurd aquatic adventures. Players can launch fish into the air and shoot them with firearms, barbecue seagulls, and gamble their catches. The game features NPCs that provide quests and a variety of islands to explore, including larger marine life like sharks and king crabs. Feedback from the Steam community has been mostly positive, though some concerns about security issues have been raised. The game is currently offered at a discounted price of £4, down from £6.40, with the promotion ending on August 27.
Winsage
August 13, 2026
Nightmare Eclipse has released a new zero-day exploit called ShieldBreak, which can bypass Microsoft's RoguePlanet patch (CVE-2026-50656) and allow attackers to gain SYSTEM privileges on fully patched Windows 10, Windows 11, and Windows Server systems. The exploit has been confirmed by security expert Kevin Beaumont, who provided detection methods for it. ShieldBreak is the tenth zero-day from Nightmare Eclipse since April and was released shortly after Microsoft's monthly Patch Tuesday. The exploit allows local privilege escalation and has a 100% success rate on the latest version of Windows 11 and Windows Server 2025, while Windows 10 remains vulnerable. Microsoft is aware of the vulnerability and is investigating it, emphasizing the importance of coordinated vulnerability disclosure. Previous exploits from Nightmare Eclipse include LegacyHive and GreatXML, with earlier vulnerabilities having been patched but recent ones still unaddressed. Microsoft had threatened legal action against Nightmare Eclipse in May but later reconsidered its approach to vulnerability disclosure.
Search