security threats

Tech Optimizer
September 21, 2026
The landscape of computer security has changed significantly over the past two decades. In 2026, antivirus protection remains important, but the need for separate third-party programs has decreased for many users due to the built-in Microsoft Defender in Windows 11, which is activated by default and effectively blocks 100% of common malware samples according to independent testing by AV-TEST. Windows 11 also includes additional protective features like SmartScreen and a robust Firewall. While dedicated security suites from companies like Norton and Bitdefender offer advanced functionalities, many users may find adequate protection with the built-in tools. Research from AV-Comparatives indicates that performance varies among security programs, particularly against real-world attacks. Phishing attacks accounted for approximately 60% of initial access points in incidents examined by the ENISA Threat Landscape report from 2025, highlighting that user behavior is a significant vulnerability. Modern web browsers and operating systems have enhanced their security measures, with Google Chrome, Microsoft Edge, macOS, and Android incorporating features to protect users from harmful websites and downloads. For the average Windows 11 user who keeps their system updated and practices safe browsing, built-in protection is generally sufficient, though paid antivirus options can provide additional tools.

AppWizard
September 19, 2026
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.
Winsage
September 17, 2026
Devices operating on Windows 11 24H2 Home and Pro editions will stop receiving updates starting October 13, 2026. The Enterprise and Education editions of Windows 11 24H2 will continue to receive mainstream support until October 2027. Microsoft encourages users to upgrade to Windows 11 25H2, which became available in September 2024. Systems running Windows 11 24H2 Home and Pro that are not managed by IT will automatically upgrade to Windows 11 25H2. Users can check for eligibility for the update by navigating to Settings > Windows Update. Windows Server 2022 will transition to extended support on October 13, 2026, lasting until October 14, 2031. Microsoft has extended the free Windows 10 Extended Security Updates program for home users until October 2027 and will halt security updates for Windows 11 Home and Pro 23H2 in November 2025.
Winsage
September 12, 2026
Windows 11 KB5124008, released on September 8, has caused various issues, including disruptions to WSL-based applications and Remote Desktop sessions. Users have reported problems with File History backups and instability in Explorer.exe, leading to system and GPU crashes. Microsoft confirmed a bug affecting applications using HCS-managed Linux virtual machines, particularly Claude Cowork, which is experiencing connectivity issues. Remote Desktop Services (RDS) are malfunctioning, leading to connection failures and sign-in problems. Additionally, some users face black screens upon sign-in due to Explorer.exe crashes. Reports indicate that File History is not recognizing external backup drives, and serious GPU issues have been reported on AMD Radeon systems, including driver timeouts and system freezes.
AppWizard
September 10, 2026
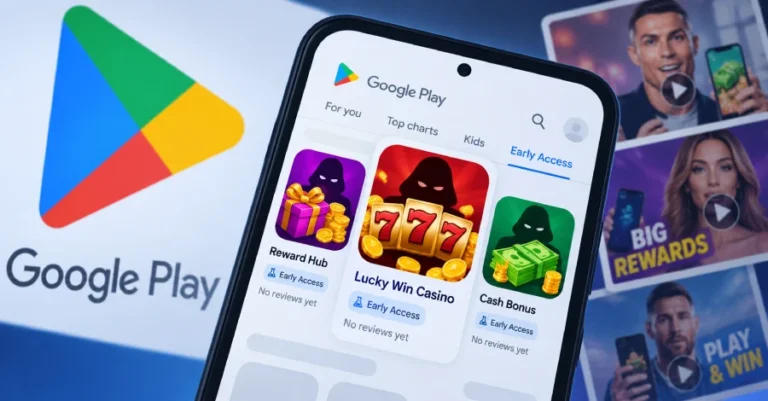
Bad actors are exploiting Google Play's Early Access program to distribute misleading applications that promise money, rewards, and casino winnings. This program allows developers to gather user feedback on unreleased apps but lacks public reviews or star ratings, enabling malicious actors to launch numerous fraudulent applications without immediate scrutiny. An example is the app "Vice Streets: Open World," which mimics Grand Theft Auto, has over 1 million downloads, and recently disappeared from the store without reviews or ratings. These deceptive apps are often promoted on social media with misleading advertisements and promise cash rewards, but users face obstacles when trying to withdraw their earnings. The primary goal of these apps is to generate revenue through excessive advertisements while circumventing regulatory requirements for legitimate gambling apps. Additionally, various malware families targeting Android devices have emerged, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory's use of the Gigabud banking trojan, highlighting ongoing security threats in the digital landscape.
Tech Optimizer
September 8, 2026
Microsoft has acknowledged a software bug causing persistent Windows Security pop-ups that incorrectly indicate antivirus protection is disabled. These notifications began appearing after the latest Microsoft Defender Antivirus updates, but the antivirus is functioning correctly. The issue affects various versions of Windows and Windows Server with the latest Defender updates. Microsoft has committed to resolving the issue in a future update, though no timeline has been provided. Users are advised to verify the status of their antivirus through the Windows Security app and disregard the notifications until a fix is released.
Tech Optimizer
September 4, 2026
Microsoft has acknowledged a software bug in its Windows operating system that causes misleading pop-up notifications, indicating that antivirus protection is disabled. These alerts began appearing after the latest Microsoft Defender Antivirus updates, despite the antivirus functioning correctly. The notifications can occur at startup and intermittently, and cannot be silenced through standard notification controls. The issue affects various versions of Windows and Windows Server with the latest Defender updates. Microsoft is working on a resolution, but no timeline has been provided. Users are advised to verify their antivirus status through the Windows Security app and can ignore the notifications if real-time protection is confirmed as active.
Tech Optimizer
August 27, 2026
A network of fraudulent websites, branded as SysScan, has been discovered, which falsely claims to evaluate antivirus software effectiveness through deceptive security scans. These sites manipulate users into uninstalling legitimate antivirus products and disclosing sensitive personal and banking information. Eleven distinct domains associated with SysScan have been identified, all hosted on a single server. The fraudulent scans generate misleading results based on static findings rather than actual system assessments, and users are coerced into believing their computers are at risk. The scams misrepresent normal browser behaviors as security threats and instruct victims to uninstall their antivirus software, compromising their defenses. The operation targets both individual and business users, collecting extensive personal information and utilizing remote-access tools. The data submitted is sent to Telegram via its bot API. Users are advised to disconnect from the internet and secure their devices if they suspect they have been compromised. Indicators of compromise include specific IP addresses and domains associated with the scam.
Search