server

Winsage
September 19, 2026
Microsoft resolved an issue that caused misleading alerts indicating that Defender Antivirus was disabled after recent updates. This fix was confirmed in an update to the Windows release health dashboard and was implemented in the Microsoft Defender Antivirus update (version 4.18.26080.4) rolled out on September 17. The bug, acknowledged by Microsoft in late August, affected users in the Release Preview Channel of the Windows Insider program since at least June and impacted all supported versions of Windows clients and servers. Users received erroneous notifications in the Windows Security app prompting them to activate Microsoft Defender Antivirus, despite it functioning correctly. Misleading alerts could appear upon Windows startup and intermittently thereafter, even when notification settings were disabled.
AppWizard
September 18, 2026
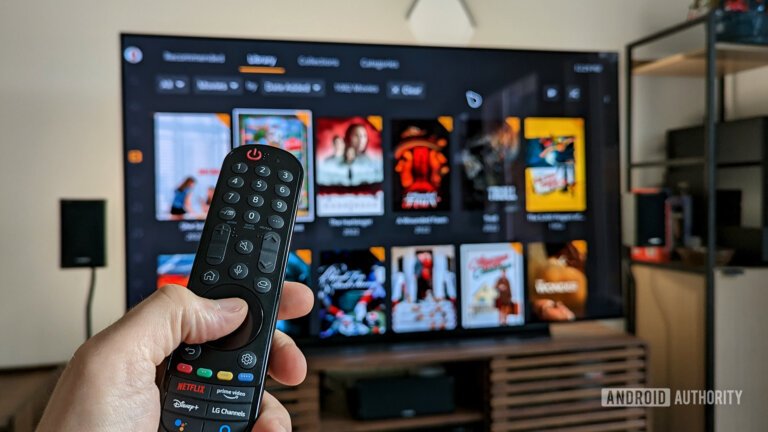
A new open-source Plex client named PlxNative has been developed for older LG TVs running on webOS to improve the browsing experience of Plex libraries. It operates independently of a web browser using a native Rust/OpenGL interface, allowing it to launch in about one second and ensuring fluid scrolling and menu navigation. PlxNative supports various Plex functionalities, including library browsing, profile switching, audio and subtitle selection, and direct play or server transcoding. It does not replace the TV's built-in video decoder and connects directly to the Plex Media Server over the local network after initial sign-in. Installation options include the Homebrew Channel or sideloading via LG’s Developer Mode, which requires periodic session renewals. The developer has submitted PlxNative for official review by LG.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
BetaBeacon
September 18, 2026
- LDPlayer is a general-purpose performance emulator - MEmu is a multi-instance workhorse for players juggling several accounts - GameLoop is Tencent's first-party tool built almost exclusively around its own mobile titles - LDPlayer, MEmu, and GameLoop are all designed around mobile gaming rather than general Android app testing - LDPlayer is actively patching graphics driver bugs, MEmu is quietly polishing quality-of-life features, and GameLoop's update cadence has slowed - GameLoop is specifically tuned for Tencent-published titles like PUBG Mobile - LDPlayer runs two branches, with LDPlayer 14 being the most actively patched version - MEmu's defining feature is multi-instance management for running multiple Android sessions - MEmu's release cadence has been steady in 2026, with the latest build adding a toggle to disable Android system sounds
Winsage
September 17, 2026
Devices operating on Windows 11 24H2 Home and Pro editions will stop receiving updates starting October 13, 2026. The Enterprise and Education editions of Windows 11 24H2 will continue to receive mainstream support until October 2027. Microsoft encourages users to upgrade to Windows 11 25H2, which became available in September 2024. Systems running Windows 11 24H2 Home and Pro that are not managed by IT will automatically upgrade to Windows 11 25H2. Users can check for eligibility for the update by navigating to Settings > Windows Update. Windows Server 2022 will transition to extended support on October 13, 2026, lasting until October 14, 2031. Microsoft has extended the free Windows 10 Extended Security Updates program for home users until October 2027 and will halt security updates for Windows 11 Home and Pro 23H2 in November 2025.
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
Search