Google's September 2026 Pixel Update Bulletin includes patches that affect standard Android platform code, relevant to both Pixel and non-Pixel devices, which have not been included in the regular monthly Android Security Bulletin. GrapheneOS has noted that Android 17 QPR1 introduced new developer APIs not present in the Android Open Source Project (AOSP) for the first time since Android Honeycomb, with one new package and modifications to sixteen others. GrapheneOS is backporting Pixel firmware and drivers from QPR1 onto Android 17 but lacks permissions to distribute this work. Additionally, there has been a delay in Google’s compliance with a GPL source request, with access granted over two weeks after the initial request. Starting in 2027, Google will require all Android app developers to register with them and provide legal identification and signing key evidence, complicating the process of sideloading unverified apps. GrapheneOS and other organizations are advocating for the Keep Android Open campaign against these developments, which may restrict competition and tighten Google's control over the Android ecosystem.
Valve has opened the source code for Lepton, a compatibility layer for running Android games on Linux. Lepton is designed to work with the Steam client and focuses on getting Android games to run seamlessly on the Linux operating system. It is not intended for general Android use, but specifically for launching games. Lepton also offers features to assist game developers in bringing their VR Android games to Steam. Valve's commitment to open-source projects like Lepton benefits the wider Linux gaming community.
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure.
The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions.
GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
- An unofficial Android port of Grand Theft Auto 5 is in development by M0jso of Paralympics Productions.
- The port is being built to run GTA 5 natively on Arm, based on the same foundation as the Switch port.
- Minimum requirements include a Snapdragon 865 processor, 8 GB of RAM, and 65 GB of storage.
- The initial public build will only be compatible with Snapdragon chips.
The Tor Project has launched Tor VPN Beta for Android, allowing mobile applications to route traffic through the Tor network, expanding beyond web browsing. This development was driven by user demand for privacy tools to bypass internet censorship, particularly in restrictive regions. The concept originated in 2021, and after initial testing and user feedback, the beta was announced on September 9.
Tor VPN creates a separate Tor circuit for each application, enhancing privacy by complicating activity correlation across apps. Users can select which applications use Tor, and the interface has been improved for easier management. The beta version 1.4.0 includes support for WebTunnel bridges to disguise Tor connections as standard encrypted traffic.
Usability testing revealed issues with exit-node selection, leading to a design change that requires users to connect to Tor before choosing an exit. Tor VPN is built on the Arti implementation of the Tor protocol and the Onionmasq networking layer, ensuring stability and component sharing. The software supports reproducible builds and is available via F-Droid and APK downloads. A security review in June 2025 found no major flaws but identified some issues being addressed.
Tor VPN is currently in beta and focuses on enhancing circumvention capabilities and usability rather than competing with commercial VPNs on speed. Users in censored areas are advised to configure bridges for access.
Comma Compliance released the source code for its Android capture component on September 10, 2026, allowing corporate IT and security teams to inspect the software that captures employee text messages for compliance archiving. The source code is available on GitHub under the MIT license. The capture mechanism reads messages stored in the phone's default messaging app, encrypts them, and sends them to the customer's Comma backend without intercepting messages in transit. A persistent notification appears on the phone when archiving is active, indicating the organization responsible for the archiving. Comma previously open-sourced its WhatsApp and Signal capture connectors in 2025.
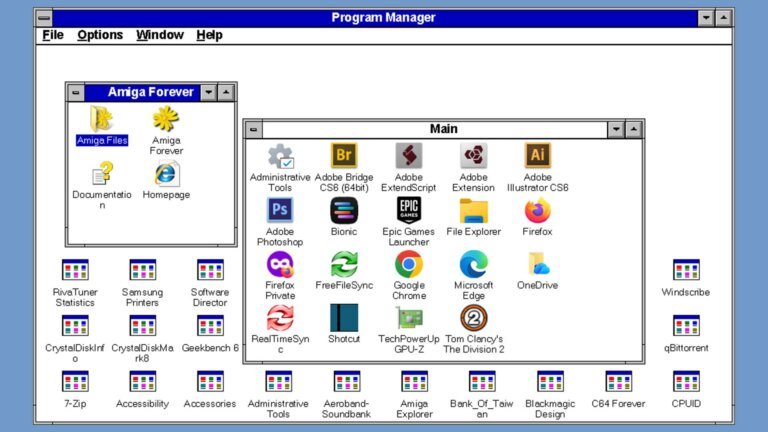
Developer Mayuki has introduced ReProgman, a homage to the classic Windows 3.1 Program Manager ('progman.exe'). The application captures the essence of its predecessor and was created by Claude Code within an hour. The initial version is lightweight, ranging from 12 to 16MB, and requires the .NET SDK 10.0 or higher to build and run. The source code is available on GitHub under the MIT license. Some enthusiasts prefer the authentic experience of running MS-DOS and Windows 3.1 on vintage hardware, with recent demonstrations showing the capability to run Windows 3.1X on modern hardware.
Juggernaut is an upcoming free-to-play boomer shooter inspired by classic Wolfenstein engine first-person shooters, featuring waves of zombies in pixelated arenas. It will be accompanied by the Juggernaut Assets Maker, a paid tool for players to create levels and customize assets. The game is developed by Mages Inc, a Japanese studio known for the Steins;Gate series. The Juggernaut Asset Maker's source code was generated using generative AI, highlighting Mages Inc's transparency in an industry where many games use similar technologies.
Recent investigations have identified the BlueMoon exploit kit, used by espionage-driven threat activity clusters, particularly linked to APT31, a China-aligned state-sponsored group, since August 28, 2026. BlueMoon exploits three vulnerabilities: CVE-2026-85046 (a type confusion vulnerability in Google Chrome's V8 engine), an unassigned V8 sandbox escape, and CVE-2026-85880 (a heap-based buffer overflow in Windows ALPC). Google and Microsoft have released patches for these vulnerabilities, which were exploited as "patch-gap" zero-days.
The attack vectors typically begin with phishing emails that lead victims to malicious URLs, triggering the vulnerabilities for code execution and privilege escalation. Variants of BlueMoon have been detected, featuring modifications for specific campaigns. Notable attack chains include:
- APT31 targeting NGOs and mining firms in the U.S. with a malicious browser add-on called GemStone.
- UNK_LateNight targeting U.S. aerospace companies, deploying BlueMoon alongside the ShadowPad backdoor.
- UNK_DoubleCheck targeting a Vietnamese manufacturer, using DLL sideloading to execute a Rust binary.
- UNK_QuietRacket targeting government and financial organizations in Indonesia and Singapore, modifying BlueMoon to execute a .NET assembly.
CISA added the Chrome flaw to its Known Exploited Vulnerabilities catalog on September 4, 2026, requiring federal agencies to apply patches by September 18, 2026. Indicators of compromise include specific process trees, files, folders, scheduled tasks, mutexes, and registry keys. Proofpoint has released detection rules to help organizations identify and mitigate these threats.