spyware

AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
Tech Optimizer
September 16, 2026
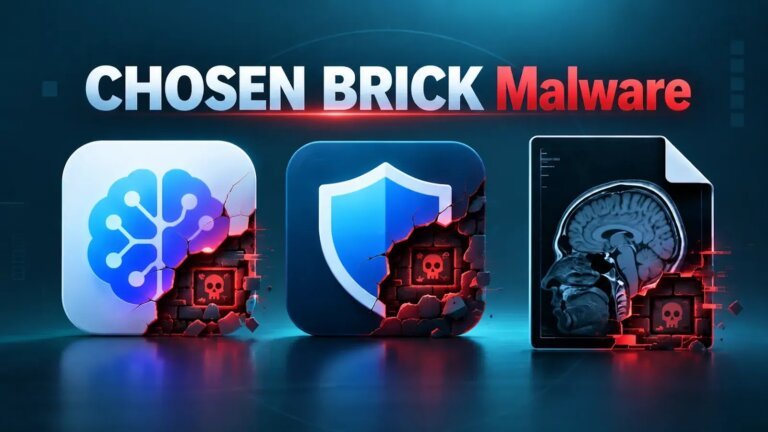
Iranian state-affiliated cyber actors are targeting dissidents, activists, and journalists using fake AI applications, counterfeit antivirus tools, and fabricated MRI scan results, primarily through a spyware family known as CHOSEN BRICK, which is designed for Windows systems. This campaign has been active since at least 2025 and affects individuals globally, including in the UK, US, and Netherlands. The malware establishes persistence via the Windows Registry Run key and communicates through Telegram, utilizing unique Bot IDs for each victim. CHOSEN BRICK is capable of extensive data collection, including capturing screenshots, recording audio, and stealing email content. Personal information from victims has been found on pro-Iranian leak sites, increasing harassment risks. Security measures should include monitoring for suspicious Registry entries and unusual communications, while users are advised to avoid unsolicited software installations and keep their systems updated. The FBI refers to this malware family as HEAVYGRAM.
Tech Optimizer
September 15, 2026
Iranian state-sponsored hackers are targeting dissidents, activists, and journalists using deceptive tactics, including malicious applications that impersonate reputable cybersecurity products like Norton Antivirus and KeePass. The FBI and UK authorities issued a warning about these hackers, who establish rapport with targets via social messaging platforms, posing as IT support or known contacts. They convince victims to download files that appear authentic, including AI video creation applications and other software. The spyware, named “Chosen Brick,” infects Windows PCs and has capabilities such as capturing screen content, recording audio, collecting message data, and downloading additional malware. The hackers have exploited this spyware to publish personal details of victims, increasing their harassment. The FBI advises potential victims on detecting the spyware and recommends enabling antivirus software, running regular scans, and avoiding unofficial downloads.
AppWizard
September 11, 2026
The Cybersecurity and Infrastructure Security Agency (CISA) warned of a critical vulnerability in NetScaler, identified as CVE-2026-19490, with a CVSS score of 9.3, which has been exploited and affects all NetScaler ADC and Gateway appliances. Citrix has patched this vulnerability as of August 19. AdaptHealth reported a data breach affecting over 4.1 million individuals, compromising personal, health, and insurance information, but not Social Security numbers or financial data. A new strain of Android malware, MantaxOtax, attributed to Indonesian threat actors, combines ransomware and spyware, stealing sensitive information and affecting older Android versions. The Gigabud banking trojan has evolved to evade detection by installing a secondary app that hides the malicious application. CISA acting director Nick Andersen emphasized the need for swift adaptation to cybersecurity threats and highlighted staffing improvements within CISA. Russian e-commerce giant Wildberries experienced disruptions from a DDoS attack affecting payments to sellers, following claims of a cyber operation by Ukraine's military intelligence. McKesson faced a cyberattack exposing sensitive data of 6.4 million individuals, with the ShinyHunters group releasing this data after a failed extortion attempt. IDScan confirmed a data breach affecting 150 million individuals, resulting in the theft of personally identifiable information and government-issued documents.
AppWizard
September 10, 2026
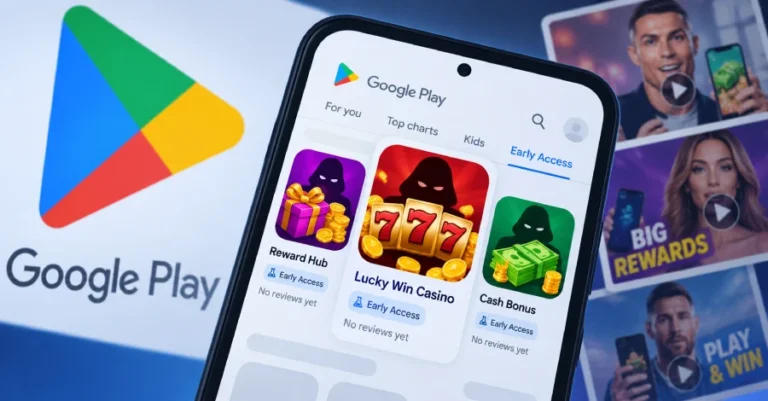
Bad actors are exploiting Google Play's Early Access program to distribute misleading applications that promise money, rewards, and casino winnings. This program allows developers to gather user feedback on unreleased apps but lacks public reviews or star ratings, enabling malicious actors to launch numerous fraudulent applications without immediate scrutiny. An example is the app "Vice Streets: Open World," which mimics Grand Theft Auto, has over 1 million downloads, and recently disappeared from the store without reviews or ratings. These deceptive apps are often promoted on social media with misleading advertisements and promise cash rewards, but users face obstacles when trying to withdraw their earnings. The primary goal of these apps is to generate revenue through excessive advertisements while circumventing regulatory requirements for legitimate gambling apps. Additionally, various malware families targeting Android devices have emerged, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory's use of the Gigabud banking trojan, highlighting ongoing security threats in the digital landscape.
Tech Optimizer
September 7, 2026
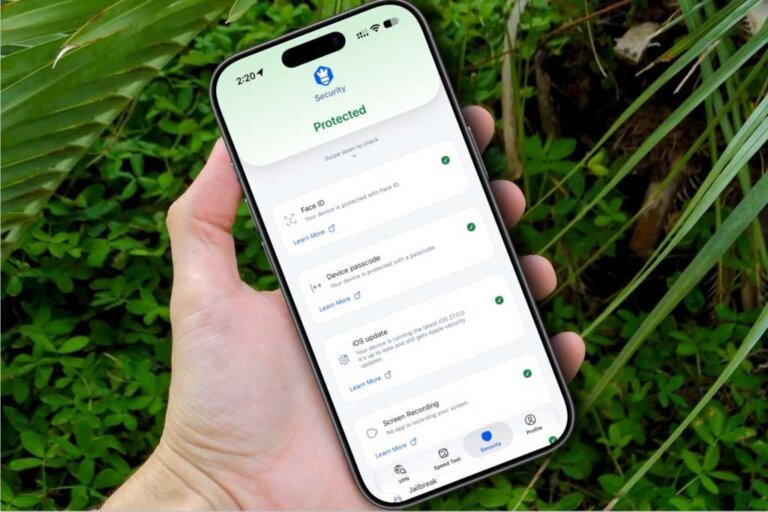
Intego ONE Complete has launched the Intego ONE: VPN & Wi-Fi Security app for iPhone, available at no extra charge to Complete subscribers. The app provides VPN protection, Wi-Fi security assessments, and checks on built-in iPhone security settings but does not function as antivirus software. It enhances existing Apple security measures by addressing vulnerabilities related to insecure Wi-Fi connections and unprotected internet access. The app is accessible to both new and existing subscribers, and Intego is currently offering a 50% discount on subscriptions until September 30, 2026. Intego ONE is available in three tiers: Essential, Advanced, and Complete, with the Complete tier including the new iPhone app. The app features a VPN that encrypts internet connections on public Wi-Fi, Wi-Fi security checks, and assessments of iPhone security settings. While traditional viruses are rare on iPhones, threats like spyware and exploits still exist. The app does not replace Apple's malware protection but complements it. Intego ONE Complete is recommended for Mac and iPhone owners, particularly those who travel frequently or connect to public Wi-Fi. The pricing includes various deals, with a 50% discount currently available and a subsequent 35% discount after the promotional period.
Tech Optimizer
August 27, 2026
ESET NOD32 Antivirus is an antivirus solution designed to protect Windows PCs from various threats, including viruses, spyware, rootkits, and zero-day exploits, while maintaining system performance. It offers a one-year license for a competitive price and is recognized for its effective threat detection and minimal impact on system resources. Key features include real-time scanning, a Ransomware Shield that blocks file-locking attempts, advanced artificial intelligence for identifying new threats, and an anti-phishing feature that prevents access to fraudulent websites.
AppWizard
August 26, 2026
Android Pulse is a diagnostic tool distributed by Google since March, which has recently become visible to the public and is now on over 10 million devices. It operates without a user interface and monitors software for unusual system resource consumption. The app first appeared in March with seven builds before being listed in the Play Store. On Pixel devices, it is found in system settings, while on others, it appears as a blank square in the update queue. There was no formal announcement regarding its rollout. Europe has enacted regulations to enhance user control over devices, but essential system applications like Android Pulse are exempt from easy uninstallation. There is no evidence that Android Pulse poses a danger, but its late visibility raised user concerns.
Search