Target

AppWizard
September 24, 2026
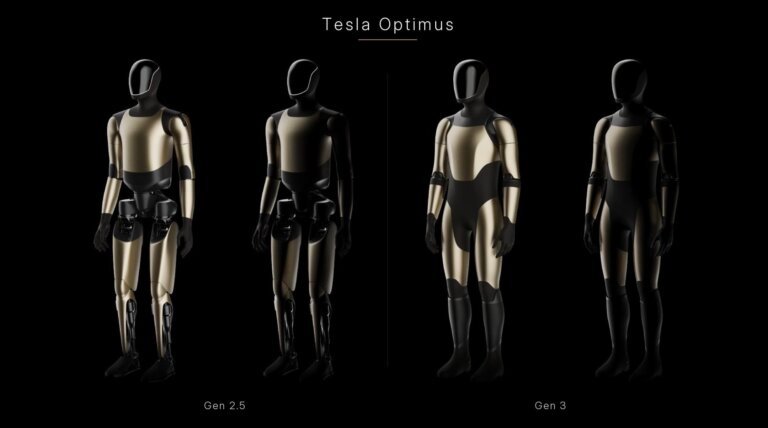
Tesla's next-generation Optimus humanoid robot, referred to as Optimus Gen 3, has been previewed through new 3D design assets found in the Android version of Tesla’s mobile app. These assets, which include renders labeled “gen3” and images comparing Optimus Gen 2.5 and Gen 3, indicate significant design changes. The robot features a cleaner aesthetic with enclosed joints, a unified torso shell, thicker forearms, slimmer wrists, and redesigned legs that resemble integrated boots. The assets began appearing in app builds around August 27, 2026, with higher-resolution versions on September 5. Tesla initially planned to unveil Optimus Gen 3 by the end of Q1 2026, but this timeline was missed. Elon Musk later indicated that the reveal was postponed to mid-year for strategic reasons. Tesla has also started auditing suppliers in China for Gen 3 production, suggesting a potential reveal is approaching.
Tech Optimizer
September 23, 2026
A new tool named BigDiskBuster has been released on GitHub, which disrupts Microsoft Defender Antivirus by preventing it from installing updates. It does this by consuming available disk space during the update process, causing Defender to remain on its current version and unable to receive new platform or signature updates. BigDiskBuster operates as a local denial-of-service technique and requires prior access to the target machine to execute. The tool was created by researcher Abdelhamid Naceri, known as Nightmare Eclipse, who has previously worked on similar projects. As of now, there is no CVE identifier, patch, or advisory from Microsoft regarding this issue.
Tech Optimizer
September 22, 2026
LastPass has identified a sophisticated scheme targeting users of its Authenticator app, involving SEO poisoning and deceptive GitHub pages that distribute malicious ZIP files disguised as legitimate software. Users searching for "LastPass Authenticator download" may encounter these counterfeit pages, which redirect them to a malicious server delivering a ZIP file containing vsdbg.exe and vsdbg.dll. The executable is a legitimate Microsoft debugging tool exploited to execute the malicious DLL through DLL sideloading, allowing the malware to run undetected. Named Rapuncel by security researchers from Delphos, this malware is undetectable by antivirus engines and targets a hardcoded list of 145 antivirus and endpoint security products, disabling them upon detection. Rapuncel harvests sensitive information, including saved passwords from over 25 web browsers, cryptocurrency wallet files from more than 30 applications, and session tokens from platforms like Discord and Steam. It also captures screenshots and compiles a profile of the infected system, uploading the stolen data to an attacker-controlled server. The malware includes a kernel driver that intercepts web traffic, allowing for advertisement injection and search result manipulation. This campaign has been active for several months, with LastPass vaults remaining unaffected. Users are advised to download applications only from trusted sources. Rapuncel establishes persistence on infected machines by installing itself as a Windows service that starts with the system and terminates activated security products. Removing the kernel driver requires booting into Safe Mode or using external recovery tools, as standard Windows utilities cannot eliminate software operating at that level.
Winsage
September 21, 2026
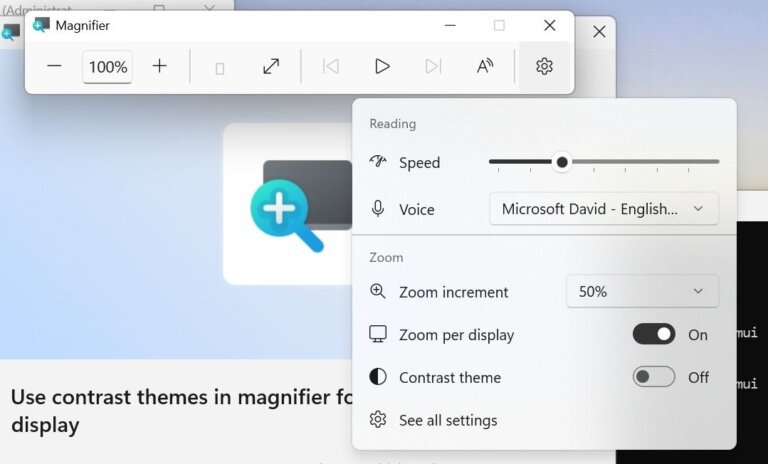
Windows 11 is set to enhance its accessibility features, particularly with the Magnifier tool, introducing a new contrast theme that reduces glare without altering the colors of photos, videos, and charts. Users can activate this feature via the Magnifier toolbar and customize their preferences in the Accessibility settings. The Cloud rebuild feature will allow users to restore their PC to a clean state with options to sanitize drives during the process. IT administrators can also initiate a Cloud rebuild remotely. Live Captions will receive an update to include a setting that excludes audio from screen readers. Issues with Hyper-V related to sharing host folders with Linux VMs have been resolved. Additionally, a problem with File History backups failing has been fixed. Many of these updates have already been released to Insiders in the Beta Channel, and changes regarding Cloud rebuild are active in the Experimental Channel.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
Search