Vigilance

Tech Optimizer
September 21, 2026
More than 5,400 websites across over 2,200 organizations have been compromised to propagate malware, primarily affecting small businesses like clinics and online retailers. The attack mechanism involves malicious code that triggers a deceptive CAPTCHA, instructing users to execute commands that can download malware. Attackers are using the BNB Smart Chain test network to store instructions, making it harder for investigators to shut down operations. A newer variant of the attack uses WebRTC technology to establish encrypted connections for delivering additional malicious code. To protect against these threats, users should avoid pasting commands from websites, be suspicious of unusual CAPTCHA instructions, use strong antivirus protection, keep systems updated, take action if commands are executed, and small business owners should regularly verify their website's integrity.
AppWizard
September 10, 2026
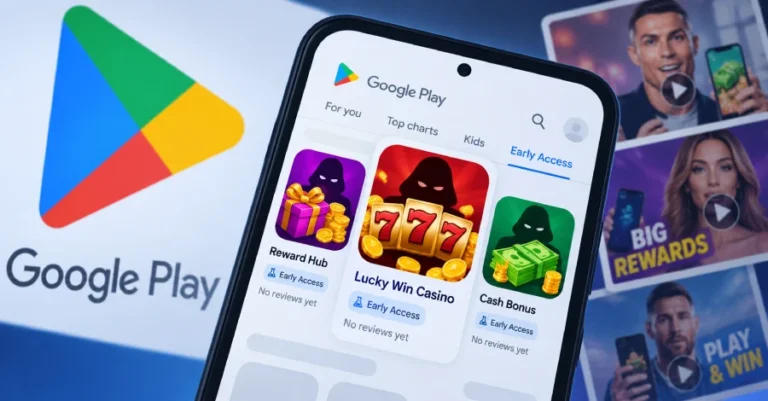
Bad actors are exploiting Google Play's Early Access program to distribute misleading applications that promise money, rewards, and casino winnings. This program allows developers to gather user feedback on unreleased apps but lacks public reviews or star ratings, enabling malicious actors to launch numerous fraudulent applications without immediate scrutiny. An example is the app "Vice Streets: Open World," which mimics Grand Theft Auto, has over 1 million downloads, and recently disappeared from the store without reviews or ratings. These deceptive apps are often promoted on social media with misleading advertisements and promise cash rewards, but users face obstacles when trying to withdraw their earnings. The primary goal of these apps is to generate revenue through excessive advertisements while circumventing regulatory requirements for legitimate gambling apps. Additionally, various malware families targeting Android devices have emerged, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory's use of the Gigabud banking trojan, highlighting ongoing security threats in the digital landscape.
Tech Optimizer
September 7, 2026
Endpoint detection and response (EDR) continuously records process, file, registry, and network activity on endpoints, applying behavioral analytics to identify attacker techniques while providing tools for investigation and containment. Several EDR platforms have emerged, each catering to different organizational needs: 1. CrowdStrike: Best overall for its rich telemetry and elite threat intelligence. 2. SentinelOne: Best for autonomous response, featuring strong containment and rollback capabilities. 3. Microsoft Defender for Endpoint: Best value for organizations already using Microsoft 365 E5. 4. Palo Alto Cortex XDR: Best for native data fusion across endpoint, network, and cloud telemetry. 5. Sophos: Best for generalist IT teams due to its user-friendly interface. 6. Trend Micro: Best for server and workload coverage, focusing on cloud and hybrid environments. 7. Bitdefender: Best mid-market value with strong detection capabilities at an accessible price. 8. Trellix: Best for organizations already using Trellix products, offering integrated solutions. 9. Huntress Managed EDR: Best for managed endpoint security, ideal for teams lacking full staffing. 10. Cisco Secure Endpoint: Best for Cisco environments, integrating well with Cisco security solutions. Key differentiators among these platforms include the analyst burden, alert management efficiency, and the impact of retention policies on investigation quality. The evaluation of EDR solutions should consider detection depth, response capabilities, operational costs, and the specific needs of the organization.
Tech Optimizer
September 1, 2026
Home Wi-Fi connects various devices and presents security risks, making firewalls important for network protection. A router firewall is built into the home router and protects all connected devices, while a software firewall operates on individual devices for additional security. Inbound traffic is data coming to a device, while outbound traffic is data leaving it; firewalls analyze this traffic to manage connections. Network security is critical as sensitive information is often accessed on devices used for leisure, and remote work increases data overlap. Firewalls can control network connections and filter unwanted traffic but cannot replace weak passwords or antivirus protection. To enhance home network security, users should secure router settings, keep routers updated, strengthen Wi-Fi access, check connected devices, and replace outdated routers. A comprehensive security strategy includes keeping software updated, using multifactor authentication, being cautious with links, and strengthening firewalls with antivirus protection. Protecting valuable data is essential, and understanding ransomware risks is crucial. The 3-2-1 backup strategy involves maintaining three copies of data on two different storage types, with one copy offsite. Regularly testing backups and knowing how to respond to ransomware incidents are also important.
Tech Optimizer
September 1, 2026
NordVPN's next-generation antivirus achieved a 94% detection rate for phishing threats in an evaluation by AV-Comparatives, tested against 250 active phishing URLs and recording zero false positives. The antivirus also demonstrated a 92% block rate in similar independent testing and ranked third overall in speed and malware protection behind Avast and Norton. It is included in NordVPN's Complete subscription tier and operates alongside the standard VPN tunnel to block trackers, ads, and malicious sites in real-time. Users are advised to maintain vigilance and practice strong digital hygiene, including scrutinizing URLs and enabling two-factor authentication for added security.
Tech Optimizer
August 31, 2026
A fake Chrome update scam has emerged, linked to a Chrome extension called Enable Right Click & Copy - Smart Unlock + OCR, which was initially legitimate but later compromised. The extension had around 70,000 users before being removed from the Chrome Web Store on August 14 due to its malicious nature. Users may encounter deceptive warnings while browsing benign sites, urging them to download files instead of using Chrome's built-in update mechanism. Google advises against engaging with suspicious pop-ups requesting software installations. The scam highlights that trusted extensions can become threats without warning, and users should regularly review their installed extensions and check for updates directly within Chrome. Similar fake update alerts have also been reported in other Chromium-based browsers. Users are encouraged to adopt safety measures, such as using strong antivirus software, reviewing browser extensions, and being cautious with downloaded files. If a suspicious file has been executed, users should treat their computer as potentially compromised and take appropriate security actions.
Tech Optimizer
August 16, 2026
The relevance of third-party antivirus software for mobile devices has declined as modern Android devices come with robust built-in security features. Google Play Protect blocks millions of harmful apps and conducts regular scans of installed apps. Android employs sandboxing technology to isolate applications, has a proactive permissions system, and provides regular security updates. While Android is not immune to malware, many threats now arise from social engineering tactics rather than technical vulnerabilities. Users face risks when connecting to public Wi-Fi networks, and malicious push notifications can mislead them. Third-party antivirus may be beneficial for users who sideload apps or notice signs of infection, but for most users, Google's Play Protect suffices. Older devices lacking updates are at higher risk, and while antivirus apps can provide additional protection, education and user vigilance are crucial for minimizing risk.
Winsage
August 16, 2026
- The August Patch Tuesday release included 421 vulnerabilities, with 236 affecting Windows, highlighting CVE-2026-68820, a critical use-after-free vulnerability that allows privilege escalation to SYSTEM level without user interaction. - CISA added CVE-2026-68820 to its Known Exploited Vulnerabilities Catalog, confirming its active exploitation. - AMD's Ryzen Master software has vulnerabilities, including CVE-2025-54512 (DLL hijacking) and CVE-2026-0465 (use-after-free), which could allow code execution with elevated privileges. - AMD's advisory on CVE-2026-6726 and CVE-2026-6727 indicates vulnerabilities in the TPM 2.0 reference code affecting Ryzen platforms, leading to potential information disclosure. - Intel's advisories included updates for microcode, Wi-Fi software, and NPU drivers, with CVE-2026-20760 addressing privilege escalation risks. - Google’s Chrome update on August 11 fixed five high-severity vulnerabilities, including use-after-free flaws. - Gunra malware has evolved into a ransomware-as-a-service model using a double-extortion strategy. - WindRelay malware combines SpyNote RAT with an NFC relay component, allowing attackers to relay NFC communication between a victim's bank card and a remote device. - The findings emphasize the need to view vulnerabilities as part of potential attack chains, highlighting the complexity of modern cybersecurity threats.
Search