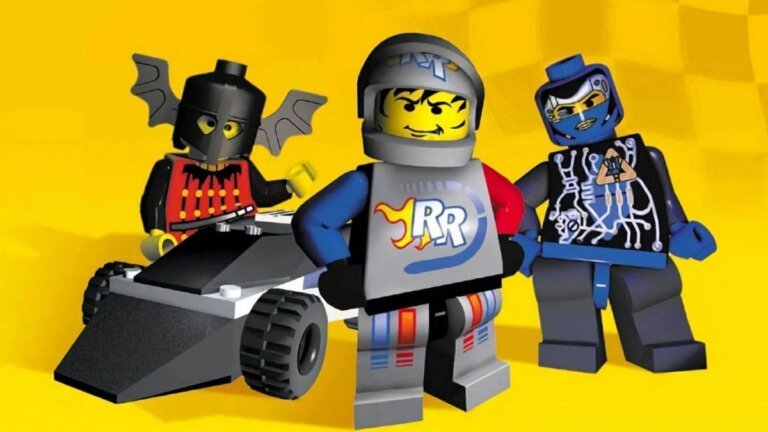
Lego Racers has been reintroduced as "Step On It," a free online game accessible through web browsers. This remake retains the original's essence while adding features like online multiplayer for up to six players. All content from the original game is available from the start, and enhancements such as rebalanced items and adjusted AI can be toggled. The project was developed by isledecomp, known for the Lego Island browser remake.
Ocean Browser is an Android application that provides a secure and private browsing experience by integrating advanced proxy technology, eliminating the need for separate VPN applications. It reroutes browsing traffic through its secure infrastructure, hiding users' actual IP addresses from websites. Ocean Browser offers features such as encrypted proxy connections, the ability to select proxy locations, and seamless management of proxy connections without complex settings. It is designed for everyday use, particularly on public Wi-Fi networks, and is available for free on Google Play.
LastPass has identified a sophisticated scheme targeting users of its Authenticator app, involving SEO poisoning and deceptive GitHub pages that distribute malicious ZIP files disguised as legitimate software. Users searching for "LastPass Authenticator download" may encounter these counterfeit pages, which redirect them to a malicious server delivering a ZIP file containing vsdbg.exe and vsdbg.dll. The executable is a legitimate Microsoft debugging tool exploited to execute the malicious DLL through DLL sideloading, allowing the malware to run undetected.
Named Rapuncel by security researchers from Delphos, this malware is undetectable by antivirus engines and targets a hardcoded list of 145 antivirus and endpoint security products, disabling them upon detection. Rapuncel harvests sensitive information, including saved passwords from over 25 web browsers, cryptocurrency wallet files from more than 30 applications, and session tokens from platforms like Discord and Steam. It also captures screenshots and compiles a profile of the infected system, uploading the stolen data to an attacker-controlled server. The malware includes a kernel driver that intercepts web traffic, allowing for advertisement injection and search result manipulation.
This campaign has been active for several months, with LastPass vaults remaining unaffected. Users are advised to download applications only from trusted sources. Rapuncel establishes persistence on infected machines by installing itself as a Windows service that starts with the system and terminates activated security products. Removing the kernel driver requires booting into Safe Mode or using external recovery tools, as standard Windows utilities cannot eliminate software operating at that level.
The landscape of computer security has changed significantly over the past two decades. In 2026, antivirus protection remains important, but the need for separate third-party programs has decreased for many users due to the built-in Microsoft Defender in Windows 11, which is activated by default and effectively blocks 100% of common malware samples according to independent testing by AV-TEST. Windows 11 also includes additional protective features like SmartScreen and a robust Firewall. While dedicated security suites from companies like Norton and Bitdefender offer advanced functionalities, many users may find adequate protection with the built-in tools. Research from AV-Comparatives indicates that performance varies among security programs, particularly against real-world attacks. Phishing attacks accounted for approximately 60% of initial access points in incidents examined by the ENISA Threat Landscape report from 2025, highlighting that user behavior is a significant vulnerability. Modern web browsers and operating systems have enhanced their security measures, with Google Chrome, Microsoft Edge, macOS, and Android incorporating features to protect users from harmful websites and downloads. For the average Windows 11 user who keeps their system updated and practices safe browsing, built-in protection is generally sufficient, though paid antivirus options can provide additional tools.
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.
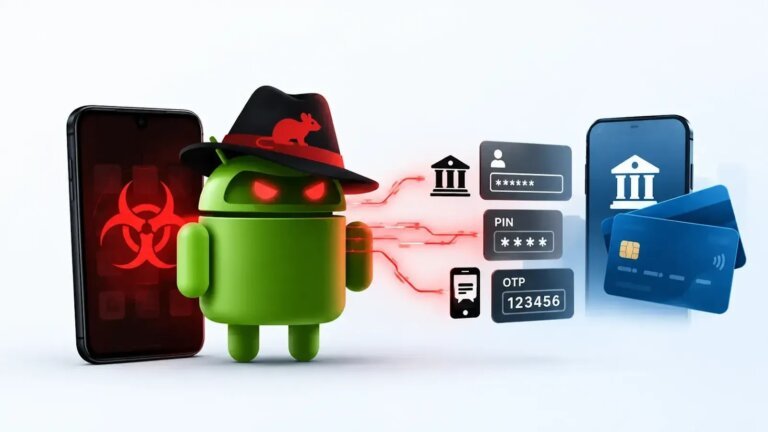
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox.
The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception.
Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client.
The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
In a survey by Android Authority with nearly 1,500 participants, Google Chrome was the most preferred web browser for Android, receiving 32.1% of the votes. Brave followed with 27.2%, while Firefox secured 17.5%. The Samsung Browser came in fourth with 6.4%, Vivaldi at 4.8%, and Microsoft Edge at 4.2%. A Firefox fork received 2.6%, surpassing a lesser-known Chromium-based browser at 2.2%.
Iranian state-sponsored hackers are targeting dissidents, activists, and journalists using deceptive tactics, including malicious applications that impersonate reputable cybersecurity products like Norton Antivirus and KeePass. The FBI and UK authorities issued a warning about these hackers, who establish rapport with targets via social messaging platforms, posing as IT support or known contacts. They convince victims to download files that appear authentic, including AI video creation applications and other software. The spyware, named “Chosen Brick,” infects Windows PCs and has capabilities such as capturing screen content, recording audio, collecting message data, and downloading additional malware. The hackers have exploited this spyware to publish personal details of victims, increasing their harassment. The FBI advises potential victims on detecting the spyware and recommends enabling antivirus software, running regular scans, and avoiding unofficial downloads.
Iranian state cyber actors are targeting individuals through popular messaging applications, using surveillance and data-stealing malware known as "Chosen Brick," which has been in use since at least 2025. This malware is designed for Windows systems and enables the theft of personal data, allowing Iranian spies to monitor perceived threats such as dissidents, activists, and journalists. The attacks typically begin with messages sent via WhatsApp or Telegram, impersonating trusted contacts. Attackers conduct extensive research on their targets to craft convincing messages that encourage victims to download malicious files disguised as legitimate applications.
Once executed, Chosen Brick operates stealthily, evading detection and establishing a connection for command-and-control communications. It can enumerate processes, capture screen and audio content, extract sensitive information, and even wipe infected systems. Organizations suspecting compromise are advised to engage IT providers for investigations and to inform staff about potential risks. Recent alerts follow cyberattacks on water and energy sectors linked to Iran, with ongoing concerns about the implications for cybersecurity amid escalating military tensions. Additionally, five US agencies have reported that attackers are using AI-generated scripts to exploit vulnerabilities in critical infrastructure systems.