Google has introduced a feature that allows users to run privately created, AI-built Android applications on their smartphones via Google Play without public publication. This enables users to launch their apps using standard Google accounts while keeping them private, as these apps will not appear in Google Play search results or listings. The feature is available to users aged 18 and older in the United States, provided the apps comply with Google Play policies. Users can create apps using Google AI Studio through a process called “vibe coding.” Google plans to allow users to share their AI-built applications with trusted friends in the future and offers the possibility of transitioning popular personal apps into publicly published ones after passing trust and safety reviews. Additionally, Google is developing AI-driven tools to enhance the Google Play experience, including a personalized game recommendation engine called Game Finder, which will be available in English in the U.S. Users can curate game lists, engage in community discussions, and participate in gaming challenges. The Play Store's AI assistant, Ask Play, will receive updates for better app comparisons, and a new age-range feature will help developers create age-appropriate experiences for children.
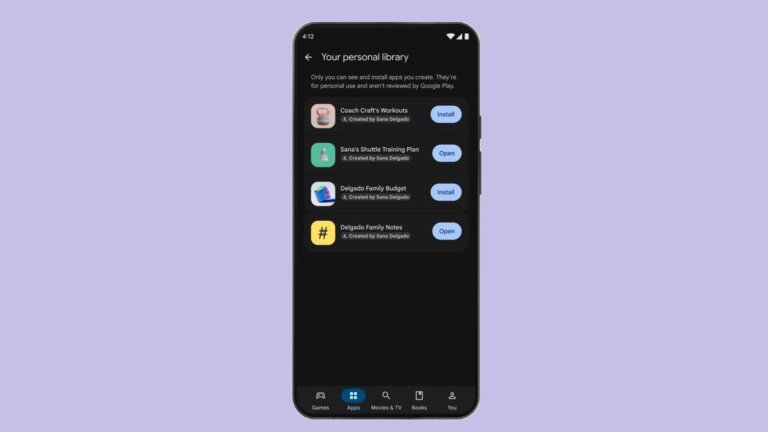
Google AI Studio is introducing tools for sharing personal software through a private section of the Play Store called "Your personal library," which does not require a developer account. This feature is currently available to U.S. users over 18 and allows them to upload or download their creations using standard login credentials. Users can initially share their vibe-coded software with a close circle of friends and family for testing purposes. Google plans to roll out this sharing feature in the coming months. Additionally, upgrades to the AI-powered Ask Play feature now allow users to compare applications, and enhancements to the Play Family Link service enable parents to set age ranges for their children's app access.
Researchers have identified a new Android malware called Hirudo, which steals bank account credentials by replacing legitimate banking applications with modified versions that disable security checks. Hirudo impersonates at least seven banks in Indonesia and targets financial institutions in China, India, Mexico, Morocco, and Thailand. It is delivered through seemingly legitimate applications related to shopping, adult content, or short drama, which prompt users to grant permissions, including Accessibility services.
Once installed, Hirudo uninstalls the genuine banking app, downloads a patched version, and uses Accessibility permissions to complete the installation. The malicious app retains nearly all of the original app's code but integrates a hooking engine based on open-source frameworks YAHFA and Dobby, employing evasion tactics such as substituting signing certificates, concealing Accessibility services, disabling screenshot protection, and altering key-attestation certificates.
Despite its advanced capabilities, Hirudo has limitations, including a publicly leaked attestation keybox and compromised certificates flagged by Google. Once operational, it can extract sensitive information, stream the screen, access cameras, and use fake checkout pages to collect payment PINs while misleading victims with fabricated success messages.
Hirudo represents an escalation in Android banking malware tactics, focusing on the security mechanisms of banking applications. Researchers recommend that banks enhance security measures and that Android users keep devices updated, avoid unofficial APK files, and conduct regular Play Protect scans.
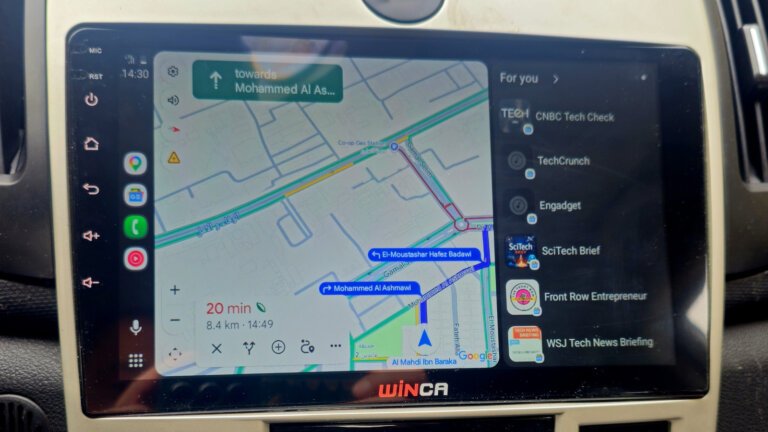
Users have reported that the speedometer feature in Google Maps on Android Auto has been disappearing unexpectedly, but this is believed to be a temporary bug. To restore the speedometer, users should set a destination in Google Maps and tap 'Start.' If the speedometer does not reappear, users should check if the feature is enabled in the Settings menu under 'Navigation' and the Speedometer toggle. The feature may not be available in all regions, and if it fails to display consistently, a complete reset of the Android Auto setup may be necessary. Google has acknowledged the issue and is investigating it, while also rolling out features like current speed and speed limits, which may lead to inconsistent availability.
Cybersecurity experts from Bitdefender have found that budget Android smartphones, such as the Doogee S200 X, Doogee Fire 3 Max, and Cubot KINGKONG X, may come pre-loaded with malware embedded in their firmware, posing significant security risks. This malware is introduced during the manufacturing process, particularly affecting devices with MediaTek chipsets. Thousands of users in around 150 countries, including Mexico, France, Italy, the United States, Germany, Brazil, and Spain, have been impacted. Bitdefender identified a network of 32 malicious applications disguised as legitimate utilities that generate fraudulent ad impressions. Some infected phones can function as residential proxies for criminal activities, including spam campaigns and DDoS attacks. Uninstalling the malicious app may not eliminate the infection if it is integrated into the system software, potentially requiring firmware-level remediation. Buyers of budget phones should research manufacturers' supply chain control and commitment to security updates.
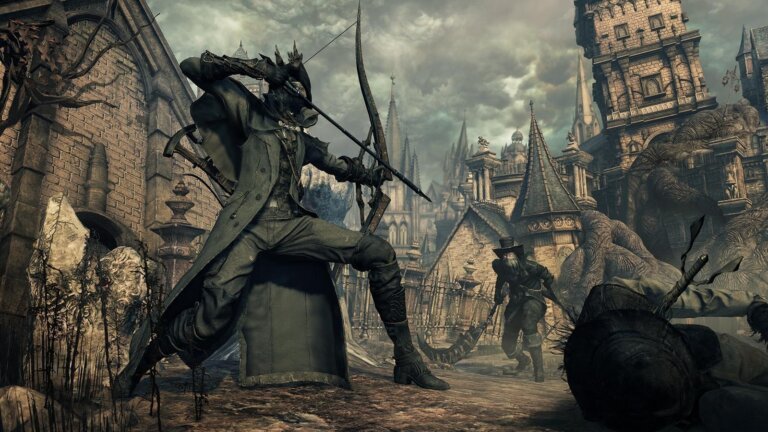
Bloodborne, a cult PS4 exclusive, has been ported to Android smartphones by a developer named ducvd89. The game has been tested on different devices and achieved around 34-35 FPS in Central Yharnam. The developer plans to continue improving the port, which already supports touch controls, gamepads, mods, and frame generation via Lossless Scaling.
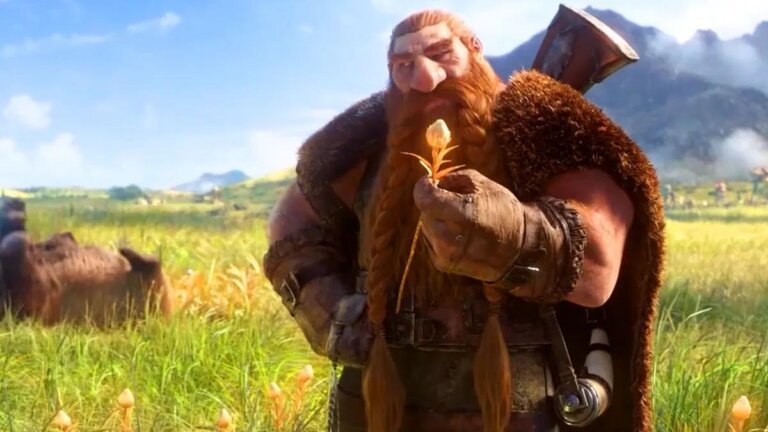
- An enthusiast named jaredgei has created an unofficial launcher called WoW Forever for Android.
- The launcher allows users to play the beta version of World of Warcraft: Forever on their smartphones and portable consoles running Android.
- The game runs smoothly on devices with Snapdragon 8 Gen 2 and Snapdragon 8 Elite Gen 5 processors.
- In less crowded areas, the game achieves 60 FPS, dropping to around 40 FPS in bustling cities.
- The launcher supports touch controls, gamepads, and direct updates on the device.
- Users need Android 10 or newer, a Snapdragon 8-series processor with Adreno 7xx or 8xx graphics, and a Battle.net account with access to the beta testing, which ends on October 21.
The Pocket Casts app is now available for download on Android TV and Google TV devices, following its debut on Apple TV. This native app is designed for television screens and allows users to pair it with their existing accounts using a QR code, synchronizing all podcast subscriptions, playlists, and account data. It features a "Made for TV" section for video podcasts and maintains a similar interface to its Apple TV version. Users can continue audio playback while minimizing the app and easily access upcoming podcasts. Some users may face difficulties searching for the app directly on their devices, but it can be downloaded via a web browser on the Play Store.
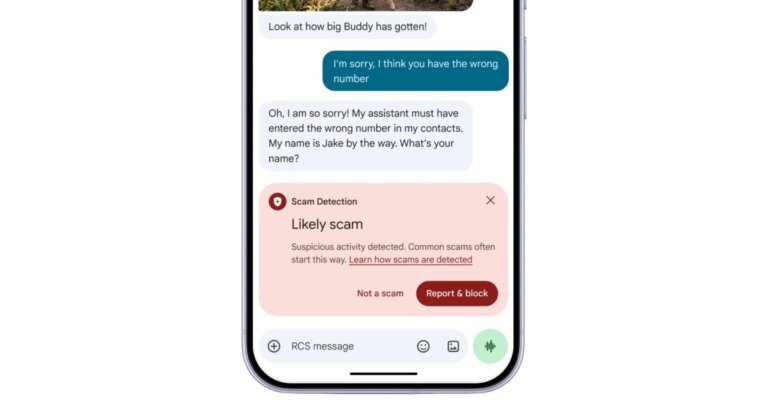
Google has introduced new features to enhance user security on its Android platform during Cybersecurity Awareness Month, focusing on combating messaging and phone scams. The key feature is an enhanced protection mode for the Google Messages app, which includes Scam Detection using Private AI Compute to analyze message context and identify scammer intent through cloud-based Gemini models. This mode complements existing on-device detection and aims to uncover sophisticated scams while ensuring user data remains encrypted and secure.
Additionally, link protections have been upgraded with real-time web signals to assess unfamiliar links' trustworthiness, available on select devices such as Pixel 10+, Samsung Galaxy S26 series, Galaxy Z Flip 8, and Z Fold 8. Redesigned warnings will provide clearer context before users tap links from unknown numbers, previously limited to select countries or devices with Android Advanced Protection.
Google is also expanding its on-device Scam Detection to more brands beyond Pixel, including HONOR, Infinix, iQOO, itel, JOVI, Motorola, OPPO, OnePlus, realme, TECNO, vivo, and Xiaomi. For phone scams, automatic screen-share privacy will conceal sensitive information in native apps and extend to Chrome and WebView on devices running Android 15 and above. Google plans to block apps from enabling call forwarding in the background to prevent one-time passcode theft, with this feature rolling out in early December on Pixel and select other devices. Android will also proactively warn users if a scammer attempts to trick them into entering an MMI forwarding code.