application

AppWizard
September 18, 2026
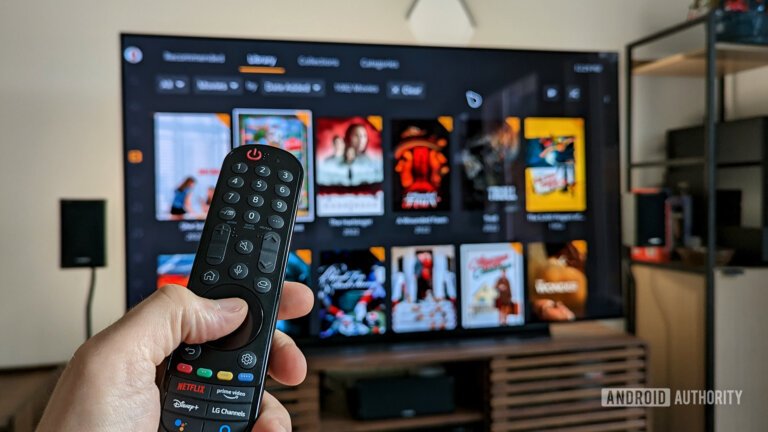
A new open-source Plex client named PlxNative has been developed for older LG TVs running on webOS to improve the browsing experience of Plex libraries. It operates independently of a web browser using a native Rust/OpenGL interface, allowing it to launch in about one second and ensuring fluid scrolling and menu navigation. PlxNative supports various Plex functionalities, including library browsing, profile switching, audio and subtitle selection, and direct play or server transcoding. It does not replace the TV's built-in video decoder and connects directly to the Plex Media Server over the local network after initial sign-in. Installation options include the Homebrew Channel or sideloading via LG’s Developer Mode, which requires periodic session renewals. The developer has submitted PlxNative for official review by LG.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
Winsage
September 17, 2026
Tali Roth, overseeing Windows core user experience, revealed that Windows 11 did not inherit significant portions of the legacy Win32 code, particularly affecting the taskbar's customization and repositioning features. Microsoft had to rebuild the taskbar from scratch, which complicated the ability to allow users to move it, as each application would need to adapt to such changes. Initially, the demand for a movable taskbar was low, but user feedback prompted Microsoft to reconsider. Similarly, the Start menu in Windows 11 offered fewer customization options compared to Windows 10 due to a design shift towards a minimalist aesthetic, making it difficult to reintegrate previous features. Microsoft is balancing user feedback with its design vision as it evolves the Windows experience.
AppWizard
September 17, 2026
The Messenger-Inquirer is launching a mobile application to enhance reader experience by providing access to its content. The app will feature comprehensive content access, a user-friendly interface, real-time notifications for breaking news, and a personalized news feed option.
Winsage
September 17, 2026
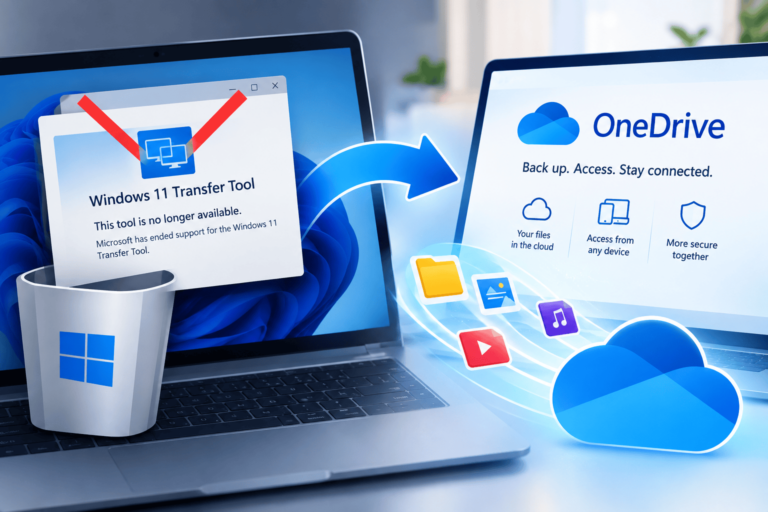
Microsoft has announced the discontinuation of Windows 11’s PC-to-PC migration tool, which was designed for direct file transfers over local Wi-Fi or LAN connections. This tool, integrated into the Windows Backup application, allowed users to connect two computers using a one-time code to transfer specific files and folders without requiring cloud storage. Users are now directed to use Windows Backup, which relies on OneDrive for file synchronization and restoration, posing challenges for those with limited OneDrive capacity. The former tool also allowed the transfer of certain Windows settings but did not include installed applications, saved passwords, or sign-in credentials. Microsoft has updated its support documentation to confirm that the PC-to-PC Migration feature is no longer available.
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
Tech Optimizer
September 16, 2026
Iranian state-affiliated cyber actors are targeting dissidents, activists, and journalists using fake AI applications, counterfeit antivirus tools, and fabricated MRI scan results, primarily through a spyware family known as CHOSEN BRICK, which is designed for Windows systems. This campaign has been active since at least 2025 and affects individuals globally, including in the UK, US, and Netherlands. The malware establishes persistence via the Windows Registry Run key and communicates through Telegram, utilizing unique Bot IDs for each victim. CHOSEN BRICK is capable of extensive data collection, including capturing screenshots, recording audio, and stealing email content. Personal information from victims has been found on pro-Iranian leak sites, increasing harassment risks. Security measures should include monitoring for suspicious Registry entries and unusual communications, while users are advised to avoid unsolicited software installations and keep their systems updated. The FBI refers to this malware family as HEAVYGRAM.
Search