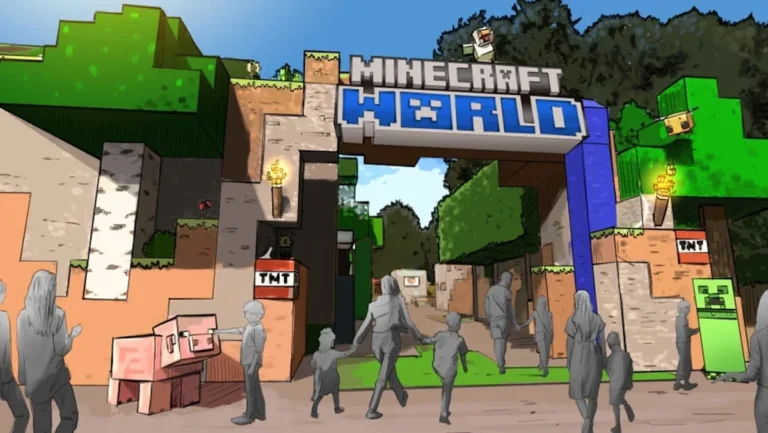
Merlin Entertainments and Mojang Studios are collaborating to create the first-ever Minecraft theme park, named Minecraft World, which will open in 2027 at Chessington World of Adventures. The project has a budget of £50 million and will feature a roller coaster that takes guests on a minecart journey through the Nether. The park will include interactive adventures, themed dining experiences, and block-built playscapes, as well as merchandise stores. The developers are working closely with Minecraft creators to ensure authenticity. Minecraft World is located 35 minutes by train from London Waterloo.
Two newly identified Critical CVEs have expanded Microsoft's September identity infrastructure vulnerabilities to over ten verified weaknesses across more than ten distinct services. The Azure Database for PostgreSQL is vulnerable to CVE-2026-85878, an Improper Authorization flaw (CWE-285) with a CVSS score of 9.9. Azure Billing is impacted by CVE-2026-62874, which presents an Insufficient Data Authenticity Verification issue (CWE-345) with a CVSS score of 10.0. Both vulnerabilities were disclosed on September 18 and validated by Tenable and MITRE. CVE-2026-85878 allows an authorized attacker to elevate privileges over the network with minimal complexity, while CVE-2026-62874 requires no authentication, enabling unauthenticated attackers to jeopardize financial integrity. The vulnerability cluster first emerged during the Patch Tuesday cycles on September 3 and September 8, with initial reports highlighting critical flaws in core services. Other September disclosures include CVE-2026-83711 (Azure AD B2C, CVSS 10.0), CVE-2026-70352 (Azure AI Language, CVSS 10.0), CVE-2026-83941 (Entra ID, CVSS 9.9), CVE-2026-62916 (Entra ID, CVSS 9.1), CVE-2026-69857 (Azure Cosmos DB, CVSS 8.5), and CVE-2026-69854 (Spring Cloud Azure, CVSS 9.0). Activity heightened between September 17 and 18 with the introduction of CVE-2026-77903 (Microsoft Dataverse, CVSS 9.0) and CVE-2026-69843 (Microsoft Fabric, CVSS 10.0). The attack surface has broadened from authentication concerns to encompass trust in AI endpoints, data storage locations, and billing verification processes. Seven out of the ten vulnerabilities are unauthenticated, and all issues were addressed through server-side fixes by Microsoft. The extensive range of affected services suggests these vulnerabilities indicate a shared architectural dependency on authentication logic.
Windows 11 requires drivers to be digitally signed, a policy aimed at enhancing security by preventing unauthorized code from executing at the kernel level. This requirement, which began with Windows Vista and became mandatory with Windows 10, version 1607, has tightened over the years, especially with the introduction of UEFI Secure Boot and TPM in Windows 11. While this enforcement protects against malware and supports anti-cheat systems in gaming, it limits user autonomy and imposes significant challenges for developers, particularly those working on smaller projects. In contrast, Linux allows users more freedom to modify their systems, though this flexibility can compromise security.
A young gamer known as Mighty Mike Plays has claimed to have accumulated over ,000 in credit card debt on his father's company card due to expenditures related to promoting his Minecraft gaming account. His father, Dave, has stated that he was unaware of these charges and that the family is facing financial repercussions, including Dave's reported job termination. They have since launched a merchandise store to help recover the losses. However, skepticism regarding the authenticity of their claims has emerged, with critics suggesting inconsistencies in their narrative. Additionally, Dave has threatened legal action against those questioning their story.
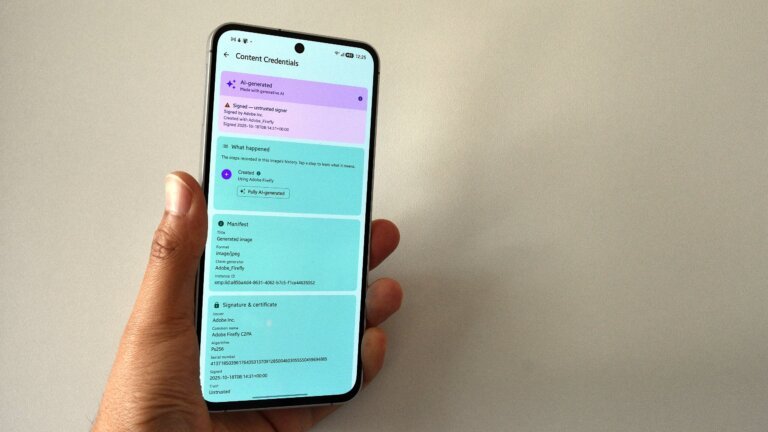
Generative AI is becoming a crucial part of various services and applications, leading to a series that will highlight notable AI innovations. A challenge for users is distinguishing between authentic and AI-generated content, which has become increasingly difficult. The C2PA Verify app helps users identify image origins by reading C2PA credentials, although these credentials can be erased, limiting the app's effectiveness. C2PA Verify is open-source, free, and developed by Dark Rock Studios.
Other noteworthy AI applications include:
- Retirement Planner: A web app powered by Claude Opus 4.5 that assists users in financial planning for retirement by calculating future portfolio value, drawdown rates, and tax implications, tailored for US and Canadian citizens.
- Memoria: An Android gallery app that uses offline AI for natural language search, ensuring user privacy by keeping data on the device. It utilizes Apple’s MobileCLIP-S0 model for processing queries and is open-source and free to use.
86Box is an emulator that meticulously reconstructs vintage PCs, allowing users to boot operating systems like MS-DOS, Windows 95, Windows 98, and Windows XP. The latest version, 6.0, was released on May 31, 2026, featuring a native Windows ARM64 build and discontinuing support for macOS 10.13 High Sierra. It has approximately 2,400 monthly searches in the U.S., indicating a demand for setup guides among enthusiasts. Unlike DOSBox, which creates a generic DOS environment, 86Box emulates specific hardware components for authentic execution of various operating systems. Originally a fork of PCem, 86Box has expanded its supported motherboards and developed a community of contributors. Version 6.0 has established it as the preferred choice for retro-PC builders in 2026.
Before installation, users need a minimum of a 64-bit Intel Core 2, AMD Athlon 64, or ARMv8 CPU, 4 GB of RAM, and a compatible host operating system. The installation process involves downloading the appropriate build, sourcing a legal ROM set, and configuring the virtual machine using the 86Box Manager. Users can select specific graphics cards and sound hardware to replicate the original systems accurately. The setup requires installation media for the guest operating system, which must be sourced legally.
Common pitfalls during setup include ensuring the BIOS ROM is available, matching CPU speed to software era, and installing the correct drivers. A properly configured virtual machine should display a BIOS POST screen and boot the selected operating system. Troubleshooting common issues often involves checking for missing ROMs, uninstalled drivers, or performance settings. 86Box is open-source and legal to use, but users must ensure they have legitimate licenses for any software used within the emulator.
A nine-year-old boy named Mike created a YouTube channel called "Mighty Mike Plays" and, with his father's initial support, launched a modest advertising campaign. However, Mike independently escalated the budget to ,000 using his father's corporate credit card, resulting in significant charges. This led to his father, Dave, losing his job and facing financial difficulties. The situation has garnered over three million views online, but some skepticism exists regarding its authenticity, particularly due to Dave promoting merchandise instead of seeking direct financial help. The incident raises concerns about financial literacy among children and parents in the digital age, especially related to online spending and microtransactions in gaming.
ESG reporting standards are becoming increasingly important in mobile technology, affecting various aspects such as data management, material sourcing, energy consumption, privacy, supply chain dynamics, and product accountability. The lifecycle of mobile devices involves raw material sourcing, component manufacturing, device assembly, shipping, marketing, sales, updates, repairs, trade-ins, and disposal. Companies must understand ESG standards to create coherent sustainability narratives and may need to disclose supplier practices, carbon emissions, and governance documentation when partnering with larger firms.
Consumers are now asking more questions about the longevity of software updates, repairability, data collection, packaging design, and the accountability of product creators. The rise of connected devices complicates ESG reporting due to extended product lifecycles and the need for ongoing software support. Companies should track product lifespan estimates, warranty data, repair trends, and update schedules to improve product quality and ESG reporting credibility.
Emerging tech companies can start their ESG journey by cataloging product claims, consolidating evidence, designating ownership of records, and reviewing product lifecycle information. Global sustainability frameworks exist but may not align with consumer needs for straightforward product information. Successful mobile tech companies will need to bridge formal reporting requirements with accessible product-level communication. Trust and transparency in practices will increasingly influence consumer choices in mobile technology.
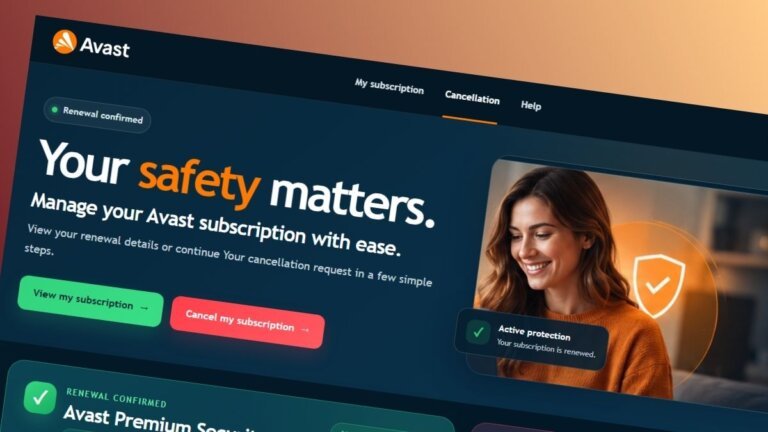
Antivirus renewal scams often begin with messages claiming automatic subscription renewals, leading victims to counterfeit pages designed to collect personal information. These scams impersonate well-known brands and do not indicate that the sender has accessed the recipient's device. Responding to such messages can provide scammers with valuable data, including names and phone numbers, which can be sold or used for further scams.
A specific scam site impersonating Avast targeted users in Belgium, falsely claiming a subscription renewal for €129.99. The site appeared polished and requested basic contact information without asking for sensitive data. It contained notes suggesting AI involvement in its creation, indicating it was a half-finished project.
To identify antivirus renewal scams, individuals should verify any claimed charges directly with their bank, check subscriptions through official channels, be cautious of cancellation forms requesting phone numbers, treat follow-up calls as potential threats, and avoid installing remote access software. If engagement with a scam occurs, disconnect from the internet, remove any installed software, and change passwords. Tools like Malwarebytes Browser Guard can help block malicious sites, and Scam Guard can analyze suspicious communications.
Altered applications and games for Android devices are often distributed as APK files, which need to be manually downloaded and installed. Reliable APK sources should provide essential details about the app, such as name, version number, file size, last update date, Android compatibility, installation instructions, user contact information, terms of use, disclaimers, and a privacy policy. Users are advised to download open-source applications directly from developers’ official websites or verified code repositories. F-Droid is a platform for original APK files, while HappyMod offers a variety of modified applications and games. User feedback on HappyMod indicates ease of installation and satisfactory performance, but independent evaluations are recommended. Before installing any APK, users should scan it with updated security software, ensure Google Play Protect is enabled, and scrutinize requested permissions. Users should avoid websites with excessive redirects or ambiguous payment forms.