cybersecurity

AppWizard
September 14, 2026
Malicious Android applications are being promoted through social media advertisements, particularly on platforms like Instagram and Facebook, posing significant risks to users. The Indian Cyber Crime Coordination Centre (I4C) has warned about deceptive apps advertised under names such as Night Play, Reloop, Kyss, Vimo, Rivo, Nezo, and Vixa, which often redirect users to pornographic websites to download APK files. These applications can exploit sensitive device permissions, leading to malware infections, unauthorized financial transactions, and various forms of cyber fraud. Users may be tricked into granting accessibility permissions that allow the malware to operate in the background and potentially install a VPN, rerouting internet traffic through servers controlled by attackers. Cybersecurity experts advise users to verify the legitimacy of applications before installation and to be cautious of permissions requested by unknown apps.
Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
AppWizard
September 11, 2026
The Cybersecurity and Infrastructure Security Agency (CISA) warned of a critical vulnerability in NetScaler, identified as CVE-2026-19490, with a CVSS score of 9.3, which has been exploited and affects all NetScaler ADC and Gateway appliances. Citrix has patched this vulnerability as of August 19. AdaptHealth reported a data breach affecting over 4.1 million individuals, compromising personal, health, and insurance information, but not Social Security numbers or financial data. A new strain of Android malware, MantaxOtax, attributed to Indonesian threat actors, combines ransomware and spyware, stealing sensitive information and affecting older Android versions. The Gigabud banking trojan has evolved to evade detection by installing a secondary app that hides the malicious application. CISA acting director Nick Andersen emphasized the need for swift adaptation to cybersecurity threats and highlighted staffing improvements within CISA. Russian e-commerce giant Wildberries experienced disruptions from a DDoS attack affecting payments to sellers, following claims of a cyber operation by Ukraine's military intelligence. McKesson faced a cyberattack exposing sensitive data of 6.4 million individuals, with the ShinyHunters group releasing this data after a failed extortion attempt. IDScan confirmed a data breach affecting 150 million individuals, resulting in the theft of personally identifiable information and government-issued documents.
Tech Optimizer
September 10, 2026
If an organization holds Microsoft 365 E5, it already has access to Microsoft Defender for Endpoint. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly management. CrowdStrike is preferred for those with a mature Security Operations Center (SOC) and sufficient budget. The choice of endpoint protection depends on specific organizational needs. Business endpoint protection integrates various technologies to defend against malware and attacks on devices. Organizations should assess their current situation before selecting a solution. Key recommendations include: - Microsoft Defender for Endpoint for organizations already using Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a funded SOC. - SentinelOne for mid-sized organizations needing automation. - ESET for those with older hardware or virtual desktops. - Avast Business for very small businesses lacking IT staff. - VIPRE for budget-conscious organizations needing straightforward coverage. - Expel for organizations wanting managed detection across diverse environments. Organizations should avoid running multiple real-time agents simultaneously and ensure prevention features are activated. Testing should prioritize line-of-business applications, and rollout procedures should be defined before going live. It’s essential to verify update staging and rollback procedures with vendors and confirm existing licenses to avoid unnecessary purchases.
Winsage
September 10, 2026
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has expanded its Known Exploited Vulnerabilities (KEV) catalog, adding critical vulnerabilities that need immediate attention. 1. CVE-2026-75650: A vulnerability in Adobe Commerce and Magento with a CVSS score of 10.0, allowing unauthenticated remote code execution. Affected versions include Magento Open Source releases 2.4.7, 2.4.8, and 2.4.9. It has been actively exploited since September 4. 2. CVE-2026-81963: A Microsoft Windows vulnerability with a CVSS score of 7.8, related to a link-following issue within the Update Stack, allowing local attackers to escalate privileges. It is currently being exploited. 3. CVE-2026-85880: Another Microsoft Windows vulnerability rated at 7.8, involving a heap-based buffer overflow in the ALPC component, permitting local privilege escalation. This flaw is also actively exploited. 4. CVE-2026-86218: A N-able N-central vulnerability with a CVSS score of 10.0, allowing pre-authenticated remote code execution. N-able has released an emergency hotfix for this issue. Federal agencies must address these vulnerabilities by specified deadlines: Windows flaws by September 22 and other vulnerabilities by September 11, 2026, in accordance with Binding Operational Directive (BOD) 22-01. Private organizations are advised to review the KEV catalog and take necessary actions to strengthen their infrastructure against these vulnerabilities.
AppWizard
September 10, 2026
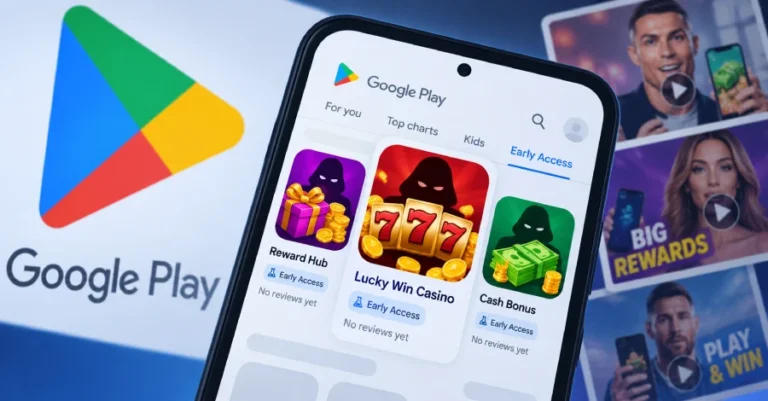
Bad actors are exploiting Google Play's Early Access program to distribute misleading applications that promise money, rewards, and casino winnings. This program allows developers to gather user feedback on unreleased apps but lacks public reviews or star ratings, enabling malicious actors to launch numerous fraudulent applications without immediate scrutiny. An example is the app "Vice Streets: Open World," which mimics Grand Theft Auto, has over 1 million downloads, and recently disappeared from the store without reviews or ratings. These deceptive apps are often promoted on social media with misleading advertisements and promise cash rewards, but users face obstacles when trying to withdraw their earnings. The primary goal of these apps is to generate revenue through excessive advertisements while circumventing regulatory requirements for legitimate gambling apps. Additionally, various malware families targeting Android devices have emerged, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory's use of the Gigabud banking trojan, highlighting ongoing security threats in the digital landscape.
Tech Optimizer
September 10, 2026
If you hold Microsoft 365 E5, you have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly platform. CrowdStrike is suggested for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses, VIPRE for budget-conscious mixed estates, and Expel for tool-agnostic managed detection and response. Antivirus and EDR are now unified under a single agent, and organizations should inquire about update staging processes to avoid issues like those experienced in July 2024 with a major vendor's faulty content update. Independent tests from organizations like AV-Comparatives and AV-TEST are crucial for evaluating protection rates and false positives. Linux servers require attention as they are often targeted by ransomware. When deploying endpoint protection, avoid running two real-time agents simultaneously, activate prevention features promptly, and test deployments on critical applications first. Organizations should confirm their Microsoft licensing covers necessary features and ensure there is a plan for responding to alerts. Common pitfalls include neglecting identity management and failing to test response workflows before incidents occur.
Tech Optimizer
September 10, 2026
Apple provides built-in security features for macOS, including XProtect, Gatekeeper, and automatic malware removal, which contribute to the safety of Macs. However, these protections do not effectively address threats like infostealers, phishing, and adware. For enhanced security, third-party antivirus solutions are recommended. Bitdefender is noted for its strong detection rates and minimal system impact, making it suitable for most users. Intego specializes in Mac-specific threats and is ideal for users focused solely on Apple products. ESET and Trend Micro are recommended for businesses needing centralized management. F-Secure is recognized for its privacy-focused approach, while Norton offers a comprehensive suite of security features. AVG provides free real-time protection suitable for low-risk personal use, but may not be adequate for business needs. CleanMyMac is a maintenance tool rather than a traditional antivirus, focusing on system cleanup and optimization. Users should avoid running multiple real-time scanners simultaneously and ensure they purchase appropriate licenses for business use. It's important to evaluate the necessity of additional features and consider long-term pricing when selecting antivirus software.
Winsage
September 10, 2026
On September 8, 2026, Microsoft released 966 security updates, the largest Patch Tuesday to date, addressing various vulnerabilities. Among these, 105 were classified as critical, including two zero-day vulnerabilities: CVE-2026-81963 and CVE-2026-85880. Both allow authorized local attackers to escalate privileges to SYSTEM level. CVE-2026-81963 is related to the Windows Update Stack, while CVE-2026-85880 involves a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC). The updates included 438 vulnerabilities related to privilege escalation, 258 concerning remote code execution, and 173 involving information disclosures. Users are advised to prioritize the installation of these updates due to the potential exploitation of the two critical vulnerabilities.
Winsage
September 10, 2026
Microsoft's Patch Tuesday on September 8, 2026, addressed two critical Windows privilege escalation vulnerabilities: CVE-2026-85880 and CVE-2026-81963, both with a CVSS score of 7.8. CVE-2026-85880 is a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC), allowing attackers with low-privilege local access to escalate privileges to SYSTEM. CVE-2026-81963 involves improper link resolution in the Windows Update Stack, enabling similar privilege escalation. Both vulnerabilities require no user interaction and have been actively exploited prior to the patch release. CISA added them to its Known Exploited Vulnerabilities catalog on September 8, 2026, with a remediation deadline of September 22 for U.S. federal agencies. CVE-2026-85880 affects various Windows 10 and Server versions but excludes Windows 11 and Windows Server 2025. CVE-2026-81963 impacts newer Windows platforms, including Windows 11 and Windows Server 2025. Microsoft released security updates for both vulnerabilities on September 8, 2026, and organizations are advised to prioritize these updates. Security teams should monitor for signs of privilege escalation and unusual SYSTEM-level activities related to these vulnerabilities.
Search