processes

AppWizard
October 2, 2026
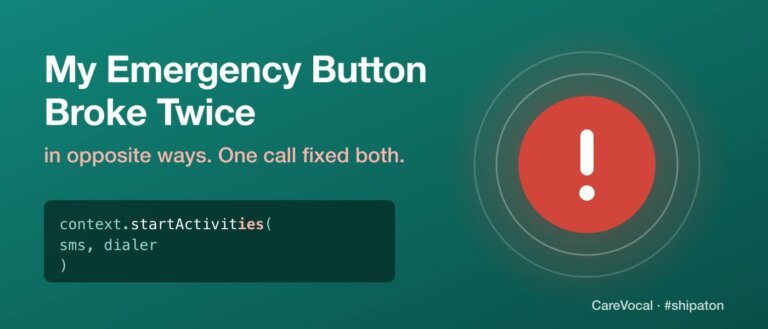
An Android application named CareVocal (internally referred to as CareBridge) was developed to facilitate communication for the user's mother living in a village. The app features three buttons: green for "feeling good," yellow for "something hurts," and red for "need help." Tapping the red button triggers three actions: saving an entry for her doctor, generating a pre-filled SMS to trusted contacts, and opening the phone dialer with the local emergency number pre-typed. The app requires the user to confirm sending the SMS and calling the emergency number to comply with Google Play's restrictions. During testing, issues arose where the SMS draft would not appear if the dialer was opened first, leading to adjustments in the code. A method was implemented to launch multiple intents simultaneously, ensuring that the SMS draft and dialer could be accessed without conflicts. Additionally, the recording feature was modified to start only after a second tap on the red button, separating it from the alert process to avoid distractions during emergencies. The app does not collect location data and is designed solely for logging and communication without diagnostic capabilities.
Winsage
October 1, 2026
Microsoft has announced that Windows settings backup will now be enabled by default on eligible Windows 11 version 26H2 devices. This feature, previously known as Windows Backup for Organizations, automatically preserves users’ Windows settings and Microsoft Store app lists, facilitating restoration after device resets, replacements, or reimages. The change aims to minimize disruptions during device recovery and ensures more devices have recovery data readily available. Administrators will still control the restore process, which requires explicit configuration. The default-on behavior applies only to Windows 11 version 26H2 or later, devices with the backup policy in a “Not Configured” state, and excludes certain environments. Administrators can disable the backup feature if necessary.
AppWizard
September 30, 2026
New video game releases this week include "Minecraft Dungeons II" on Tuesday and "Ace Combat 8: Wings of Theve" on October 2. "Minecraft Dungeons II" allows players to explore a new dimension called the Sift, either solo or with up to three friends. "Ace Combat 8" features aerial combat in the alternate-universe Earth of Strangereal, where players defend against an invasion. Analysts predict that AI tools could significantly reduce game development costs, potentially unlocking billions in profits for developers. Global consumer spending on video games is projected to reach 0 billion this year, with billion reinvested in development. "Grand Theft Auto VI" is set for a November 2026 launch, having been in development since 2018.
AppWizard
September 29, 2026
Transaction Network Services (TNS) has launched a capability called Bring Your Own App (BYOA) for operators in the payment industry, allowing them to create and deploy customer-facing applications on TNS's Android-based unattended payment terminals. BYOA simplifies payment processing, compliance, and certification by managing card capture, PIN collection, encryption, EMV processing, and payment certification. Each operator's application must be approved and signed by TNS before execution on the terminal. This model enables operators to focus on enhancing customer experiences without the usual security and compliance burdens. BYOA is available across TNS's Android-based unattended payment terminal platform, including retail and fuel payment terminals.
Tech Optimizer
September 29, 2026
Traditional antivirus software relies on a signature-based model that compares files against a database of known malware, which limits its effectiveness against modern threats. Cybercriminals have adapted by using polymorphic malware and fileless techniques that evade detection. Endpoint Detection and Response (EDR) continuously monitors device activities, tracking process activity, network connections, and file changes to detect behavioral patterns indicative of attacks. EDR also enables rapid response actions, such as isolating affected devices and terminating malicious processes. Small and medium businesses are increasingly targeted by attackers who exploit the limitations of traditional antivirus solutions. Relying solely on antivirus software creates vulnerabilities, making it essential for organizations to incorporate EDR for enhanced security.
Tech Optimizer
September 28, 2026
Two newly identified Critical CVEs have expanded Microsoft's September identity infrastructure vulnerabilities to over ten verified weaknesses across more than ten distinct services. The Azure Database for PostgreSQL is vulnerable to CVE-2026-85878, an Improper Authorization flaw (CWE-285) with a CVSS score of 9.9. Azure Billing is impacted by CVE-2026-62874, which presents an Insufficient Data Authenticity Verification issue (CWE-345) with a CVSS score of 10.0. Both vulnerabilities were disclosed on September 18 and validated by Tenable and MITRE. CVE-2026-85878 allows an authorized attacker to elevate privileges over the network with minimal complexity, while CVE-2026-62874 requires no authentication, enabling unauthenticated attackers to jeopardize financial integrity. The vulnerability cluster first emerged during the Patch Tuesday cycles on September 3 and September 8, with initial reports highlighting critical flaws in core services. Other September disclosures include CVE-2026-83711 (Azure AD B2C, CVSS 10.0), CVE-2026-70352 (Azure AI Language, CVSS 10.0), CVE-2026-83941 (Entra ID, CVSS 9.9), CVE-2026-62916 (Entra ID, CVSS 9.1), CVE-2026-69857 (Azure Cosmos DB, CVSS 8.5), and CVE-2026-69854 (Spring Cloud Azure, CVSS 9.0). Activity heightened between September 17 and 18 with the introduction of CVE-2026-77903 (Microsoft Dataverse, CVSS 9.0) and CVE-2026-69843 (Microsoft Fabric, CVSS 10.0). The attack surface has broadened from authentication concerns to encompass trust in AI endpoints, data storage locations, and billing verification processes. Seven out of the ten vulnerabilities are unauthenticated, and all issues were addressed through server-side fixes by Microsoft. The extensive range of affected services suggests these vulnerabilities indicate a shared architectural dependency on authentication logic.
Search