Enterprise

Winsage
September 16, 2026
Microsoft will unveil its vision for the future of personal computing at an event in San Francisco on October 7 at 10 a.m. Pacific time, focusing on the role of on-device artificial intelligence in Windows and Surface hardware. Key figures including CEO Satya Nadella and NVIDIA CEO Jensen Huang will discuss innovations across Windows, NVIDIA RTX Spark, and the PC ecosystem. The RTX Spark platform, introduced earlier this year, features a system-on-a-chip with 128GB of memory, an NVIDIA GPU, and an Arm-based CPU for high-performance AI workloads. Microsoft has announced the Surface Laptop Ultra, built on the RTX Spark platform, but details on pricing and release dates are not yet available. The event will emphasize how local AI will shape the future of PCs, with a focus on hardware capable of running AI models directly on devices. Attendees can also expect enhancements to the Windows operating system, though a surprise announcement regarding Windows 12 is unlikely. The event will be streamed live, starting at 10 a.m. PT and 1 p.m. ET.
Winsage
September 15, 2026
Microsoft announced on September 14 that the Windows 11 24H2 edition, including Home and Pro versions, has only 30 days of support remaining, with a deadline for updates set for October 13, 2026. Users are encouraged to upgrade to version 25H2 or later to continue receiving security updates. The Enterprise and Education editions will have support until October 12, 2027. Users have reported issues from September's security updates, particularly with the Office patch KB5002914, which disrupts the copy-and-paste function in Excel across multiple versions. Microsoft has acknowledged the issue but has not yet released a fix. A temporary workaround involves manually removing the problematic patch, though this also removes the associated security fixes. Additionally, users have experienced connection drops and unresponsiveness in Remote Desktop Services (RDS) across various Windows versions, including Windows 11 26H1 and Windows Server 2012. Microsoft confirmed that related tools may also stop responding, and restarting virtual machines may temporarily restore functionality. USB audio issues have been reported on certain USB Audio Class 1.0 devices across Windows 11 versions, with users experiencing loss of audio output and corrupted sound settings. Switching to 2-channel mode has helped some users, but Microsoft has not provided a timeline for a comprehensive fix. As Windows Server 2012 nears the end of its Extended Security Updates period on October 13, 2026, the RDS issues add pressure on administrators. Users on 24H2 need to prioritize migration to 25H2, while those with the latest updates should be cautious regarding Excel and Remote Desktop functionalities.
Winsage
September 15, 2026
Microsoft has released an emergency patch for Windows 11, identified as KB5129195, which is being automatically downloaded to address critical issues, including privilege elevation vulnerabilities. The patch fixes CVE-2026-62721 and resolves remote desktop connection problems, as well as attempts to address USB audio issues that arose after the September update. Improvements have been noted for 8-channel and 3D audio modes, but users may still face problems such as missing volume controls and lack of audio output for some USB audio devices. Additionally, unresolved issues from the September update, KB5124008, persist, particularly for AMD Radeon GPU users experiencing system freezes, crashes, and driver timeouts. Complaints about File Explorer crashing or failing to launch have also been reported, affecting certain enterprise environments. Microsoft is using internal AI tools to enhance security, but this has led to a cycle of instability in the operating system. Nearly 1,000 CVE patches were applied just before this update.
Tech Optimizer
September 14, 2026
The encryption landscape has shifted significantly, with Microsoft’s BitLocker and Apple’s FileVault becoming the primary free and integrated solutions for disk encryption. Organizations are encouraged to focus on comprehensive management capabilities rather than just acquiring encryption technology. Key management, compliance proof for auditors, and consistent policy enforcement across devices are critical. Native encryption solutions do not provide fleet-wide compliance, centralized key escrow, or advanced pre-boot authentication options. Various management models exist for different organizational needs, including options from Microsoft, Sophos, ESET, Trend Micro, Check Point, Trellix, WinMagic, Broadcom (Symantec), Dell, and Kaspersky. It is essential to ensure proper key management and recovery procedures before enforcing encryption to avoid data loss. Organizations should verify claims of compatibility and effectiveness of encryption solutions, especially regarding pre-boot authentication and cryptographic standards. Native encryption solutions are free, but management layers typically incur costs. Open-source solutions like VeraCrypt lack necessary management features, making them impractical for businesses.
Tech Optimizer
September 13, 2026
The landscape of encryption engines has stabilized, with Microsoft BitLocker and Apple FileVault being the primary solutions. As of 2026, the emphasis is on management rather than just acquiring encryption technology. Key management elements include audit proofing, key escrow and recovery, policy enforcement, and pre-boot options. Native encryption solutions lack features such as fleet-wide compliance proof, centralized key escrow, consistent policy enforcement, advanced pre-boot authentication, and removable-media encryption. Various management models are available for different environments, including: 1. Microsoft BitLocker with Intune: Free for Windows Pro/Enterprise, integrates with Entra ID for key management. 2. Sophos: Manages both BitLocker and FileVault from a single console. 3. ESET: Offers lightweight management and removable-media protection. 4. Trend Micro: Integrates encryption with DLP capabilities. 5. Check Point: Provides advanced pre-boot options and policy management. 6. Trellix: Comprehensive enterprise encryption suite with a complex management interface. 7. WinMagic: Focuses on cross-platform encryption and strong pre-boot options. 8. Broadcom (Symantec): Manages native engines within its broader security framework. 9. Dell: OEM-integrated encryption management for Dell hardware. 10. Kaspersky: Provides encryption management but is restricted in the U.S. Key considerations before deploying encryption include ensuring key escrow is in place, conducting recovery tests, and being mindful of removable media and server encryption. Common mistakes include using outdated freeware and not verifying key escrow. Organizations should request auditor reports for compliance verification and confirm claims of compatibility and pre-boot functionality. Native encryption engines are free, while management layers typically charge on a per-endpoint basis.
Winsage
September 13, 2026
32-bit Windows is commonly thought to be limited to 4GB of RAM due to its 32-bit address space, but this overlooks the role of Physical Address Extension (PAE), which allows access to more than 4GB of RAM on compatible processors. PAE enables 32-bit x86 processors to use 36-bit physical addresses. Windows allocates a 4GB virtual address space to each 32-bit application, with 2GB reserved for the application and 2GB for system use. Windows Server 2003 SP1 Enterprise can support up to 64GB of RAM, while the Datacenter edition can handle 128GB. Microsoft did not extend this capability to consumer editions due to the complexities and potential issues with hardware drivers, which often assume a 32-bit framework. Modifying drivers for PAE can be challenging, as incorrect assumptions about physical and virtual addresses can lead to memory corruption. To mitigate risks, Microsoft capped physical address space at 4GB in Windows XP SP2 and Windows Server 2003 SP1 Standard Edition. Server environments typically have more controlled hardware selections, allowing for the use of drivers that are tested for compatibility with addresses exceeding 4GB. Microsoft began discouraging the production of 32-bit systems in 2020 and ended 32-bit edition production with Windows 11.
Winsage
September 12, 2026
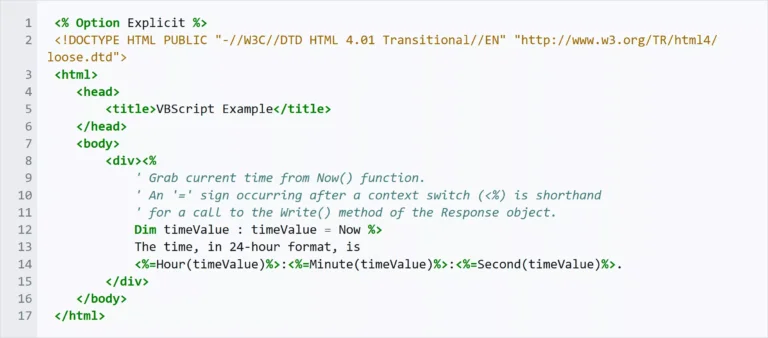
Microsoft is phasing out VBScript and urging organizations to transition to PowerShell. The Slmgr.vbs tool, used for managing Windows activation, will lose functionality as VBScript is deprecated. Slmgr.vbs allows users to install product keys, activate Windows, and check licensing status. VBScript will soon only be available as a Feature on Demand, requiring manual installation in future updates. PowerShell's OSLicense module offers similar capabilities to Slmgr.vbs for managing activation information. The OSLicense module is available for Windows 11 users after the August 2026 Preview update and will be supported in the next major release of Windows Server. Organizations are advised to review their existing scripts and tools to adapt to this transition.
Winsage
September 12, 2026
Microsoft introduced a feature called Cloud Rebuild with the release of Build 26220.9343 to the Beta channel on September 8, 2026. This tool allows users to download a fresh installation of Windows 11 from the internet, restoring the operating system and its drivers without needing removable media. The recovery process is conducted through the Windows Recovery Environment (WinRE), and users can access it by booting into WinRE or through Settings. For Cloud Rebuild to work, a healthy WinRE, internet access, a compatible networking driver, and local administrator credentials are required. The feature also enables the storage of Wi-Fi profiles in WinRE, allowing wireless-only setups to utilize cloud recovery. Cloud Rebuild is compatible with enterprise management tools like Intune and Windows Autopilot, but it is currently only available to Beta channel Insider participants for non-production evaluation.
Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Search